Question 81 · 407 in bank
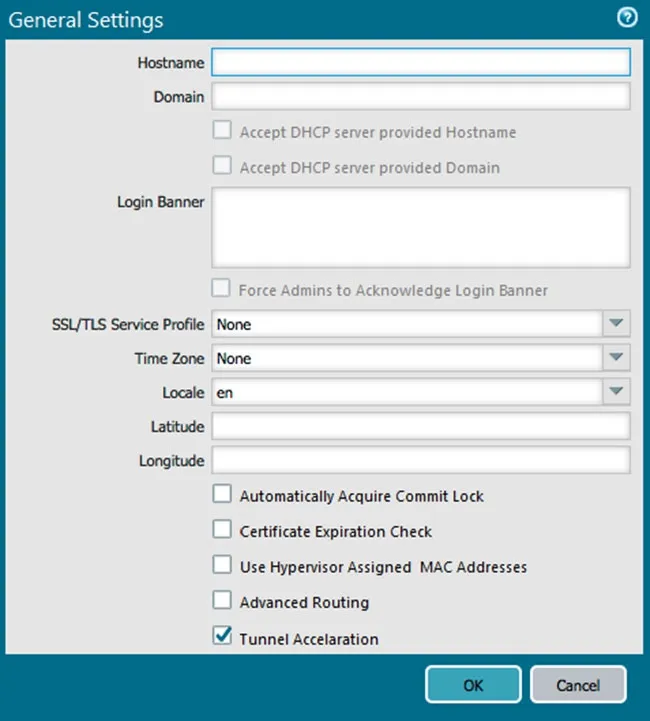
Based on the graphic, what is the purpose of the SSL/TLS Service profile configuration option?
Show answer
Answer: C
Explanation
Reference: https://knowledgebase.paloaltonetworks.com/KCSArticleDetail?id=kA10g000000ClFGCA0
Palo Alto Networks Certified Network Security Administrator407 questions across 41 pages are complete and free, with no account or card.
407 questions in this bank
Free access · progress saved on this device
Based on the graphic, what is the purpose of the SSL/TLS Service profile configuration option?
Answer: C
Reference: https://knowledgebase.paloaltonetworks.com/KCSArticleDetail?id=kA10g000000ClFGCA0
An administrator is troubleshooting an issue with traffic that matches the intrazone-default rule, which is set to default configuration. What should the administrator do?
Answer: A
key word is "default", Remember that in intrazone is disabled logging action and you cannot see any traffic log related. System log is not capable to show some log about traffic
Source: Adapted from community discussion — Alessandro1986
When is the content inspection performed in the packet flow process?
Answer: A
During the App-ID update process, what should you click on to confirm whether an existing policy rule is affected by an App-ID update?
Answer: B
When creating a custom URL category object, which is a valid type?
Answer: D
When HTTPS for management and GlobalProtect are enabled on the same interface, which TCP port is used for management access?
Answer: C
A company moved its old port-based firewall to a new Palo Alto Networks NGFW 60 days ago. Which utility should the company use to identify out-of-date or unused rules on the firewall?
Answer: D
exactly, for that reason it is the correct answer. If you choose the option of 30 days, some rule could be used within 30 to 60, therefore the answer that I assure that it has not been used for more than 60 days is the "D"
Source: Adapted from community discussion — LuisLfr
What two authentication methods on the Palo Alto Networks firewalls support authentication and authorization for role-based access control (RBAC)? (Choose two.)
Answer: AB
The administrative accounts are defined on an external SAML, TACACS+, or RADIUS server. The server performs both authentication and authorization. For authorization, you define Vendor-Specific Attributes (VSAs) on the TACACS+ or RADIUS server, or SAML attributes on the SAML server. PAN-OS maps the attributes to administrator roles, access domains, user groups, and virtual systems that you define on the firewall. For details, see:
Source: Adapted from community discussion — Oteslar
Which administrative management services can be configured to access a management interface?
Answer: C
The question is talking about "administrative management services" about the management interface not management interfaces. Tested in a lab: From PanOS 11.0 firewall go to Device -> Setup -> Interfaces -> Management -> Administrative Management -> Services - you will see these options : HTTP, HTTPS, TELNET, SSH. That is why the answer is C not A.
Source: Adapted from community discussion — drogadotcom
Which feature would be useful for preventing traffic from hosting providers that place few restrictions on content whose services are frequently used by attackers to distribute illegal or unethical material?
Answer: D
Keyboard:J Kmove between questionsA–Dselect an answerRshow or hide the answer← →change page
PCNSA practice, question 81. 407 questions available.
Version 1.0.0. How we source questions