Question 71 · 407 in bank
Which Security policy match condition would an administrator use to block traffic from IP addresses on the Palo Alto Networks EDL of Known Malicious IP Addresses list?
Show answer
Answer: B
Palo Alto Networks Certified Network Security Administrator407 questions across 41 pages are complete and free, with no account or card.
407 questions in this bank
Free access · progress saved on this device
Which Security policy match condition would an administrator use to block traffic from IP addresses on the Palo Alto Networks EDL of Known Malicious IP Addresses list?
Answer: B
URL categories can be used as match criteria on which two policy types? (Choose two.)
Answer: AB
There are many ways to enforce web page access beyond only blocking and allowing certain sites. For example, you can use multiple categories per URL to allow users to access a site, but block particular functions like submitting corporate credentials or downloading files. You can also use URL categories to enforce different types of policy, such as Authentication, Decryption, QoS, and Security.
Source: Adapted from community discussion — Oteslar
Given the screenshot, what are two correct statements about the logged traffic? (Choose two.)

Answer: BD
Entries for traffic that matches the URL Filtering profile attached to a security policy rule- will show as url Entries generated when traffic matches one of the Security Profiles attached to a security rule on the firewall- it will show as threat
Source: Adapted from community discussion — Jackie26
Refer to the exhibit. An administrator is using DNAT to map two servers to a single public IP address. Traffic will be steered to the specific server based on the application, where Host A (10.1.1.100) receives HTTP traffic and Host B (10.1.1.101) receives SSH traffic.
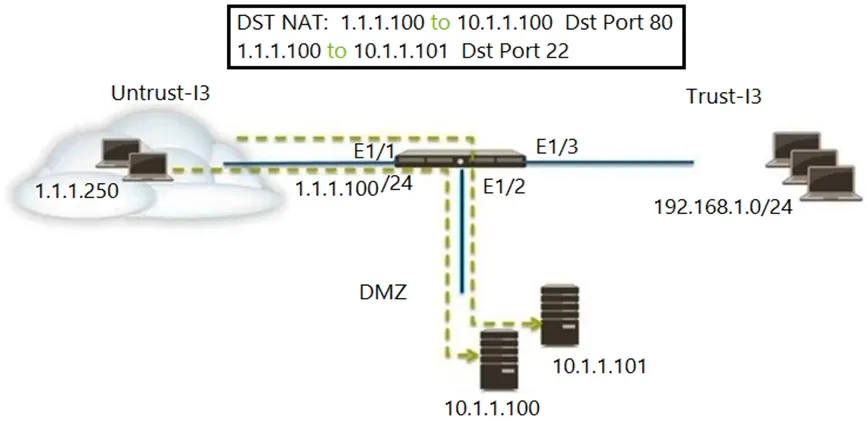
Which two Security policy rules will accomplish this configuration? (Choose two.)
Answer: AE
Which type of profile must be applied to the Security policy rule to protect against buffer overflows, illegal code execution, and other attempts to exploit system flaws?
Answer: B
Reference: https://docs.paloaltonetworks.com/pan-os/8-1/pan-os-web-interface-help/objects/objects-security-profiles-vulnerability-protection.html
Which interface does not require a MAC or IP address?
Answer: A
No IP or MAC addresses are assigned to Virtual Wire interfaces. No routing or switching is done on a Virtual Wire interface.
Source: Adapted from community discussion — darkonzy
Starting with PAN-OS version 9.1, application dependency information is now reported in which two locations? (Choose two.)
Answer: AC
Reference: https://docs.paloaltonetworks.com/pan-os/9-1/pan-os-admin/app-id/use-application-objects-in-policy/resolve-application-dependencies.html
What action will inform end users when their access to Internet content is being restricted?
Answer: D
Reference: https://docs.paloaltonetworks.com/pan-os/8-1/pan-os-web-interface-help/device/device-response-pages.html
What is a recommended consideration when deploying content updates to the firewall from Panorama?
Answer: A
The content release version on the Panorama management server must be the same (or earlier) version as the content release version on any Dedicated Log Collectors or managed firewalls. https://docs.paloaltonetworks.com/panorama/9-1/panorama-admin/set-up-panorama/install-content-and-software-updates-for-panorama/panorama-log-collector-firewall-and-wildfire-version-compatibility#id09d0b616-1197-4f80-be05-fdd7e75f8652
Source: Adapted from community discussion — TheMaster01
Which information is included in device state other than the local configuration?
Answer: D
Correct: Exports the firewall state information as a bundle. In addition to the running configuration, the state information includes device group and template settings pushed from Panorama.
Source: Adapted from community discussion — nolox
Keyboard:J Kmove between questionsA–Dselect an answerRshow or hide the answer← →change page
PCNSA practice, question 71. 407 questions available.
Version 1.0.0. How we source questions