Question 91 · 407 in bank
Which security policy match condition would an administrator use to block traffic to IP addresses on the Palo Alto Networks Bulletproof IP Addresses list?
Show answer
Answer: B
Palo Alto Networks Certified Network Security Administrator407 questions across 41 pages are complete and free, with no account or card.
407 questions in this bank
Free access · progress saved on this device
Which security policy match condition would an administrator use to block traffic to IP addresses on the Palo Alto Networks Bulletproof IP Addresses list?
Answer: B
Which three filter columns are available when setting up an Application Filter? (Choose three.)
Answer: BCE
Which stage of the cyber attack lifecycle makes it important to provide ongoing education to users on spear phishing links, unknown emails, and risky websites?
Answer: B
Weaponization and Delivery: Attackers will then determine which methods to use in order to deliver malicious payloads. Some of the methods they might utilize are automated tools, such as exploit kits, spear phishing attacks with malicious links, or attachments and malvertizing. Gain full visibility into all traffic, including SSL, and block high-risk applications. Extend those protections to remote and mobile devices. Protect against perimeter breaches by blocking malicious or risky websites through URL filtering. Block known exploits, malware and inbound command-and-control communications using multiple threat prevention disciplines, including IPS, anti-malware, anti-CnC, DNS monitoring and sinkholing, and file and content blocking. Detect unknown malware and automatically deliver protections globally to thwart new attacks. Provide ongoing education to users on spear phishing links, unknown emails, risky websites, etc.
Source: Adapted from community discussion — TheMaster01
A coworker found a USB labeled "confidential in the parking lot. They inserted the drive and it infected their corporate laptop with unknown malware The malware caused the laptop to begin infiltrating corporate data. Which Security Profile feature could have been used to detect the malware on the laptop?
Answer: C
The key word in the question = Detect Antivirus security profiles protect against viruses, worms, and trojans as well as spyware downloads. Answer A will indeed deal with the spyware when it kicks in and tries to do its stuff - but its Antivirus that detects it.
Source: Adapted from community discussion — Surfside92
What must be configured before setting up Credential Phishing Prevention?
Which DNS Query action is recommended for traffic that is allowed by Security policy and matches Palo Alto Networks Content DNS Signatures?
Answer: B
Which statement best describes a common use of Policy Optimizer?
Answer: B
for me is A Policy Optimizer identifies port-based rules so you can convert them to application-based allow rules or add applications from a port-based rule to an existing application-based rule without compromising application availability. https://docs.paloaltonetworks.com/pan-os/10-2/pan-os-admin/app-id/security-policy-rule-optimization
Source: Adapted from community discussion — innuendo2
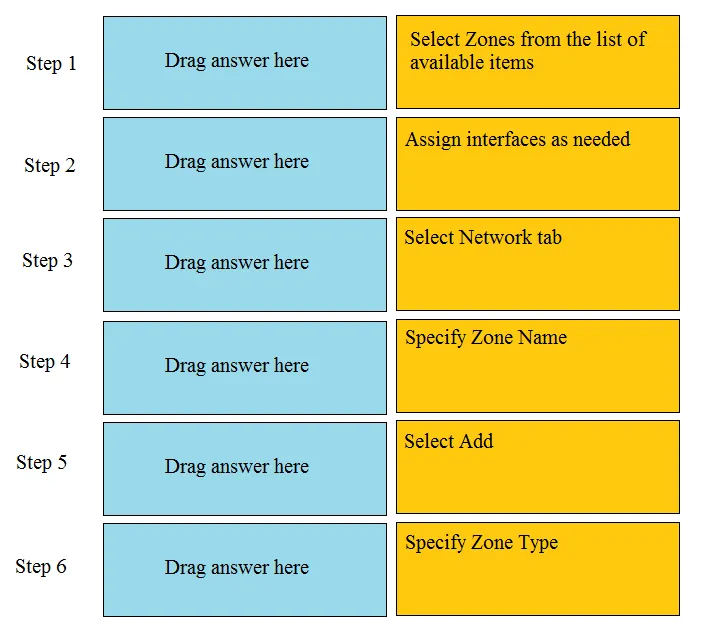
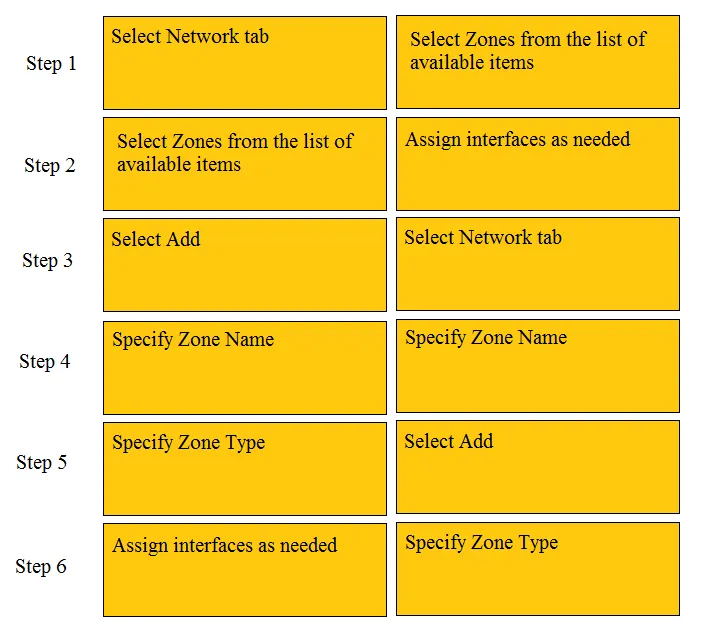
DRAG DROP - Order the steps needed to create a new security zone with a Palo Alto Networks firewall. Select and Place:
This is an interactive task on the real exam — a drag-and-drop, hotspot or ordering question. There is nothing to select here, so the answer is shown below for reference.
Answer: See figure below
Answer is Select Network Tab Select Zones from the list of available items Select Add Specify Zone Name Specify Zone Type Assign interfaces as needed
Source: Adapted from community discussion — Arch_Angel
An address object of type IP Wildcard Mask can be referenced in which part of the configuration?
Answer: A
The correct answer is You can use an address object of type IP Wildcard Mask only in a Security policy rule. https://docs.paloaltonetworks.com/pan-os/9-0/pan-os-web-interface-help/objects/objects-addresses IP Wildcard Mas
Source: Adapted from community discussion — Robert_99
You receive notification about a new malware that infects hosts. An infection results in the infected host attempting to contact command-and-control server. Which Security Profile, when applied to outbound Security policy rules, detects and prevents this threat from establishing a command-and-control connection?
Answer: A
Keyboard:J Kmove between questionsA–Dselect an answerRshow or hide the answer← →change page
PCNSA practice, question 91. 407 questions available.
Version 1.0.0. How we source questions