Question 41 · 407 in bank
A Security Profile can block or allow traffic at which point?
Show answer
Answer: C
Palo Alto Networks Certified Network Security Administrator407 questions across 41 pages are complete and free, with no account or card.
407 questions in this bank
Free access · progress saved on this device
A Security Profile can block or allow traffic at which point?
Answer: C
DRAG DROP - Place the following steps in the packet processing order of operations from first to last. Select and Place:

This is an interactive task on the real exam — a drag-and-drop, hotspot or ordering question. There is nothing to select here, so the answer is shown below for reference.
Answer: See figure below
Reference: https://knowledgebase.paloaltonetworks.com/KCSArticleDetail?id=kA10g000000ClVHCA0
Source: Adapted from community discussion — Bubu3k

Employees are shown an application block page when they try to access YouTube. Which security policy is blocking the YouTube application?
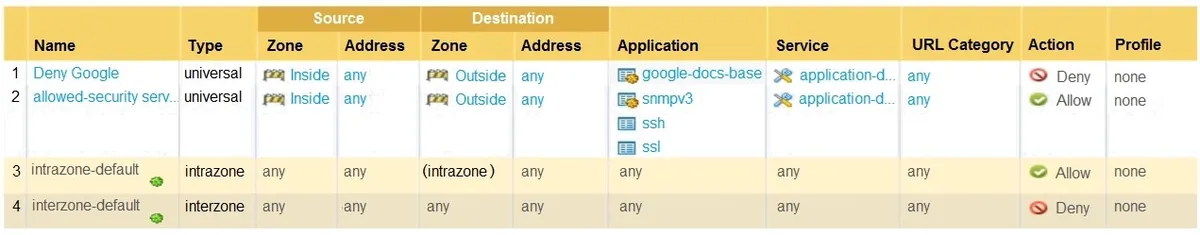
Answer: D
The application on the policy is google-docs-base. As it is different from google-base, B cannot be the right answer. D is correct
Source: Adapted from community discussion — delorean
Which type of address object is `10.5.1.1/0.127.248.2`?
Answer: C
Which component is a building block in a Security policy rule?
Answer: D
Reference: https://docs.paloaltonetworks.com/pan-os/9-0/pan-os-web-interface-help/policies/policies-security/building-blocks-in-a-security-policy-rule.html
You have been tasked to configure access to a new web server located in the DMZ. Based on the diagram what configuration changes are required in the NGFW virtual router to route traffic from the 10.1.1.0/24 network to 192.168.1.0/24?

Answer: C
C is correct answer. Destination is the web server, interface towards the router and next hop IP address of the routers interface connected to FW.
Source: Adapted from community discussion — H3kerman
An administrator would like to use App-ID's deny action for an application and would like that action updated with dynamic updates as new content becomes available. Which security policy action causes this?
Answer: C
For clarification: each app has its own defualt deny-action listed in the database. If the deny option is selected in the policy rue, then this default action will be used. Answer C is correct
Source: Adapted from community discussion — error_909
Selecting the option to revert firewall changes will replace what settings?
Answer: A
D is correct The question does not specify the type of revert mode. Therefore, the answer cannot be specific, but a more general one!
Source: Adapted from community discussion — hatus
An administrator has configured a Security policy where the matching condition includes a single application, and the action is drop. If the application's default deny action is reset-both, what action does the firewall take?
Answer: A
Deny Action App-IDs are developed with a default deny action that dictates how the firewall responds when the application is included in a Security policy rule with a deny action. The default deny action can specify either a silent drop or a TCP reset. You can override this default action in Security policy.
Source: Adapted from community discussion — jbas
Which three types of authentication services can be used to authenticate user traffic flowing through the firewall's data plane? (Choose three.)
Answer: ABD
PAN-OS software supports the following authentication types: • None • Local Database • RADIUS • LDAP • TACACS+ PALO ALTO NETWORKS: PCNSA Study Guide 106 • SAML • Kerberos
Source: Adapted from community discussion — H3kerman
Keyboard:J Kmove between questionsA–Dselect an answerRshow or hide the answer← →change page
PCNSA practice, question 41. 407 questions available.
Version 1.0.0. How we source questions