Question 361 · 496 in bank
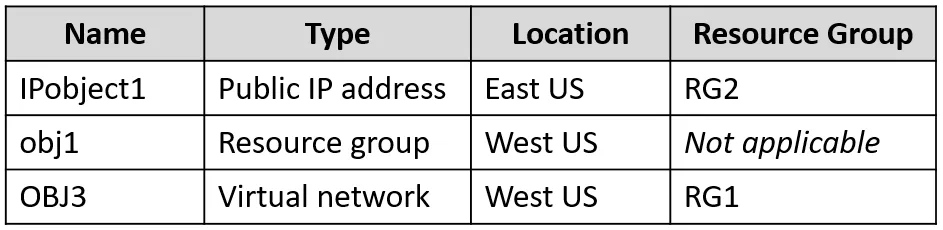
You have an Azure subscription that contains a managed identity named Identity1 and the Azure key vaults shown in the following table.

KeyVault1 contains an access policy that grants Identity1 the following key permissions: • Get • List • Wrap • Unwrap You need to provide Identity1 with the same permissions for KeyVault2. The solution must use the principle of least privilege. Which role should you assign to Identity1?
Show answer
Answer: A
Explanation
Why not Key Vault Crypto Service Encryption User "dataActions": [ "Microsoft.KeyVault/vaults/keys/read", List keys in the specified vault, or read properties and public material of a key. For asymmetric keys, this operation exposes public key and includes ability to perform public key algorithms such as encrypt and verify signature. Private keys and symmetric keys are never exposed. "Microsoft.KeyVault/vaults/keys/wrap/action", Wraps a symmetric key with a Key Vault key. Note that if the Key Vault key is asymmetric, this operation can be performed by principals with read access.javascript:void(0) "Microsoft.KeyVault/vaults/keys/unwrap/action" Unwraps a symmetric key with a Key Vault key.
Source: Adapted from community discussion — Nick66