Question 301 · 496 in bank
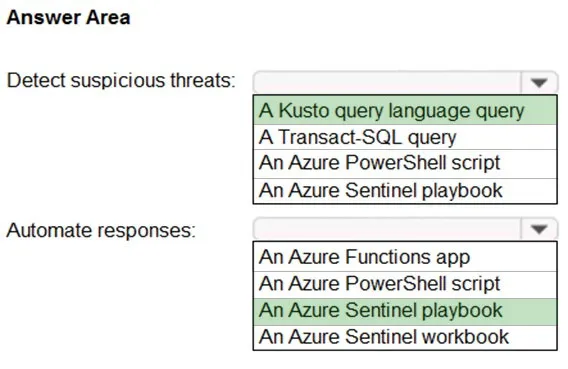
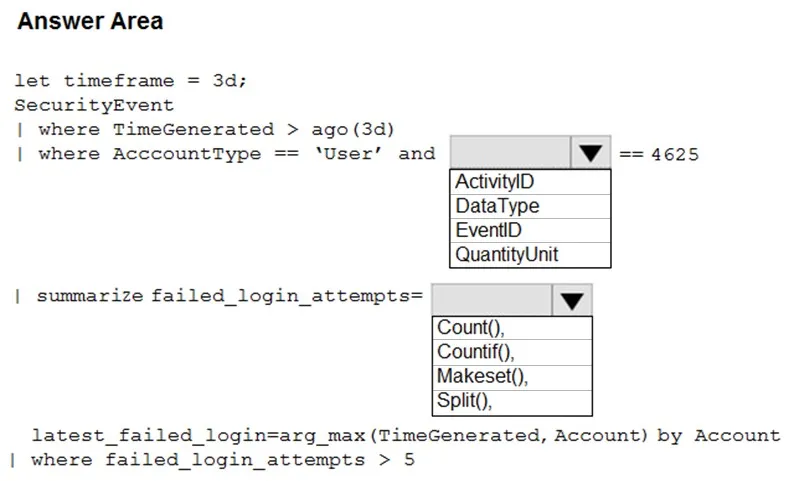
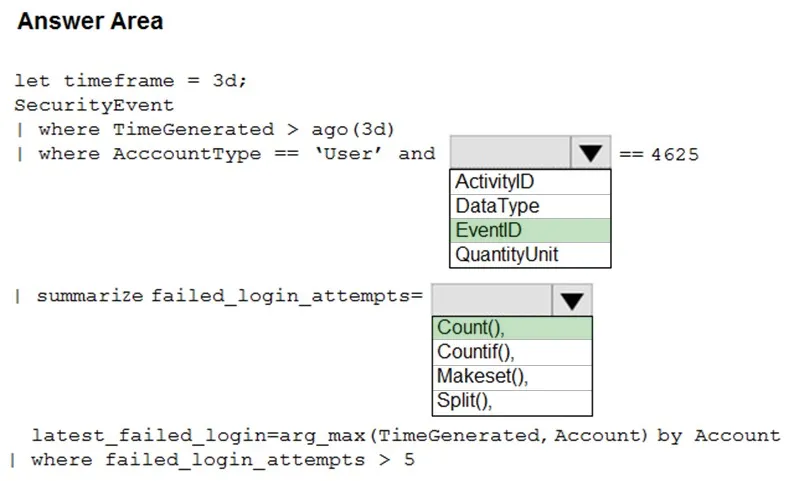
HOTSPOT - You plan to use Azure Sentinel to create an analytic rule that will detect suspicious threats and automate responses. Which components are required for the rule? To answer, select the appropriate options in the answer area. NOTE: Each correct selection is worth one point. Hot Area:
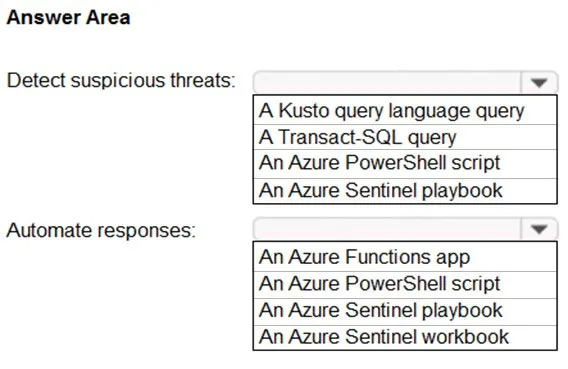
This is an interactive task on the real exam — a drag-and-drop, hotspot or ordering question. There is nothing to select here, so the answer is shown below for reference.
Show the answer figure
Answer: See figure below
Explanation
Reference: https://docs.microsoft.com/en-us/azure/sentinel/tutorial-detect-threats-custom https://docs.microsoft.com/en-us/azure/sentinel/tutorial-respond-threats-playbook
Source: Adapted from community discussion — Johnvic