Question 241 · 496 in bank
HOTSPOT - You have an Azure subscription that is linked to an Azure Active Directory (Azure AD). The tenant contains the users shown in the following table.

You have an Azure key vault named Vault1 that has Purge protection set to Disable. Vault1 contains the access policies shown in the following table.

You create role assignments for Vault1 as shown in the following table.

For each of the following statements, select Yes if the statement is true. Otherwise, select No. NOTE: Each correct selection is worth one point. Hot Area:

This is an interactive task on the real exam — a drag-and-drop, hotspot or ordering question. There is nothing to select here, so the answer is shown below for reference.
Show the answer figure
Answer: See figure below
Explanation
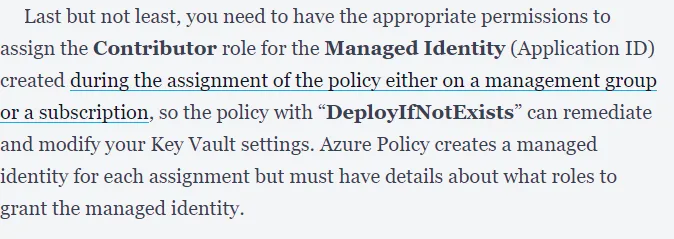
Box 1: No - Resource Policy Contributor or Security Administrator is required. User1 is Security Administrator only with the no specific permission granted to Vault1. The Security Admin can view and update permissions for Security Center. Same permissions as the Security Reader role and can also update the security policy and dismiss alerts and recommendations. However: Box 2: Yes - User2 is a Network Contributor, with Select All Key, Secret & Certificate permissions, and Key Vault Reader. The Network Contributor role lets you manage networks, but not access to them. Box 3: Yes - User3 is a Key Vault Contributor and a User Access Administrator for Vault. The Key Vault Contributor role allows you to manage key vaults, but does not allow you to assign roles in Azure RBAC, and does not allow you to access secrets, keys, or certificates. Reference: https://docs.microsoft.com/en-us/azure/role-based-access-control/built-in-roles#network-contributor https://charbelnemnom.com/enable-purge-protection-key-vault-azure-policy/
Source: Adapted from community discussion — juandmi
References