Question 321 · 334 in bank
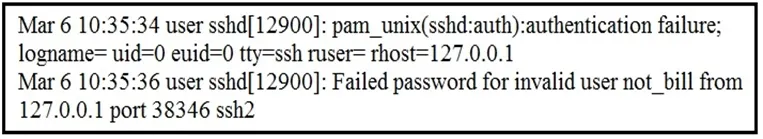
Refer to the exhibit. In which Linux log file is this output found?
Show answer
Answer: D
Understanding Cisco Cybersecurity Operations Fundamentals (CBROPS)334 questions across 34 pages are complete and free, with no account or card.
334 questions in this bank
Free access · progress saved on this device
Refer to the exhibit. In which Linux log file is this output found?
Answer: D
An engineer runs a suspicious file in a sandbox analysis tool to see the outcome. The analysis report shows that outbound callouts were made post infection. Which two pieces of information from the analysis report are needed to investigate the callouts? (Choose two.)
Answer: BE
The two pieces of information from the analysis report that are needed to investigate the outbound callouts are: B. Host IP addresses - this will give information about the destination of the callouts and can be used to identify potential malicious hosts. E. Domain names - this will give information about the domains contacted during the outbound callouts and can be used to identify potential command-and-control servers or other malicious infrastructure.
Source: Adapted from community discussion — drdecker100
An analyst is exploring the functionality of different operating systems. What is a feature of Windows Management Instrumentation that must be considered when deciding on an operating system?
Answer: D
"D" is correct. Windows Management Instrumentation (WMI) consists of a set of extensions to the Windows Driver Model that provides an operating system interface through which instrumented components provide information and notification. WMI is Microsoft's implementation of the Web-Based Enterprise Management (WBEM) and Common Information Model (CIM) standards from the Distributed Management Task Force (DMTF). https://en.wikipedia.org/wiki/Windows_Management_Instrumentation
Source: Adapted from community discussion — anonymous1966
What causes events on a Windows system to show Event Code 4625 in the log messages?
Answer: B
"B" is correct 4625(F): An account failed to log on. Event Description: This event generates if an account logon attempt failed when the account was already locked out. It also generates for a logon attempt after which the account was locked out. It generates on the computer where logon attempt was made, for example, if logon attempt was made on user’s workstation, then event will be logged on this workstation. This event generates on domain controllers, member servers, and workstations. https://docs.microsoft.com/en-us/windows/security/threat-protection/auditing/event-4625
Source: Adapted from community discussion — anonymous1966

Refer to the exhibit. What does the message indicate?
Answer: C
"C" is correct. Apache log format: LogFormat "%h %l %u %t \"%r\" %>s %b" Now let's break down what each section of that log means. %h The IP address of the client. %l The identity of the client determined by identd on the client's machine. Will return a hyphen (-) if this information is not available. %u The userid of the client if the request was authenticated. %t The time that the request was received. \"%r\" The request line that includes the HTTP method used, the requested resource path, and the HTTP protocol that the client used. %>s The status code that the server sends back to the client. %b The size of the object requested. Pay attention at \"%r\". The resource path is "-" that means "empty". So, the root of the site was requested.
Source: Adapted from community discussion — anonymous1966

Refer to the exhibit. This request was sent to a web application server driven by a database. Which type of web server attack is represented?
Answer: D
I think blind sql injection is correct Blind SQL (Structured Query Language) injection is a type of SQL Injection attack that asks the database true or false questions and determines the answer based on the applications response. https://owasp.org/www-community/attacks/Blind_SQL_Injection
Source: Adapted from community discussion — gnuga
A SOC analyst is investigating an incident that involves a Linux system that is identifying specific sessions. Which identifier tracks an active program?
Answer: D
Answer is correct. The process identifier (process ID or PID) is a number used by Linux or Unix operating system kernels. It is used to uniquely identify an active process. https://www.cyberciti.biz/faq/linux-find-process-name/
Source: Adapted from community discussion — gnuga
An offline audit log contains the source IP address of a session suspected to have exploited a vulnerability resulting in system compromise. Which kind of evidence is this IP address?
Answer: B
"B is correct. There are 3 types of evidences: Best: Do not need anything else. Corroborating: evidence that tends to support a theory or an assumption deduced by some initial evidence. Indirect: extrapolation to a conclusion of fact (such as fingerprints, DNA evidence, and so on) In this case the IP address would corroborate to some other evidence.
Source: Adapted from community discussion — anonymous1966

Refer to the exhibit. Which type of evidence is this file?
Answer: A
What is a difference between SIEM and SOAR security systems?
Answer: C
Keyboard:J Kmove between questionsA–Dselect an answerRshow or hide the answer← →change page
200-201 practice, question 321. 334 questions available.
Version 1.0.0. How we source questions