Question 301 · 334 in bank
Which security monitoring data type requires the largest storage space?
Show answer
Answer: D
Understanding Cisco Cybersecurity Operations Fundamentals (CBROPS)334 questions across 34 pages are complete and free, with no account or card.
334 questions in this bank
Free access · progress saved on this device
Which security monitoring data type requires the largest storage space?
Answer: D
What are two denial of service attacks? (Choose two.)
Answer: CD
C and D are correct A UDP flood is a type of denial-of-service attack in which a large number of User Datagram Protocol (UDP) packets are sent to a targeted server with the aim of overwhelming that device’s ability to process and respond. A Ping of death (PoD) attack is a denial-of-service (DoS) attack, in which the attacker aims to disrupt a targeted machine by sending a packet larger than the maximum allowable size, causing the target machine to freeze or crash. https://www.cloudflare.com/pt-br/learning/ddos/udp-flood-ddos-attack/ https://www.cloudflare.com/pt-br/learning/ddos/ping-of-death-ddos-attack/
Source: Adapted from community discussion — anonymous1966
An engineer needs to discover alive hosts within the 192.168.1.0/24 range without triggering intrusive portscan alerts on the IDS device using Nmap. Which command will accomplish this goal?
Answer: B
-sL (List Scan) The list scan is a degenerate form of host discovery that simply lists each host of the network(s) specified, without sending any packets to the target hosts. By default, Nmap still does reverse-DNS resolution on the hosts to learn their names. It is often surprising how much useful information simple hostnames give out. -sn (No port scan) This option tells Nmap not to do a port scan after host discovery, and only print out the available hosts that responded to the host discovery probes. This is often known as a “ping scan”, but you can also request that traceroute and NSE host scripts be run. This is by default one step more intrusive than the list scan, and can often be used for the same purposes. It allows light reconnaissance of a target network WITHOUT ATTRACTING MUCH ATTENTION. Knowing how many hosts are up is more valuable to attackers than the list provided by list scan of every single IP and host name. IN PREVIOUS RELEASES OF NMAP, -sn WAS KNOWN AS -sP. Correct answer is B Source: https://nmap.org/book/man-host-discovery.html
Source: Adapted from community discussion — mariodesa
Which open-sourced packet capture tool uses Linux and Mac OS X operating systems?
Answer: B
tcpdump Tcpdump is an open-source packet capture tool primarily used on Unix-like operating systems, including Linux and macOS. It allows users to capture and analyze network traffic for troubleshooting, monitoring, and security analysis purposes. Netsh is a Windows command-line utility, and SolarWinds and NetScout are software solutions that provide network monitoring and management but are not packet capture tools like tcpdump.
Source: Adapted from community discussion — AhmedAbdalla
An engineer must compare NIST vs ISO frameworks. The engineer decided to compare as readable documentation and also to watch a comparison video review. Using Windows 10 OS, the engineer started a browser and searched for a NIST document and then opened a new tab in the same browser and searched for an ISO document for comparison. The engineer tried to watch the video, but there was an audio problem with OS, so the engineer had to troubleshoot it. At first, the engineer started CMD and looked for a driver path, then looked for a corresponding registry in the registry editor. The engineer enabled "Audiosrv" in task manager and put it on auto-start, and the problem was solved. Which two components of the OS did the engineer touch? (Choose two.)
Answer: CE
An engineer configured regular expression ".*\.([Dd][Oo][Cc]|[Xx][LI][Ss]|[Pp][Pp][Tt]) HTTP/1.[01]" on Cisco ASA firewall. What does this regular expression do?
Answer: C
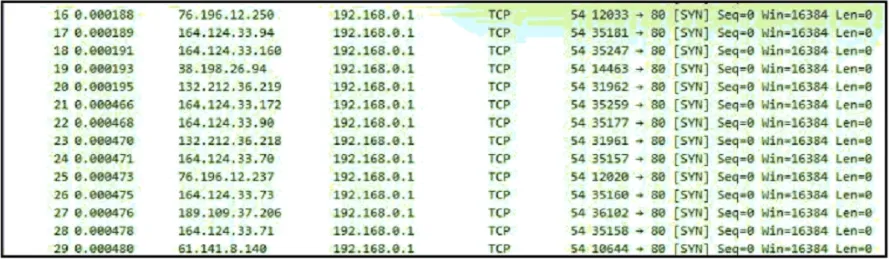
Refer to the exhibit. Which application-level protocol is being targeted?
Answer: C

Refer to the exhibit. Which kind of attack method is depicted in this string?
Answer: A
Cross-site scripting works by manipulating a vulnerable web site so that it returns malicious JavaScript to users. Key word: Java
Source: Adapted from community discussion — SecurityGuy
Which two components reduce the attack surface on an endpoint? (Choose two.)
Answer: AD
The two components that reduce the attack surface on an endpoint are: Secure boot: Secure boot is a process that ensures the integrity and authenticity of the firmware and operating system that are loaded on an endpoint device when it starts up. It helps prevent malicious code from being executed during the boot process, reducing the attack surface by ensuring only trusted software is run. Restricting USB ports: By restricting or disabling USB ports on an endpoint device, you can reduce the risk of malware being introduced through external devices like USB drives. This limits the attack surface by preventing unauthorized or potentially malicious USB devices from being connected to the endpoint. (full packet captures at the endpoint), (increased audit log levels), and (load balancing) are not directly related to reducing the attack surface on an endpoint.
Source: Adapted from community discussion — AhmedAbdalla
What is an attack surface as compared to a vulnerability?
Answer: B
From wikipedia, The attack surface of a software environment is the sum of the different points (for "attack vectors") where an unauthorized user (the "attacker") can try to enter data to or extract data from an environment.[1][2] [3]Keeping the attack surface as small as possible is a basic security measure. So as you said B is correct then, sorry for the confusion.
Source: Adapted from community discussion — beowolf
Keyboard:J Kmove between questionsA–Dselect an answerRshow or hide the answer← →change page
200-201 practice, question 301. 334 questions available.
Version 1.0.0. How we source questions