Question 291 · 334 in bank
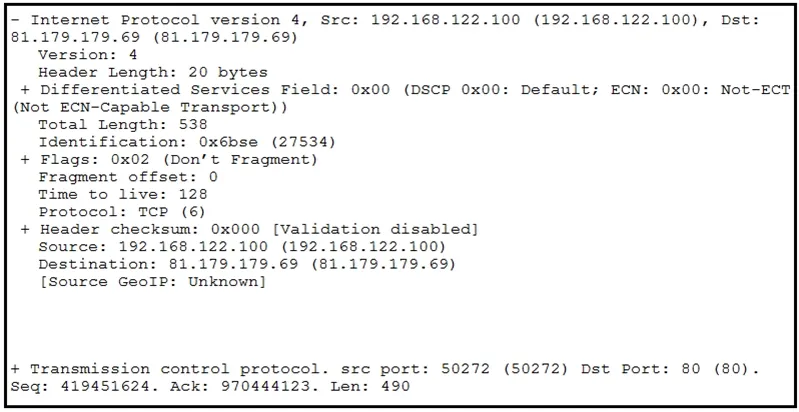
Refer to the exhibit. What should be interpreted from this packet capture?
Show answer
Answer: B
Understanding Cisco Cybersecurity Operations Fundamentals (CBROPS)334 questions across 34 pages are complete and free, with no account or card.
334 questions in this bank
Free access · progress saved on this device
Refer to the exhibit. What should be interpreted from this packet capture?
Answer: B
What are the two characteristics of the full packet captures? (Choose two.)
Answer: BE
"C" is correct. IP Reassembly IP Reassembly is a feature in Wireshark and TShark to automatically reassemble all fragmented IP Datagrams into a full IP packet before calling the higher layer dissector. Ref: https://wiki.wireshark.org/IP_Reassembly This feature will require a lot of extra memory to be consumed by wireshark in order to store the reassembly buffers and is disabled by default. "E" is correct. By the book: Packet captures provide a full historical record of a network transaction or an attack. It is important to recognize that no other data source offers this level of detail. There are many study of cases of using Wireshark to troubleshooting the cause of security and performance issues. So, "B" would also be right. But the other options are more direct.
Source: Adapted from community discussion — anonymous1966
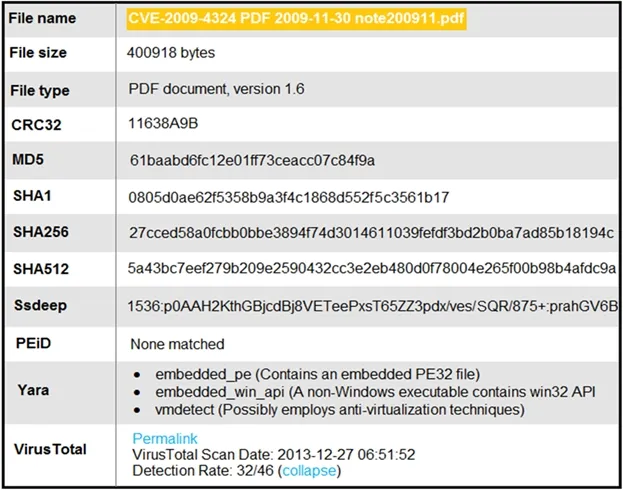
Refer to the exhibit. An engineer is analyzing this Cuckoo Sandbox report for a PDF file that has been downloaded from an email. What is the state of this file?
Answer: C
What is rule-based detection when compared to statistical detection?
Answer: B
A and D are not right because both detections have nothing to do with idenity. C is incorrect as statistical detection would concern with the likelihood so B is the correct answer.
Source: Adapted from community discussion — Leo_Visser
DRAG DROP - Drag and drop the technology on the left onto the data type the technology provides on the right. Select and Place:

This is an interactive task on the real exam — a drag-and-drop, hotspot or ordering question. There is nothing to select here, so the answer is shown below for reference.
Answer: See figure below
The correct answer is: StateFull Firewall, TCPDUMP, Cisco Umbrella, Snort StateFull Firewall --> Session data Session data is data about a network session that is usually established between two devices either on the same network or remote networks. Session data contains the following elements, which are used to identify the details within the network session: Source and destination IP addresses Source and destination service ports Layer 3 protocol details and code TCPDUMP --> full packet capture Cisco Umbrella (DNS) --> Transaction Data The actual data that is exchanged during a session is known as transaction data. The actual data that is being sent across the network. Snort (IDS) --> connection event Connection events – These events are generated when a device establishes a session with another device on the network. When a session is detected by NGIPS, it creates a connection log that contains all the information about the session/connection itself. Reference: Book Cisco Certified CyberOps Associate 200-201 Certification Guide - By Glen D. Singh
Source: Adapted from community discussion — anonymous1966

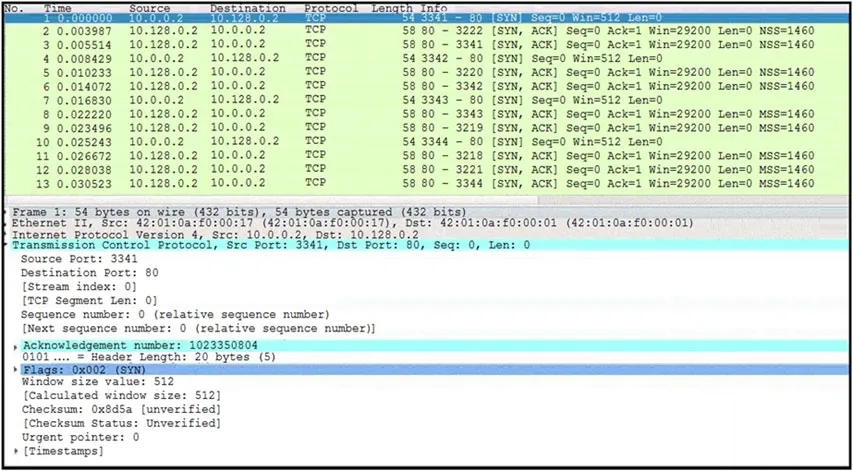
Refer to the exhibit. What is occurring in this network traffic?
Answer: D
In the provided network traffic capture, there is a flood of SYN packets (Synchronize) coming from a single source IP (10.128.0.2) to a single destination IP (10.0.0.2) on port 80. This is indicative of an attempt to establish multiple TCP connections. Therefore, the correct answer is D. Flood of SYN packets coming from a single source IP to a single destination IP
Source: Adapted from community discussion — AhmedAbdalla
An engineer needs to have visibility on TCP bandwidth usage, response time, and latency, combined with deep packet inspection to identify unknown software by its network traffic flow. Which two features of Cisco Application Visibility and Control should the engineer use to accomplish this goal? (Choose two.)
Answer: DE
Correct D and E AVC can do many things. Attention to the question. The engineering needs: visibility on several parameters - metrics collection and exporting (D) identify unknown software by its network traffic flow - application recognition (E)
Source: Adapted from community discussion — anonymous1966
Which security technology guarantees the integrity and authenticity of all messages transferred to and from a web application?
Answer: B
An engineer is investigating a case of the unauthorized usage of the `Tcpdump` tool. The analysis revealed that a malicious insider attempted to sniff traffic on a specific interface. What type of information did the malicious insider attempt to obtain?
Answer: D
using verbose parameter (-v or -vv) increases the amount of detail shown in the output, showing more than tagged protocols.
Source: Adapted from community discussion — fejec
At a company party a guest asks questions about the company's user account format and password complexity. How is this type of conversation classified?
Answer: D
Keyboard:J Kmove between questionsA–Dselect an answerRshow or hide the answer← →change page
200-201 practice, question 291. 334 questions available.
Version 1.0.0. How we source questions