Question 851 · 1003 in bank
Which security option protects credentials from sniffer attacks in a basicAPI authentication?
Show answer
Answer: B
Implementing Cisco Enterprise Network Core Technologies (ENCOR)1,003 questions across 101 pages are complete and free, with no account or card.
1003 questions in this bank
Free access · progress saved on this device
Which security option protects credentials from sniffer attacks in a basicAPI authentication?
Answer: B
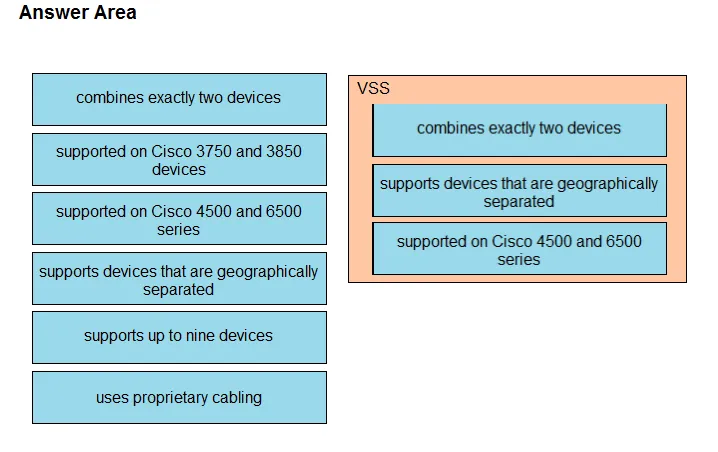
DRAG DROP - Drag and drop the descriptions of the VSS technology from the left to the right. Not all options are used. Select and Place:
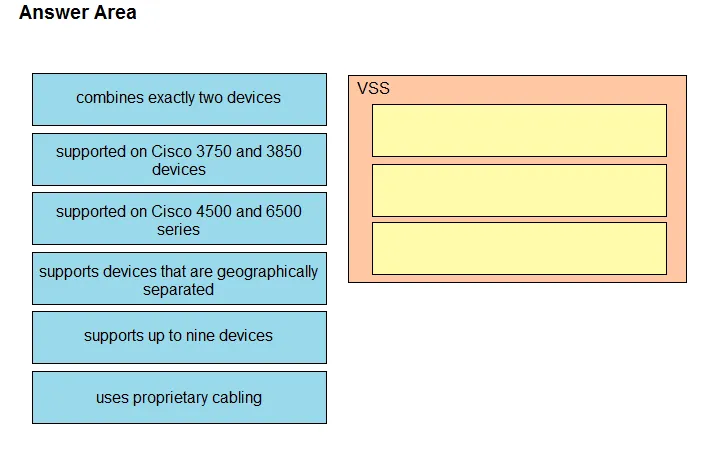
This is an interactive task on the real exam — a drag-and-drop, hotspot or ordering question. There is nothing to select here, so the answer is shown below for reference.
Answer: See figure below
Lets talk about the difference between both the technology Switch Stacking uses proprietary cabling and is limited in distance while in the case of Cisco VSS, It uses 10 GE interfaces and so it can be geographically separated In the case of stacking, no configuration required if switch supports stacking while in the case of Cisco VSS concept, you need to configure about the VSS and VSL on the switches. You can have stack upto 9 switches via stack cabling, while in the Cisco VSS, only two switches can be the part of VSS. For Cisco portfolio, Cisco switches like 2960 or 3750,3850 will be the part of the cisco stack switching while Cisco 4500 catalysts, Cisco 6500 and Cisco 6800 catalysts are using the concept of Cisco VSS. Another thing like Cisco stack switching generally used at Access layer while Cisco VSS can be used at distribution or core layers.
Source: Adapted from community discussion — Summo
Which mechanism can be used to enforce network access authentication against an AAA server if the endpoint does not support the 802.1X supplicant functionality?
Answer: A
MAC Authentication Bypass (MAB) is an access control technique that enables port-based access control using the MAC address of an endpoint, and it is typically used as a fallback mechanism to 802.1x. A MAB-enabled port can be dynamically enabled or disabled based on the MAC address of the endpoint that connects to it WebAuth, like MAB, can be used as a fallback authentication mechanism for 802.1x. If both MAB and WebAuth are configured as fallbacks for 802.1x, when 802.1x times out, a switch first attempts to authenticate through MAB, and if it fails, the switch attempts to authenticate with WebAuth Extracted from Secure Network Access Control, Chapter 25 of the OCG
Source: Adapted from community discussion — joseromerogarci
An engineer must configure router R1 to validate user logins via RADIUS and fall back to the local user database if the RADIUS server is not available. Which configuration must be applied?
Answer: A
The commands are wrong. They should have been: a) aaa authentication login default group radius local b) aaa authentication login default group radius c) aaa authorization exec default group radius local d) aaa authorization exec default group radius We can eliminate B & D because without "local" keyword, if the AAA server does not reply to the authentication/authorization request, the authentication/authorization fails. The reason I selected A is: "Authentication allows administrators to identify who can connect to a router by including the user's username and password." "Authorization comes into play after authentication. Authorization allows administrators to control the level of access users have after they successfully gain access to the router." Validate user logins - authentication. https://www.cisco.com/c/en/us/support/docs/security-vpn/terminal-access-controller-access-control-system-tacacs-/10384-security.html https://www.ciscopress.com/articles/article.asp?p=422947&seqNum=2
Source: Adapted from community discussion — Horsefeathers
What does the Cisco WLC Layer 3 roaming feature allow clients to do?
Answer: A
When a client initiates an L3 intercontroller roam, the two controllers involved can compare the VLAN numbers that are assigned to their respective WLAN interfaces If the two VLAN IDs differ, the controllers arrange a Layer 3 roam (also known as a local-to-foreign roam) that will allow the client to keep using its IP address. D: wrong -> talks about management VLAN of the controller
Source: Adapted from community discussion — riktammenaars
What is the function of Cisco DNA Center in a Cisco SD-Access deployment?
Answer: A
Cisco DNA Center serves as a centralized management platform for SD-Access deployments. It provides a single pane of glass for designing, deploying, managing, and troubleshooting the fabric network infrastructure. With Cisco DNA Center, administrators can define policies, provision network devices, monitor network performance, and ensure compliance across the fabric. It plays a crucial role in automating and simplifying network operations in SD-Access deployments.
Source: Adapted from community discussion — slacker_at_work
How do the MAC address table and TCAM differ?
Answer: D
TCAM: 1. A special type of memory for high-speed lookups. 2. Dedicated to packet classification and forwarding. 3. Stores complex forwarding information, such as Layer 2/Layer 3 forwarding, ACLs, and QoS. 4. Three possible results: true (0), false (1), and don’t care (X). 5. High speed and flexibility, suitable for complex packet processing. MAC Address Table: 1. A data structure that stores MAC addresses and their port information. 2. Typically implemented using RAM. 3. Stores MAC addresses and their associated ports for Layer 2 forwarding. 4. Two results: true (0) and false (1). 5. Slower speed and less flexibility.
Source: Adapted from community discussion — chiacche
Which technology provides an overlay fabric to connect remote locations utilizing commodity data paths and improves network performance, boosts security, and reduces costs?
Answer: C
Which two actions are recommended as security best practices to protect REST API? (Choose two.)
Answer: BC
Agreed. And considering the overwhelming majority of API calls in automation are "machine to machine", how exactly would the 2FA even work...
Source: Adapted from community discussion — TheGorn
DRAG DROP - Drag and drop the code snippets from the bottom onto the blanks in the PHP script to convert a PHP array into JSON format. Not all options are used.

This is an interactive task on the real exam — a drag-and-drop, hotspot or ordering question. There is nothing to select here, so the answer is shown below for reference.
Answer: See figure below
Answer is correct. // first configure array $InputArray = array(......); // json_encode function... the format is json_encode(name of the array) $encodedJSON = json_encode($InputArray, JSON_PRETTY_PRINT); //Finally print Print ($encodedJSON)
Source: Adapted from community discussion — studying_1

Keyboard:J Kmove between questionsA–Dselect an answerRshow or hide the answer← →change page
350-401 practice, question 851. 1003 questions available.
Version 1.0.0. How we source questions