Question 71 · 1334 in bank
SIMULATION - Guidelines - This is a lab item in which tasks will be performed on virtual devices: • Refer to the Tasks tab to view the tasks for this lab item. • Refer to the Topology tab to access the device console(s) and perform the tasks. • Console access is available for all required devices by clicking the device icon or using the tab(s) above the console window. • All necessary preconfigurations have been applied. • Do not change the enable password or hostname for any device. • Save your configurations to NVRAM before moving to the next item. • Click Next at the bottom of the screen to submit this lab and move to the next question. • When Next is clicked the lab closes and cannot be reopened. Topology -
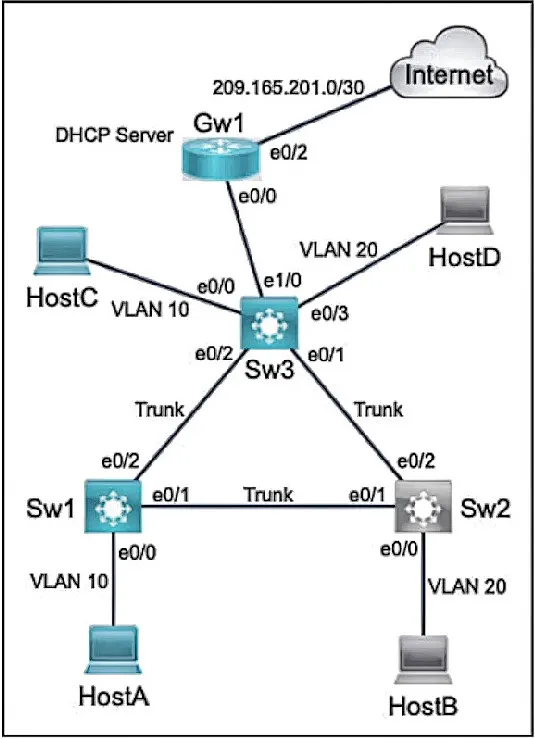
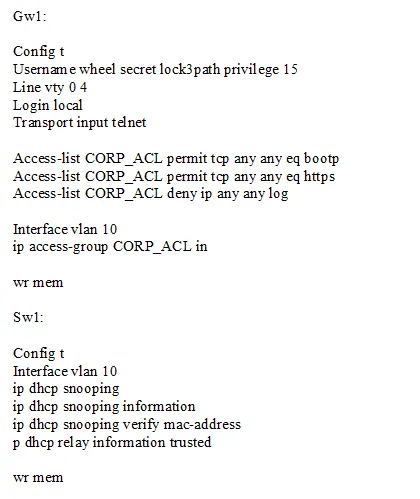
Tasks - Refer to the topology. All physical cabling is in place. Configure local users accounts, modify the Named ACL (NACL), and configure DHCP Snooping. The current contents of the NACL must remain intact. Task 1 - Configure a local account on Gw1 with telnet access only on virtual ports 0-4. Use the following information: • Username: wheel • Password: lock3path • Algorithm type: Scrypt • Privilege level: Exec mode Task 2 - Configure and apply a NACL on Gw1 to control network traffic from VLAN 10: • Name: CORP_ACL • Allow BOOTP and HTTPS • Restrict all other traffic and log the ingress interface, source MAC address, the packet’s source and destination IP addresses, and ports Task 3 - Configure Sw1: • Enable DNCP Snooping for VLAN 10 • Disable DHCP Option-82 data insertion • Enable DHCP Snooping MAC address verification • Enable trusted interfaces

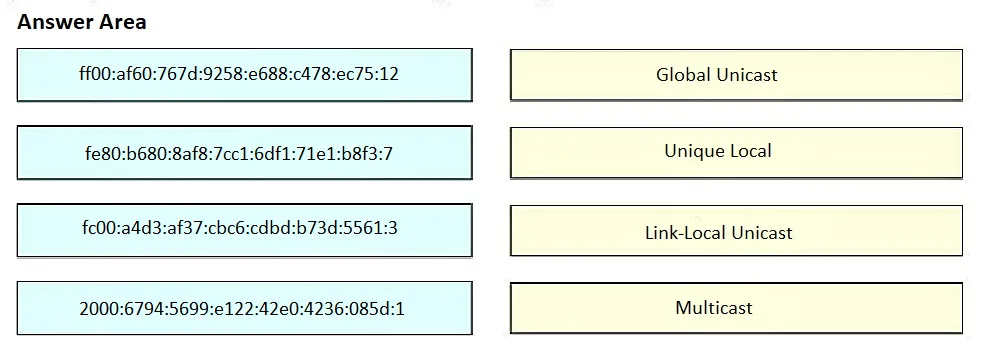
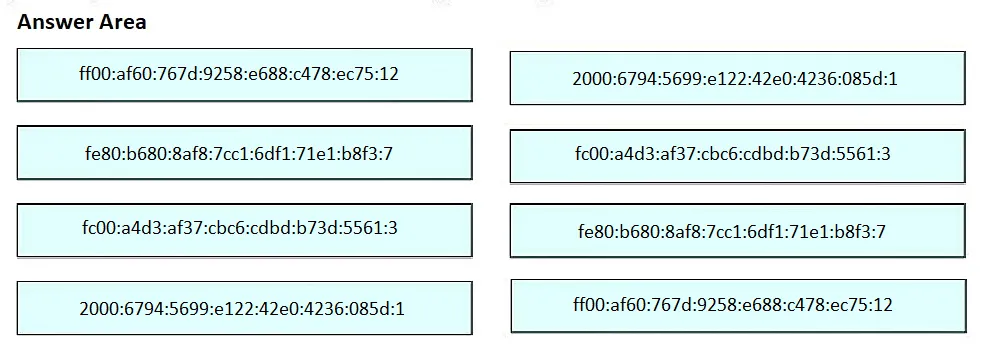
This is an interactive task on the real exam — a drag-and-drop, hotspot or ordering question. There is nothing to select here, so the answer is shown below for reference.
Show the answer figure
Answer: See figure below
Explanation
Task 1 GW1(config)#username wheel privilege 15 algorithm-type scrypt secret lock3path GW1(config)#line vty 0 4 GW1(config-line)#transport input telnet GW1(config-line)#login local Task 2 GW1(config)#ip access-list extended CORP_ACL GW1(config-ext-nacl)#permit udp any any eq 68 GW1(config-ext-nacl)#permit udp any any eq 67 GW1(config-ext-nacl)#permit tcp any any eq 443 GW1(config-ext-nacl)#deny ip any any log-input GW1(config)#interface gigabitEthernet 0/0.10 => Subinterface assigned to vlan 10 GW1(config-subif)#ip access-group CORP_ACL in Task 3 SW1(config)#ip dhcp snooping vlan 10 SW1(config)#no ip dhcp snooping information option SW1(config)#ip dhcp snooping verify mac-address SW1(config)#interface range gigabitEthernet 0/1-2 SW1(config-if-range)#ip dhcp snooping trust
Source: Adapted from community discussion — picho707