Question 1 · 392 in bank
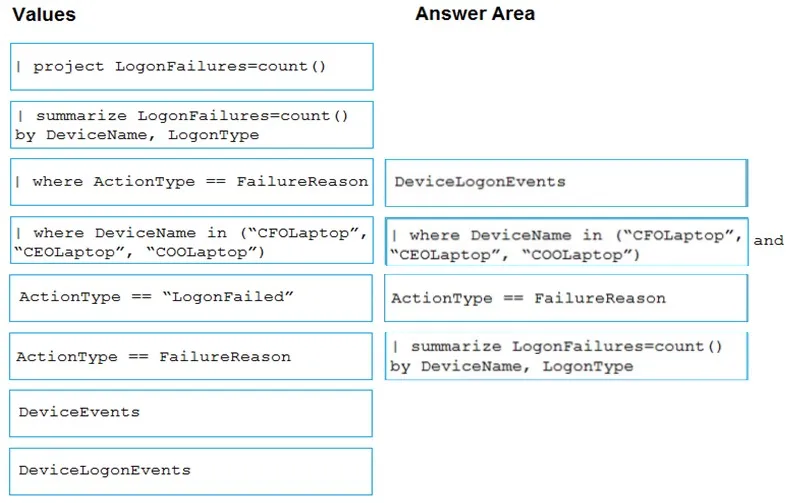
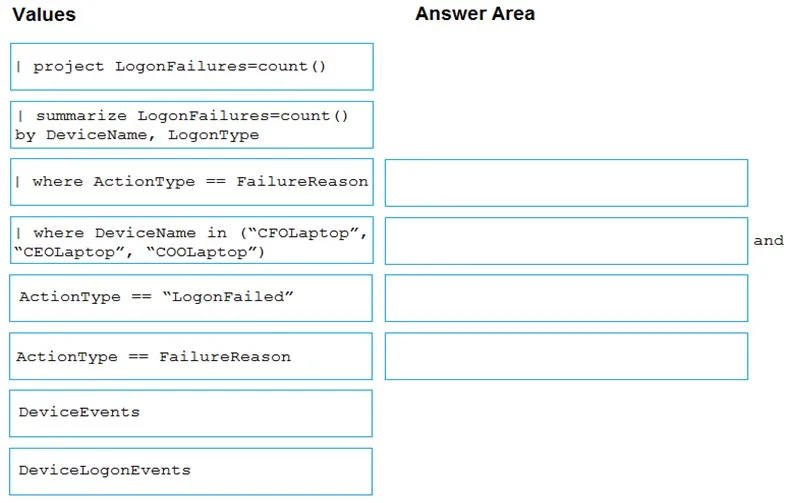
DRAG DROP - You are investigating an incident by using Microsoft 365 Defender. You need to create an advanced hunting query to count failed sign-in authentications on three devices named CFOLaptop, CEOLaptop, and COOLaptop. How should you complete the query? To answer, select the appropriate options in the answer area. NOTE: Each correct selection is worth one point. Select and Place:
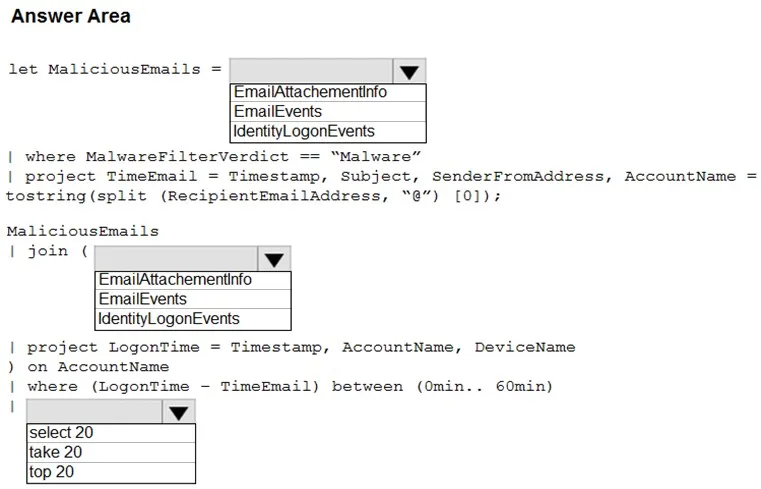
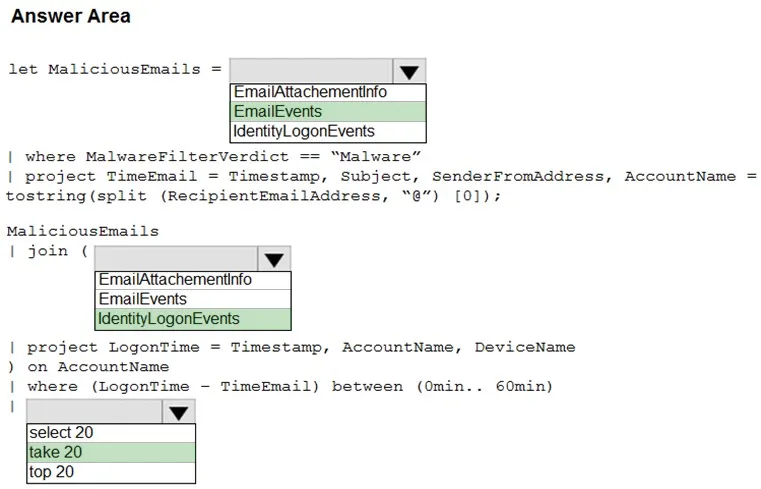
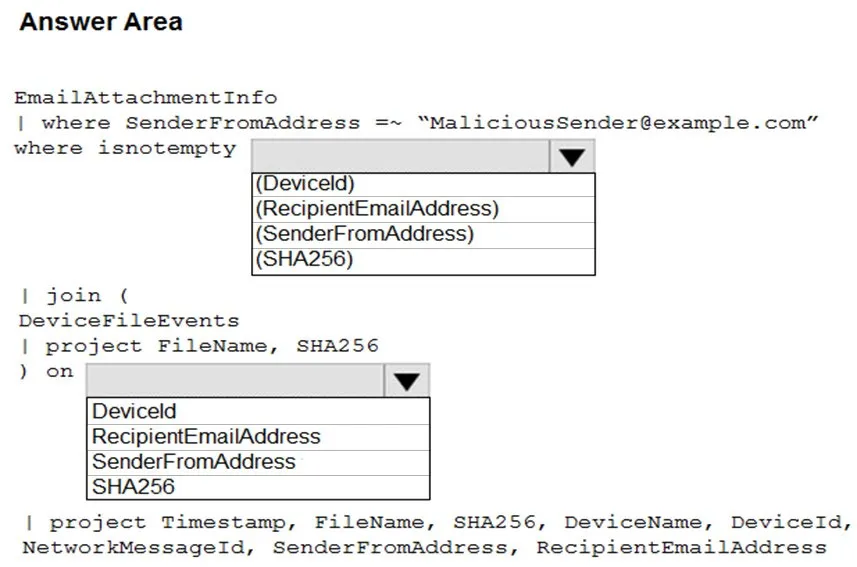
This is an interactive task on the real exam — a drag-and-drop, hotspot or ordering question. There is nothing to select here, so the answer is shown below for reference.
Show the answer figure
Answer: See figure below
Explanation
DeviceLogonEvents | where DeviceName in ("CFOLaptop" , "CEOLaptop" ) and ActionType == "LogonFailed" | summarize LogonFailures=count() by DeviceName , LogonType This is the correct answer , I tested it .
Source: Adapted from community discussion — DigitalNomad
References