Question 81 · 396 in bank
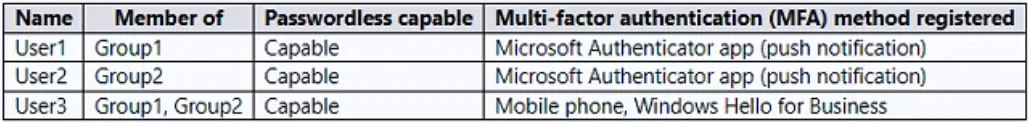
HOTSPOT - You have an Azure AD tenant that contains the users shown in the following table.

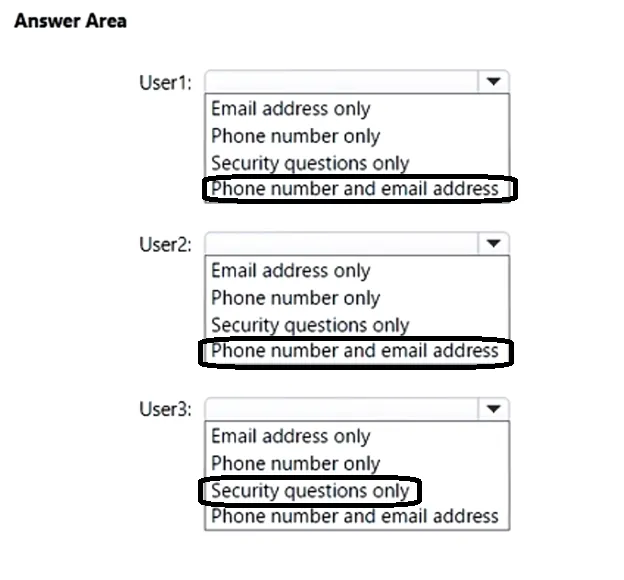
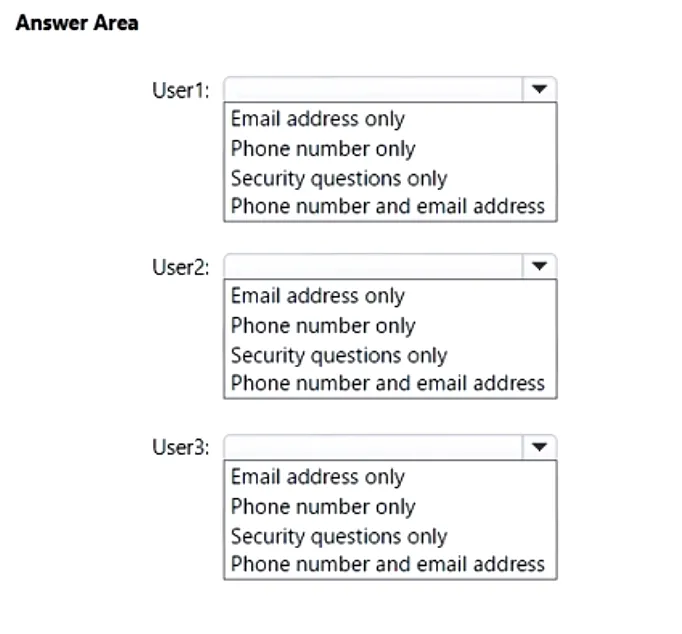
You enable self-service password reset for all users. You set Number of methods required to reset to 1, and you set Methods available to users to Security questions only. What information must be configured for each user before the user can perform a self-service password reset? To answer, select the appropriate options in the answer area. NOTE: Each correct selection is worth one point.
This is an interactive task on the real exam — a drag-and-drop, hotspot or ordering question. There is nothing to select here, so the answer is shown below for reference.
Show the answer figure
Answer: See figure below
Explanation
Correct By default, administrator accounts are enabled for self-service password reset, and a strong default two-gate password reset policy is enforced. This policy may be different from the one you have defined for your users, and this policy can't be changed. You should always test password reset functionality as a user without any Azure administrator roles assigned. With a two-gate policy, administrators don't have the ability to use security questions. The two-gate policy requires two pieces of authentication data, such as an email address, authenticator app, or a phone number. https://docs.microsoft.com/en-us/azure/active-directory/authentication/concept-sspr-policy#administrator-password-policy-differences
Source: Adapted from community discussion — Casticod
References