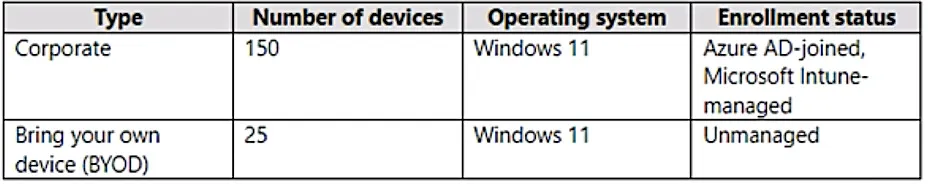
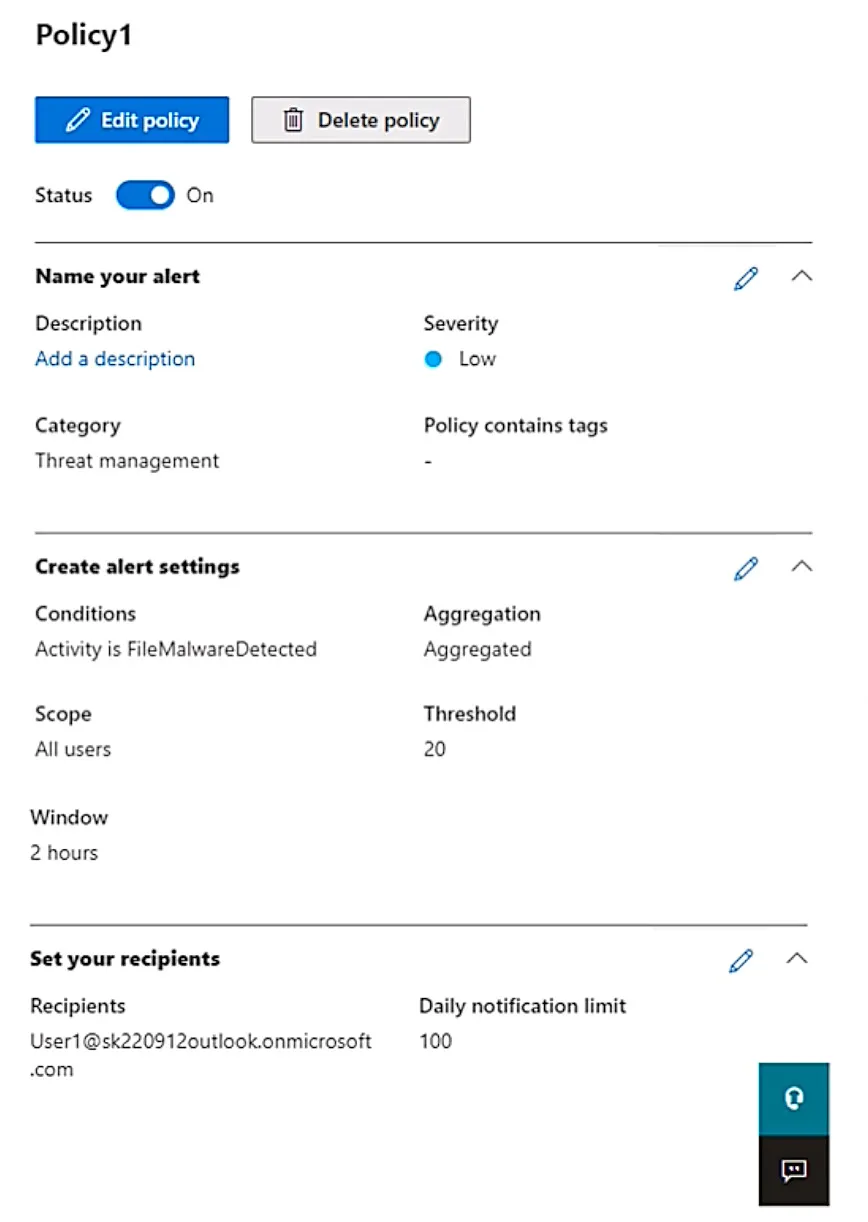
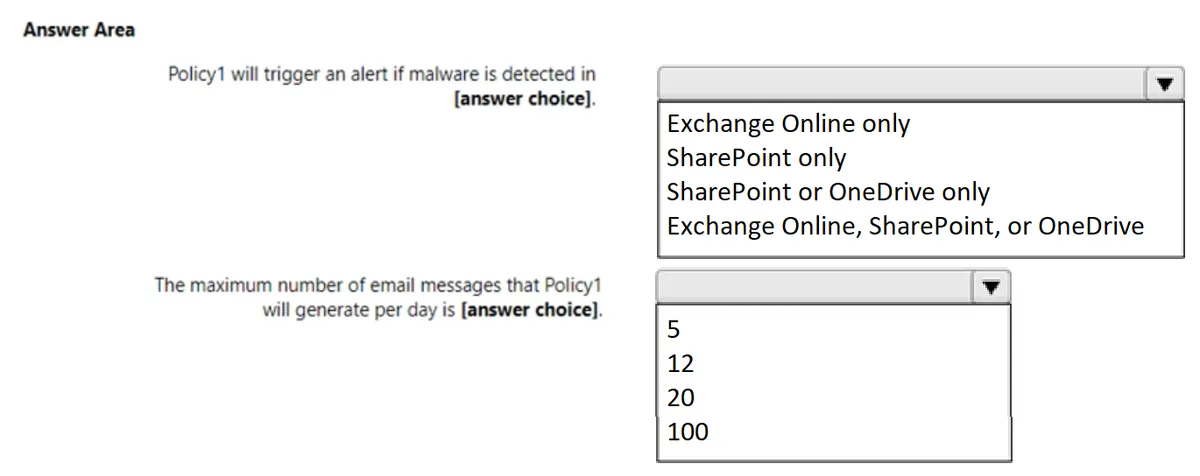
HOTSPOT - You have a Microsoft 365 E5 subscription that contains the devices shown in the following table.

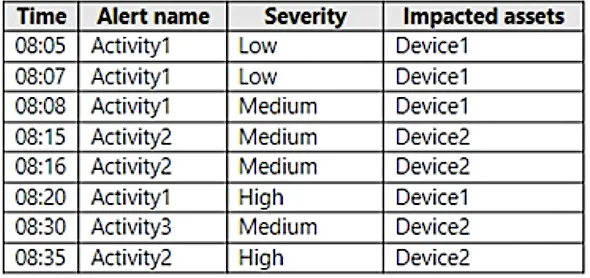
At 08:00, you create an incident notification rule that has the following configurations: • Name: Notification1 • Notification settings • Notify on alert severity: Low • Device group scope: All (3) • Details: First notification per incident • Recipients: User1@contoso.com, User2@contoso.com At 08:02, you create an incident notification rule that has the following configurations: • Name: Notification2 • Notification settings • Notify on alert severity: Low, Medium • Device group scope: DeviceGroup1, DeviceGroup2 • Recipients: User1@contoso.com In Microsoft 365 Defender, alerts are logged as shown in the following table.
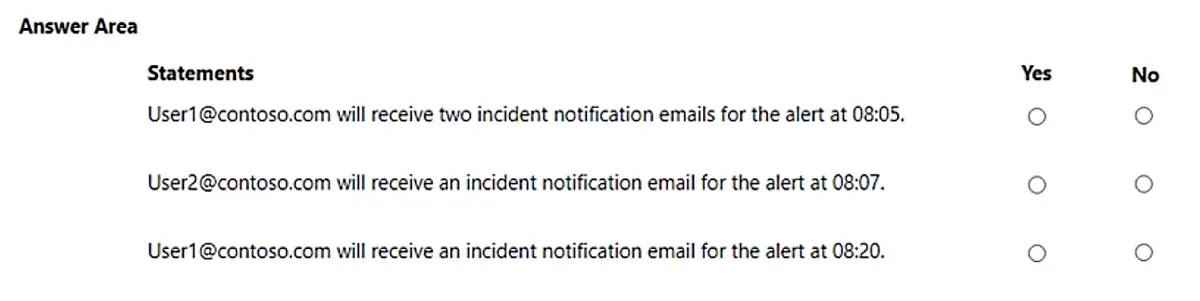
For each of the following statements, select Yes if the statement is true. Otherwise, select No. NOTE: Each correct selection is worth one point.
This is an interactive task on the real exam — a drag-and-drop, hotspot or ordering question. There is nothing to select here, so the answer is shown below for reference.