Question 251 · 540 in bank
You have a GitHub repository. You need to ensure that all the code in the repository is scanned for vulnerabilities. What should you use?
Show answer
Answer: C
Explanation
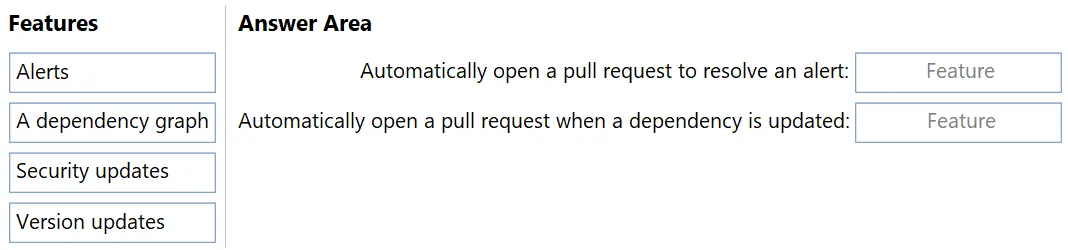
Dependabot is complementary to CodeQL. While CodeQL detects security issues in your own code, Dependabot detects vulnerabilities that originate from your project’s dependencies. A recent example was Log4j, which introduced a number of upstream impacts for package registries and dependencies. Since Log4j is widely used across apps and websites to help log activity in applications and websites, this incident meant a lot of people were suddenly forced to quickly update their Log4j versions to avoid any potential issues. Source: https://github.blog/2022-04-22-5-simple-things-every-developer-can-do-to-ship-more-secure-code/#:~:text=Dependabot%20is%20complementary%20to%20CodeQL,for%20package%20registries%20and%20dependencies.
Source: Adapted from community discussion — yana_b