Question 201 · 213 in bank
An analyst finds that a malicious program contains the instructions add 10, eax followed by sub 10, eax. What technique was the attacker likely using?
Show answer
Answer: D
GIAC Certified Incident Handler213 questions across 22 pages are complete and free, with no account or card.
213 questions in this bank
Free access · progress saved on this device
An analyst finds that a malicious program contains the instructions add 10, eax followed by sub 10, eax. What technique was the attacker likely using?
Answer: D
How should an incident handler classify the following event shown in the output below?
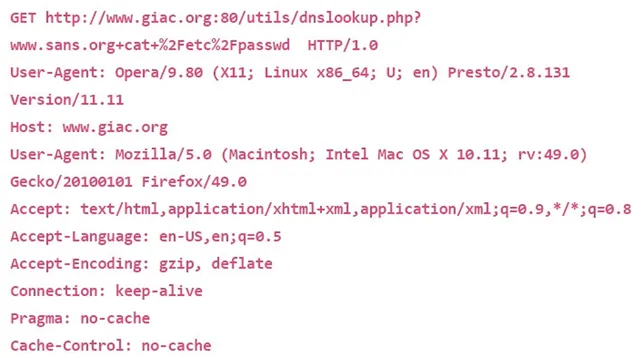
Answer: C
Which of the following accounts is an Administrator account?

Answer: D
A popular forum for ICS professionals to discuss techniques includes code that loads scripts and ads from multiple external sites. How would an adversary leverage this forum to compromise ICS industry targets?
Answer: A
What john format should be specified to crack an 18 character Windows password?
Answer: C
You have gained access to a Linux box. Which of the following methods would enable you to launch attacks against other systems and send the sessions back to your home PC (10.2.200.1) without altering system config files on the Linux box that might alert the sysadmin?
Answer: B
Considering Volatility, why would psscan return more results than pslist?
Answer: C
An organization has an SSH server that was compromised. Given the following evidence, what most likely occurred?
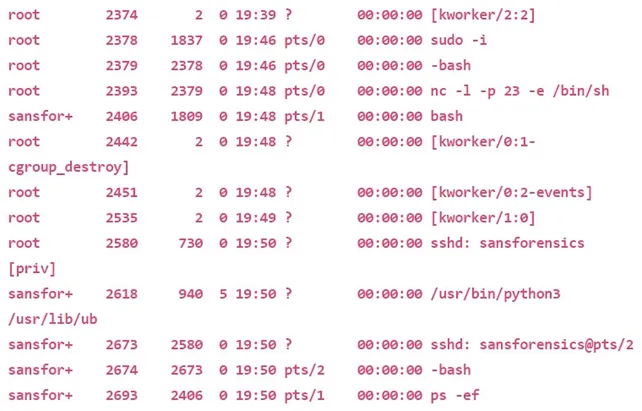
Answer: D
For what purpose would an auditor obtain a copy of the /etc/passwd file for a password audit of a linux machine?
Answer: C
A consultant provides an organization with a report that contains their users' most popular passwords, data on password sharing, and a breakdown of password length by department. Which tool could generate this report?
Answer: A
Keyboard:J Kmove between questionsA–Dselect an answerRshow or hide the answer← →change page
GCIH practice, question 201. 213 questions available.
Version 1.0.0. How we source questions