Question 161 · 213 in bank
Which malware investigation approach provides a detailed log of a system’s file system, network, registry and process activities?
Show answer
Answer: A
GIAC Certified Incident Handler213 questions across 22 pages are complete and free, with no account or card.
213 questions in this bank
Free access · progress saved on this device
Which malware investigation approach provides a detailed log of a system’s file system, network, registry and process activities?
Answer: A
Which PowerShell cmdlet will display the command line parameters used to launch a Windows process?
Answer: C
Which of the following logs could be queried to identify Azure, Amazon and Google storage use in an organization?
Answer: D
What is the outcome of the command below? hashcat -m 0 -a 3 ntds.dat --potfile-path ntds.potfile -1 ?d?d?d?d?d?d
Answer: B
What hash type is being cracked in the command below? hashcat -m 1800 -a 0 customer.ntds wordlist.txt --potfile-path ./hashcat.potfile
Answer: D
What UNIX component can be used to enforce password complexity requirements?
Answer: A
Which web application log keyword would be associated with a SQL injection attack?
Answer: A
Which endpoint security bypass technique leverages existing system tools instead of adding executable?
Answer: C
Based on the nmap data in the screenshot the analyst would choose which IP address for a DNS attack?
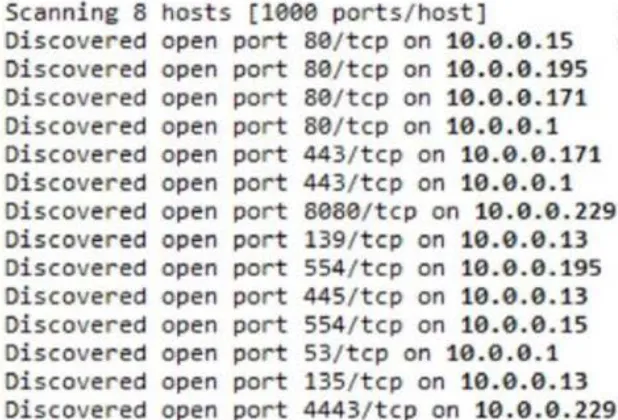
Answer: C
An attacker is hoping to discover as many IP addresses associated with a target domain as possible. Which command would be helpful?
Answer: C
Keyboard:J Kmove between questionsA–Dselect an answerRshow or hide the answer← →change page
GCIH practice, question 161. 213 questions available.
Version 1.0.0. How we source questions