Question 121 · 213 in bank
What is the Linux administrator doing with the commands below? $ rpcclient -U fezzik florin rpcclient $> lsaenumsid
Show answer
Answer: C
GIAC Certified Incident Handler213 questions across 22 pages are complete and free, with no account or card.
213 questions in this bank
Free access · progress saved on this device
What is the Linux administrator doing with the commands below? $ rpcclient -U fezzik florin rpcclient $> lsaenumsid
Answer: C
When probing for command injection opportunities on a remote host, why would an attacker target her own address space from the remote host?
Answer: D
An administrator needs to protect his organization's IIS webservers from Cross-Site Scripting attacks. Which action should he take?
Answer: A
What information is commonly found in both the header and the possession log of a Chain of Custody?
Answer: B
Which of the following Metasploit module types would contain privilege escalation capabilities?
Answer: D
Which of the following describes a suspicious event in the service data below? root@kali:~/volatility# ./vol.py -f ../mem/Desk005.vmem svcscan
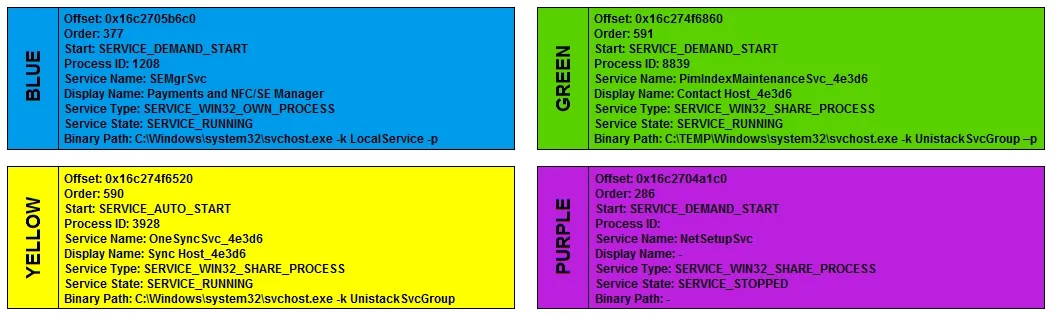
Answer: D
Which file contains information about failed login attempts on a Unix system?
Answer: C
What is one of the simplest AND most common ways for an attacker to camouflage files on a UNIX system?
Answer: C
Which of the following packets saved in the file pingout.pcap would be returned with the following Berkley Packet Filters? tcpdump -nn -r pingout.pcap `˜icmp and (dst host 8.8.8.8)'
Answer: A
During the identification phase of a Web server compromise, you notice the following entries in the web server logs. If "admin" is a valid username, but its corresponding password is not "pass1", and "root" is not a valid username, what can you infer solely from these logs?
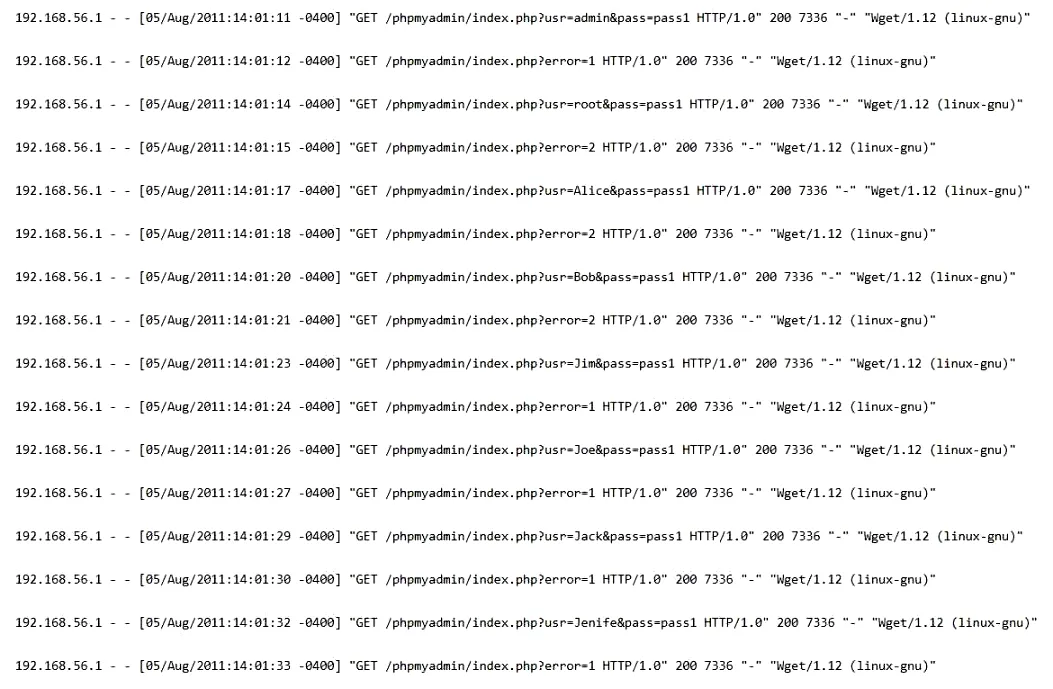
Answer: D
Keyboard:J Kmove between questionsA–Dselect an answerRshow or hide the answer← →change page
GCIH practice, question 121. 213 questions available.
Version 1.0.0. How we source questions