Question 71 · 213 in bank
To defend against network mapping, which of the following packets should be denied at the border router?
Show answer
Answer: A
GIAC Certified Incident Handler213 questions across 22 pages are complete and free, with no account or card.
213 questions in this bank
Free access · progress saved on this device
To defend against network mapping, which of the following packets should be denied at the border router?
Answer: A
As related to buffer overflows, what is the purpose of the Instruction Pointer?
Answer: A
Which stage of an attack typically involves little or no direct interaction with the attack target(s)?
Answer: C
A client wants a system so that they can monitor connection queues on network equipment for too many half-open connections, as well as look for bandwidth consumption from the same types of connections. What kind of attacks will this type of system defend against?
Answer: C
If virtual machines are relatively easy for an attacker to detect, the next best thing might be to put so much honey in your honeypot, attackers won't be able to resist. Which actions would result in the most meaningful traffic on your honeypot?
Answer: D
Which reconnaissance source would you expect to provide the information in the below screen capture?
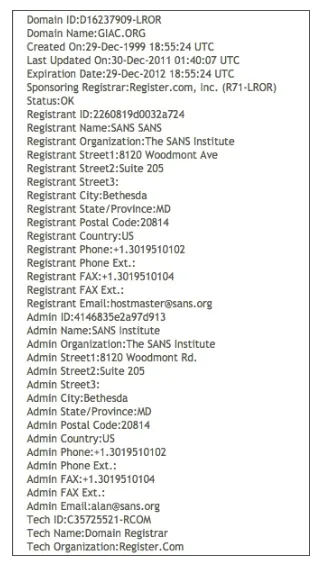
Answer: B
A new helpdesk employee at a multinational corporation took it upon himself to test the security of the servers that holds highly confidential information regarding specific government projects. Which of the following is a well-known technique for deterring such individuals?
Answer: B
You are a member of your organization's security team. A new ticket just came into your service desk and was escalated to you. One of the system administrators noticed the following entry in a Windows Server 2008 R2 file server Security event log: Log Name: Security - Source: Microsoft-Windows-Security-Auditing Date: 2/1/2012 2:24:07 AM - Event ID: 4674 - Task Category: Sensitive Privilege Use Level: Information - Keywords: Audit Failure - User: N/A - Computer: somehost.somecompany.com Description: An operation was attempted on a privileged object. Subject: Security ID: LOCAL SERVICE - Account Name: LOCAL SERVICE - Account Domain: NT AUTHORITY - Logon ID: 0x3e5 - Object: Object Server: LSA - Object Type: - Object Name: - Object Handle: 0x0 - Process Information: Process ID: 0x1d8 - Process Name: C:\Windows\System32\Isass.exe Requested Operation: Desired Access: 16777216 - Privileges: SeSecurityPrivilege - What is your next step?
Answer: A
The Network Operations Center has identified and escalated an active denial of service incident on the mail server and several externally facing web sites to the security team for review. What are the next steps for the NOC team?
Answer: D
Analysis of malicious code identifies a function that searches for specific processes and hardware on a victim host. If the processes or hardware are found, the malicious executable does not install itself. What is a common purpose of this type of malware functionality?
Answer: A
Keyboard:J Kmove between questionsA–Dselect an answerRshow or hide the answer← →change page
GCIH practice, question 71. 213 questions available.
Version 1.0.0. How we source questions