Question 91 · 104 in bank
Refer to the exhibit to view the firewall policy.
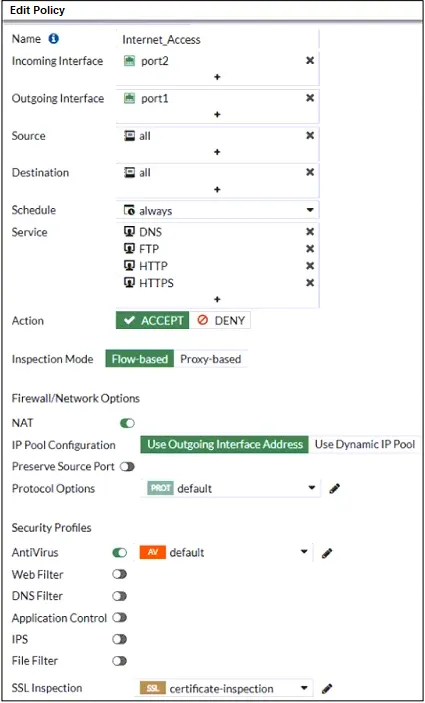
Why would the firewall policy not block a well-known virus, for example eicar?
Show answer
Answer: C
NSE 4 — FortiOS 7.2 Network Security Professional104 questions across 11 pages are complete and free, with no account or card.
104 questions in this bank
Free access · progress saved on this device
Refer to the exhibit to view the firewall policy.
Why would the firewall policy not block a well-known virus, for example eicar?
Answer: C
What are two characteristics of FortiGate HA cluster virtual IP addresses? (Choose two.)
Answer: AD
A. Virtual IP addresses are used to distinguish between cluster members. D. A change in the virtual IP address happens when a FortiGate device joins or leaves the cluster. FortiGate Infrastructure 7.2 Study Guide (p.301): "FGCP automatically assigns the heartbeat IP addresses based on the serial number of each device. The IP address 169.254.0.1 is assigned to the device with the highest serial number." "A change in the heartbeat IP addresses may happen when a FortiGate device joins or leaves the cluster." "The HA cluster uses the heartbeat IP addresses to distinguish the cluster members and synchronize data." Reference and download study guide: https://ebin.pub/fortinet-fortigate-infrastructure-study-guide-for-fortios-72.html
Source: Adapted from community discussion — raydel92
An administrator wants to simplify remote access without asking users to provide user credentials. Which access control method provides this solution?
Answer: B
B. ZTNA access proxy FortiGate Infrastructure 7.2 Study Guide (p.165): "ZTNA access proxy allows users to securely access resources through an SSL-encrypted access proxy. This simplifies remote access by eliminating the use of VPNs." Reference and download study guide: https://ebin.pub/fortinet-fortigate-infrastructure-study-guide-for-fortios-72.html
Source: Adapted from community discussion — raydel92
Refer to the exhibit showing a debug flow output.
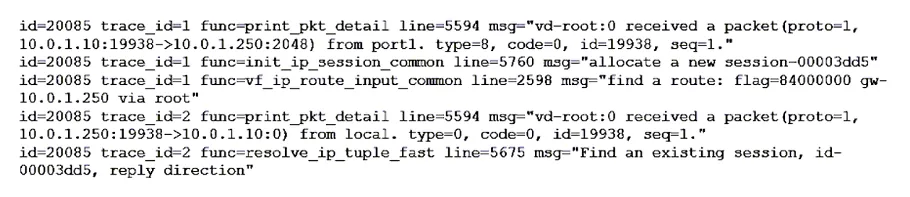
What two conclusions can you make from the debug flow output? (Choose two.)
Answer: AC
A. The debug flow is for ICMP traffic. C. A new traffic session was created. Reference and download study guide: https://ebin.pub/fortinet-fortigate-infrastructure-study-guide-for-fortios-72.html
Source: Adapted from community discussion — raydel92
What are two features of collector agent advanced mode? (Choose two.)
Answer: AD
A. In advanced mode, FortiGate can be configured as an LDAP client and group filters can be configured on FortiGate. D. Advanced mode supports nested or inherited groups. FortiGate Infrastructure 7.2 Study Guide (p.146): "Also, advanced mode supports nested or inherited groups; that is, users can be members of subgroups that belong to monitored parent groups." "In advanced mode, you can configure FortiGate as an LDAP client and configure the group filters on FortiGate. You can also configure group filters on the collector agent." Reference and download study guide: https://ebin.pub/fortinet-fortigate-infrastructure-study-guide-for-fortios-72.html
Source: Adapted from community discussion — raydel92
Which three CLI commands can you use to troubleshoot Layer 3 issues, if the issue is in neither the physical layer nor the link layer? (Choose three.)
Answer: ABD
A,B & D correct , layer 3 diagnose sys top - list of processes with most CPU get system arp - show interface, IP, MAC (physical layer)
Source: Adapted from community discussion — Halmonte0780
What are two scanning techniques supported by FortiGate? (Choose two.)
Answer: AB
A. Machine learning scan B. Antivirus scan FortiGate Security 7.2 Study Guide (p.341): "Like viruses, which use many methods to avoid detection, FortiGate uses many techniques to detect viruses. These detection techniques include: • Antivirus scan • Grayware scan • Machine learning (AI) scan If all antivirus features are enabled, FortiGate applies the following scanning order: antivirus scan, followed by grayware scan, followed by AI scan." Reference and download study guide: https://ebin.pub/fortinet-fortigate-security-study-guide-for-fortios-72.html
Source: Adapted from community discussion — raydel92
Refer to the exhibit. The exhibit shows a diagram of a FortiGate device connected to the network and the firewall policy and IP pool configuration on the FortiGate device. Two PCs, PC1 and PC2, are connected behind FortiGate and can access the internet successfully. However, when the administrator adds a third PC to the network (PC3), the PC cannot connect to the internet.
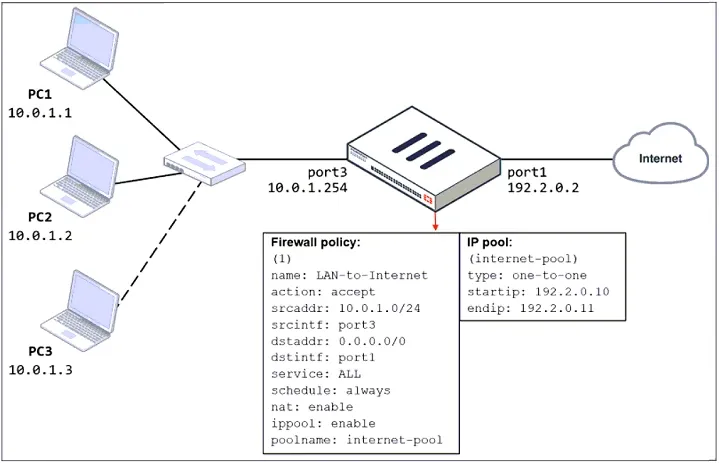
Based on the information shown in the exhibit, which three configuration changes should the administrator make to fix the connectivity issue for PC3? (Choose three.)
Answer: ACD
D: If we disable Ippool via cli, the default will be overload. E: we create a new firewall policy but don't say anything about enable NAT, so this will fail.
Source: Adapted from community discussion — GANGA2021
Refer to the exhibit.
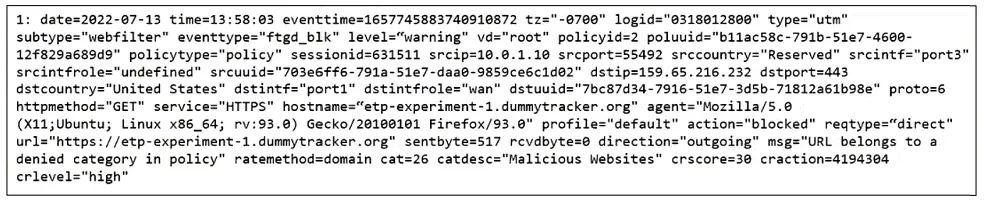
Based on the raw log, what can you conclude from the output? (Choose two.)
Answer: BC
B. VDOM=root C. Security=UTM D. Log severity is set to error on FortiGate. obviously wrong B. Traffic belongs to the root VDOM. correct (vd="root") A. Traffic is blocked because Action is set to DENY in the firewall policy. wrong (msg="URL belongs to a DENIED CATEGORY in policy" It's meaning traffic blocked with "Security Profiles" but Action is allow int the firewall policy) C. This is a security log. correct (type="utm")
Source: Adapted from community discussion — Halmonte0780
Which two settings can be separately configured per VDOM on a FortiGate device? (Choose two.)
Answer: CD
The Correct Answer are C, D *Operating mode (transparent mode and Nat Mode) *NGFW mode (profile-based, policy-based) Infrastructure guide 7.2, pages 90 and 91
Source: Adapted from community discussion — Halmonte0780
Keyboard:J Kmove between questionsA–Dselect an answerRshow or hide the answer← →change page
NSE4_FGT-7.2 practice, question 91. 104 questions available.
Version 1.0.0. How we source questions