Question 181 · 393 in bank
A security analyst is reviewing the following authentication logs:
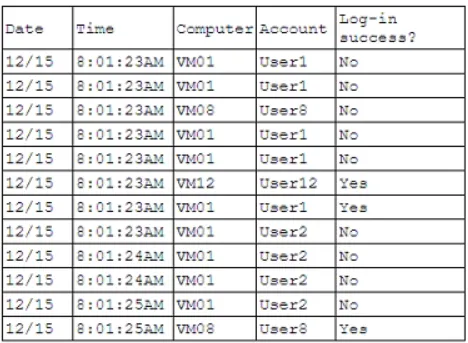
Which of the following should the analyst do first?
Show answer
Answer: D
CompTIA SecurityX393 questions across 40 pages are complete and free, with no account or card.
393 questions in this bank
Free access · progress saved on this device
A security analyst is reviewing the following authentication logs:
Which of the following should the analyst do first?
Answer: D
A game developer wants to reach new markets and is advised by legal counsel to include specific age-related sign-up requirements. Which of the following best describes the legal counsel's concerns?
Answer: D
During a recent audit, a company's systems were assessed Given the following information:

Which of the following is the best way to reduce the attack surface?
Answer: D
A global manufacturing company has an internal application that is critical to making products. This application cannot be updated and must be available in the production area. A security architect is implementing security for the application. Which of the following best describes the action the architect should take?
Answer: D
A company wants to perform threat modeling on an internally developed, business-critical application. The Chief Information Security Officer (CISO) is most concerned that the application should maintain 99.999% availability and authorized users should only be able to gain access to data they are explicitly authorized to view. Which of the following threat-modeling frameworks directly addresses the CISO’s concerns about this system?
Answer: B
A company's internal network is experiencing a security breach and the threat actor is still active Due to business requirements, users in this environment are allowed to utilize multiple machines at the same time. Given the following log snippet:
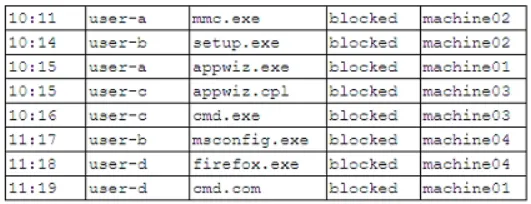
Which of the following accounts should a security analyst disable to best contain the incident without impacting valid users?
Answer: D
A security team is responding to malicious activity and needs to determine the scope of impact. The malicious activity appears to affect a certain version of an application used by the organization. Which of the following actions best enables the team to determine the scope of impact?
Answer: C
An organization recently implemented a policy that requires all passwords to be rotated every 90 days. An administrator sees a large volume of failed sign-on logs from multiple servers that are often accessed by users. The administrator determines users are disconnecting from the RDP session but not logging off. Which of the following should the administrator do to prevent account lockouts?
Answer: C
A security review revealed that not all of the client proxy traffic is being captured. Which of the following architectural changes best enables the capture of traffic for analysis?
Answer: A
A security architect is onboarding a new EDR agent on servers that traditionally do not have internet access. In order for the agent to receive updates and report back to the management console, some changes must be made. Which of the following should the architect do to best accomplish this requirement? (Choose two.)
Answer: AC
Keyboard:J Kmove between questionsA–Dselect an answerRshow or hide the answer← →change page
CAS-005 practice, question 181. 393 questions available.
Version 1.0.0. How we source questions