Question 151 · 393 in bank
Which of the following best explains the business requirement a healthcare provider fulfills by encrypting patient data at rest?
Show answer
Answer: C
CompTIA SecurityX393 questions across 40 pages are complete and free, with no account or card.
393 questions in this bank
Free access · progress saved on this device
Which of the following best explains the business requirement a healthcare provider fulfills by encrypting patient data at rest?
Answer: C
A security engineer is implementing security measures on new hardware in preparation for its launch. During the development phase, a risk related to protections at the UEFI level was found. Which of the following should the engineer recommend to reduce this risk?
Answer: B
A hotel chain wants to use point-of-sale systems to allow customers to check in and out of their rooms without employee assistance. These systems should limit access to a specific set of programs approved to run, with all other programs blocked. Which of the following should the company configure to best support this goal?
Answer: A
A user reports application access issues to the help desk. The help desk reviews the logs for the user:
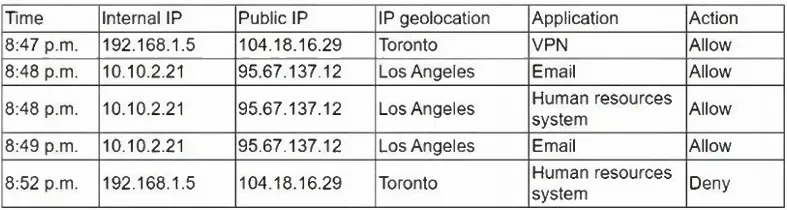
Which of the following is most likely the reason for the issue?
Answer: D
A global organization wants to manage all endpoint and user telemetry. The organization also needs to differentiate this data based on which office it is correlated to. Which of the following strategies best aligns with this goal?
Answer: B
A security architect must make sure that the least number of services as possible is exposed in order to limit an adversary's ability to access the systems. Which of the following should the architect do first?
Answer: B
A security officer performs due diligence activities before implementing a third-party solution into the enterprise environment. The security officer needs evidence from the third party that a data subject access request handling process is in place. Which of the following is the security officer most likely seeking to maintain compliance?
Answer: C
An administrator needs to craft a single certificate-signing request for a web-server certificate. The server should be able to use the following identities to mutually authenticate other resources over TLS: • www.int.comptia.org • webserver01 .int.comptia.org • 10.5.100.10 Which of the following certificate fields must be set properly to support this objective?
Answer: A
A security analyst reviews the following event timeline from an EDR solution:
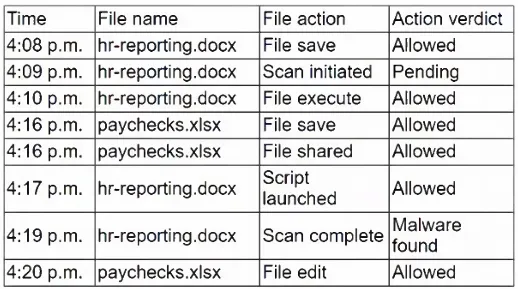
Which of the following has most likely occurred and needs to be fixed?
Answer: C
A hospital provides tablets to its medical staff to enable them to more quickly access and edit patients' charts. The hospital wants to ensure that if a tablet is identified as lost or stolen and a remote command is issued, the risk of data loss can be mitigated within seconds. The tablets are configured as follows to meet hospital policy: • Full disk encryption is enabled. • "Always On" corporate VPN is enabled. • eFuse-backed keystore is enabled/ready. • Wi-Fi 6 is configured with SAE. • Location services is disabled. • Application allow list is unconfigured. Assuming the hospital policy cannot be changed, which of the following is the best way to meet the hospital's objective?
Answer: B
Keyboard:J Kmove between questionsA–Dselect an answerRshow or hide the answer← →change page
CAS-005 practice, question 151. 393 questions available.
Version 1.0.0. How we source questions