Question 171 · 393 in bank
A security engineer is reviewing the following vulnerability scan report:

Which of the following should the engineer prioritize for remediation?
Show answer
Answer: B
CompTIA SecurityX393 questions across 40 pages are complete and free, with no account or card.
393 questions in this bank
Free access · progress saved on this device
A security engineer is reviewing the following vulnerability scan report:
Which of the following should the engineer prioritize for remediation?
Answer: B
A company notices that cloud environment costs increased after using a new serverless solution based on API requests. Many invalid requests from unknown IPs were found, often within a short time. Which of the following solutions would most likely solve this issue, reduce cost, and improve security?
Answer: C
A large organization deployed a generative AI platform for its global user population to use. Based on feedback received during beta testing, engineers have identified issues with user interface latency and page-loading performance for international users. The infrastructure is currently maintained within two separate data centers, which are connected using high-availability networking and load balancers. Which of the following is the best way to address the performance issues?
Answer: A
A company reduced its staff 60 days ago, and applications are now starting to fail. The security analyst is investigating to determine if there is malicious intent for the application failures. The security analyst reviews the following logs:
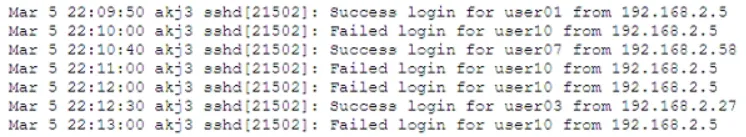
Which of the following is the most likely reason for the application failures?
Answer: A
Source code snippets for two separate malware samples are shown below:
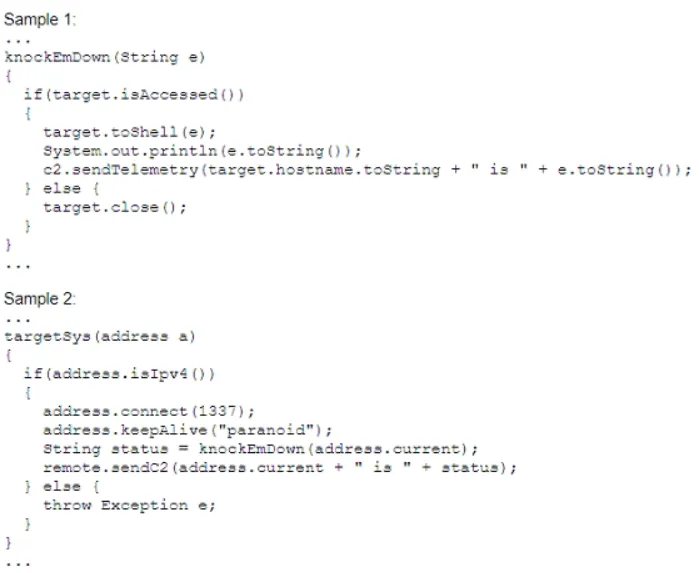
Which of the following describes the most important observation about the two samples?
Answer: B
A security analyst received a notification from a cloud service provider regarding an attack detected on a web server. The cloud service provider shared the following information about the attack: • The attack came from inside the network. • The attacking source IP was from the internal vulnerability scanners • The scanner is not configured to target the cloud servers. Which of the following actions should the security analyst take first?
Answer: B
A company implemented a NIDS and a NIPS on the most critical environments. Since this implementation the company has been experiencing network connectivity issues. Which of the following should the security architect recommend for a new NIDS/NIPS implementation?
Answer: A
The material findings from a recent compliance audit indicate a company has an issue with excessive permissions. The findings show that employees changing roles or departments results in privilege creep. Which of the following solutions are the best ways to mitigate this issue? (Choose two.)
Answer: BE
A security analyst is reviewing a SIEM and generates the following report:
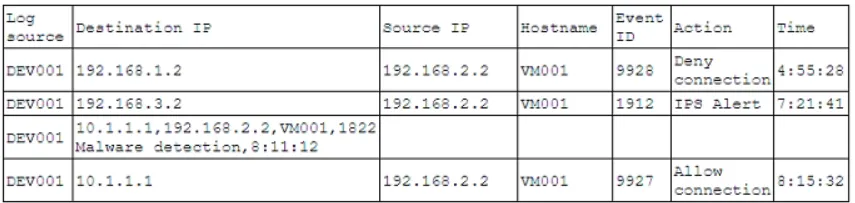
Later, the incident response team notices an attack was executed on the VM001 host. Which of the following should the security analyst do to enhance the alerting process on the SIEM platform?
Answer: B
A security administrator is performing a gap assessment against a specific OS benchmark. The benchmark requires the following configurations be applied to endpoints: • Full disk encryption • Host-based firewall • Time synchronization • Password policies • Application allow listing • Zero Trust application access Which of the following solutions best addresses the requirements? (Choose two.)
Answer: AE
Keyboard:J Kmove between questionsA–Dselect an answerRshow or hide the answer← →change page
CAS-005 practice, question 171. 393 questions available.
Version 1.0.0. How we source questions