Question 311 · 527 in bank
Select 2Which of the following are process improvements that can be realized by implementing a SOAR solution? (Choose two.)
Show answer
Answer: CF
CompTIA Cybersecurity Analyst (CySA+)527 questions across 53 pages are complete and free, with no account or card.
527 questions in this bank
Free access · progress saved on this device
Which of the following are process improvements that can be realized by implementing a SOAR solution? (Choose two.)
Answer: CF
Which of the following best describe the external requirements that are imposed for incident management communication? (Choose two).
Answer: BF
A security analyst observes a high volume of SYN flags from an unexpected source toward a web application server within one hour. The traffic is not flagging for any exploit signatures. Which of the following scenarios best describes this activity?
Answer: C
Which of the following features is a key component of Zero Trust architecture?
Answer: A
An analyst produces a weekly endpoint status report for the management team. The report Includes specific details for each endpoint in relation to organizational baselines. Which of the following best describes the report type?
Answer: D
A user’s computer is performing slower than the day before, and unexpected windows continually open and close. The user did not install any new programs, and after the user restarted the desktop, the issue was not resolved. Which of the following incident response actions should be taken next?
Answer: B
I am going with B because restarting could delete all forensic evidences or allow the possible malware to change its behavior (A), a legal hold i sonly needed for legal cases and CompTIA didn't mention it (C), and (D) should only be done after investigation and containment.
Source: Adapted from community discussion — Cyde
An analyst is reviewing a vulnerability report for a server environment with the following entries:
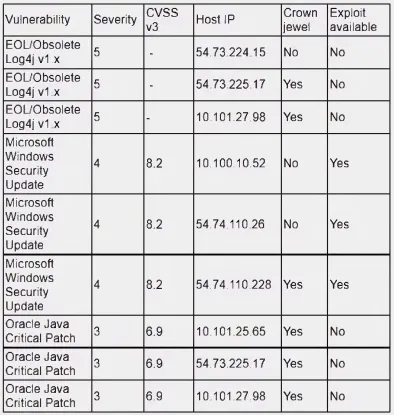
Which of the following systems should be prioritized for patching first?
Answer: D
Based on the vulnerability report, the system that should be prioritized for patching first is 54.74.110.228. This system has a critical vulnerability listed in the report, which means that it is at high risk of being exploited by an attacker. Additionally, the vulnerability is publicly known, so there is a high likelihood that an exploit is already available.
Source: Adapted from community discussion — Alizade
A security analyst needs to prioritize vulnerabilities for patching. Given the following vulnerability and system information:
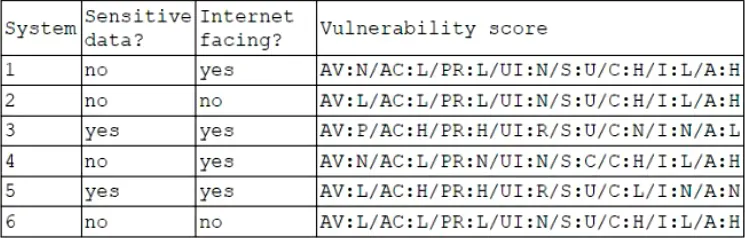
Which of the following systems should the analyst patch?
Answer: D
System 4 should be patched first because it is internet facing, requires no privileges, no user interaction, and has a changed scope, meaning it can impact other systems.
Source: Adapted from community discussion — fab34
During a packet capture review, a security analyst identifies the output below as suspicious:
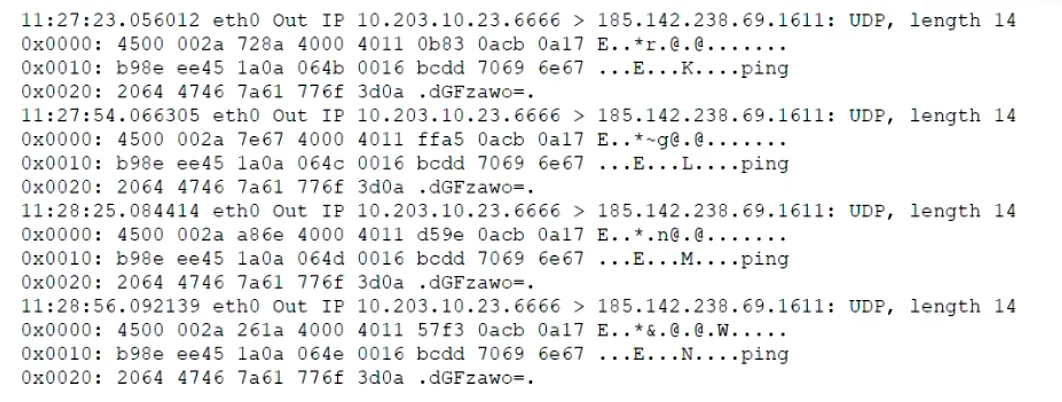
Which of the following best describes the type of activity the analyst has identified?
Answer: D
Has anyone taken the exam recently? I want to know how accurate these questions are, I am taking my test early next month.
Source: Adapted from community discussion — Wolf541
A company is in the process of implementing a vulnerability management program, and there are concerns about granting the security team access to sensitive data. Which of the following scanning methods can be implemented to reduce the access to systems while providing the most accurate vulnerability scan results?
Answer: C
As I am working in the Vulnerability Assessment and based on this scenario, I would need to choose Agent-based scanning. Here's why: +There is no need to use credentials (username and password), while the agent is installed through the supper admin account on the target machine +Less network bandwidth consumption +Local based on the target => The answer is C
Source: Adapted from community discussion — Phanna
Keyboard:J Kmove between questionsA–Dselect an answerRshow or hide the answer← →change page
CS0-003 practice, question 311. 527 questions available.
Version 1.0.0. How we source questions