Question 261 · 527 in bank
Which of the following is the best framework for assessing how attackers use techniques over an infrastructure to exploit a target’s information assets?
Show answer
Answer: D
CompTIA Cybersecurity Analyst (CySA+)527 questions across 53 pages are complete and free, with no account or card.
527 questions in this bank
Free access · progress saved on this device
Which of the following is the best framework for assessing how attackers use techniques over an infrastructure to exploit a target’s information assets?
Answer: D
A threat intelligence analyst is updating a document according to the MITRE ATT&CK framework. The analyst detects the following behavior from a malicious actor: “The malicious actor will attempt to achieve unauthorized access to the vulnerable system.” In which of the following phases should the analyst include the detection?
Answer: C
An analyst receives alerts that state the following traffic was identified on the perimeter network firewall:
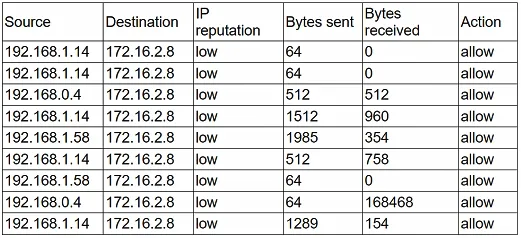
Which of the following best describes the indicator of compromise that triggered the alerts?
Answer: A
Not seeing any evidence of cryptomining. Not enough to validate bandwidth saturation. 3 source machines with private addresses targeting one destination machine with a private address would be a DDoS. With source consisting of class C addresses and destination of class B. Seeing traffic from three machines target one machine in a different subnet would indicate anomalous activity. Upon further investigation, this may reveal itself to be benign or malicious. There isn't enough data to confirm that yet, which leads me to view this activity as anomalous.
Source: Adapted from community discussion — Popeyes_Chicken
A newly hired security manager in a SOC wants to improve efficiency by automating routine tasks. Which of the following SOC tasks is most suitable for automation?
Answer: C
Reviewing logs and alerts is one of the most automatable tasks in a SOC. SIEM tools integrated with a SOAR platform can analyze logs and flag potential security anomalies / threats for further review. Generating incident reports can be automated, but often requires customization and human input. Especially for detailed or nuanced incidents.
Source: Adapted from community discussion — Popeyes_Chicken
An analyst notices there is an internal device sending HTTPS traffic with additional characters in the header to a known-malicious IP in another country. Which of the following describes what the analyst has noticed?
Answer: A
The analyst has noticed a behavior known as "beaconing." A. Beaconing is a term used in cybersecurity to describe a pattern where an internal device, often compromised or part of a botnet, sends periodic and regular communications to a command and control server or a known-malicious IP address. These communications are often designed to be stealthy and can carry additional information, such as commands or data, within the headers or payloads of seemingly innocuous traffic like HTTPS. The other options, B, C, and D, describe different security-related concepts
Source: Adapted from community discussion — nmap_king_22
Which of the following is a circumstance in which a security operations manager would most likely consider using automation?
Answer: A
A system that provides the user interface for a critical server has potentially been corrupted by malware. Which of the following is the best recommendation to ensure business continuity?
Answer: B
A System Isolation stops malware from spreading, but it doesn’t restore the system. This is an initial containment step, not a business continuity solution. I think the best answer is B. Reimaging, because is the most reliable way to restore a compromised system to a clean state.
Source: Adapted from community discussion — ruelgo
Which of following attack methodology frameworks should a cybersecurity analyst use to identify similar TTPs utilized by nation-state actors?
Answer: D
An XSS vulnerability was reported on one of the public websites of a company. The security department confirmed the finding and needs to provide a recommendation to the application owner. Which of the following recommendations will best prevent this vulnerability from being exploited? (Choose two.)
Answer: CF
I think fixing the server with a WAF because its public facing website and taking the website off online is possible because it mentions "one of the public websites of a company"
Source: Adapted from community discussion — 1403ad2
A security analyst is reviewing a recent vulnerability scan report for a new server infrastructure. The analyst would like to make the best use of time by resolving the most critical vulnerability first. The following information is provided:

Which of the following should the analyst concentrate remediation efforts on first?
Answer: B
Keyboard:J Kmove between questionsA–Dselect an answerRshow or hide the answer← →change page
CS0-003 practice, question 261. 527 questions available.
Version 1.0.0. How we source questions