Question 531 · 578 in bank
SIMULATION - Guidelines - This is a lab item in which tasks will be performed on virtual devices. • Refer to the Tasks tab to view the tasks for this lab item. • Refer to the Topology tab to access the device console(s) and perform the tasks. • Console access is available for all required devices by clicking the device icon or using the tab(s) above the console window. • All necessary preconfigurations have been applied. • Do not change the enable password or hostname for any device. • Save your configurations to NVRAM before moving to the next item. • Click Next at the bottom of the screen to submit this lab and move to the next question. • When Next is clicked, the lab closes and cannot be reopened. Topology -

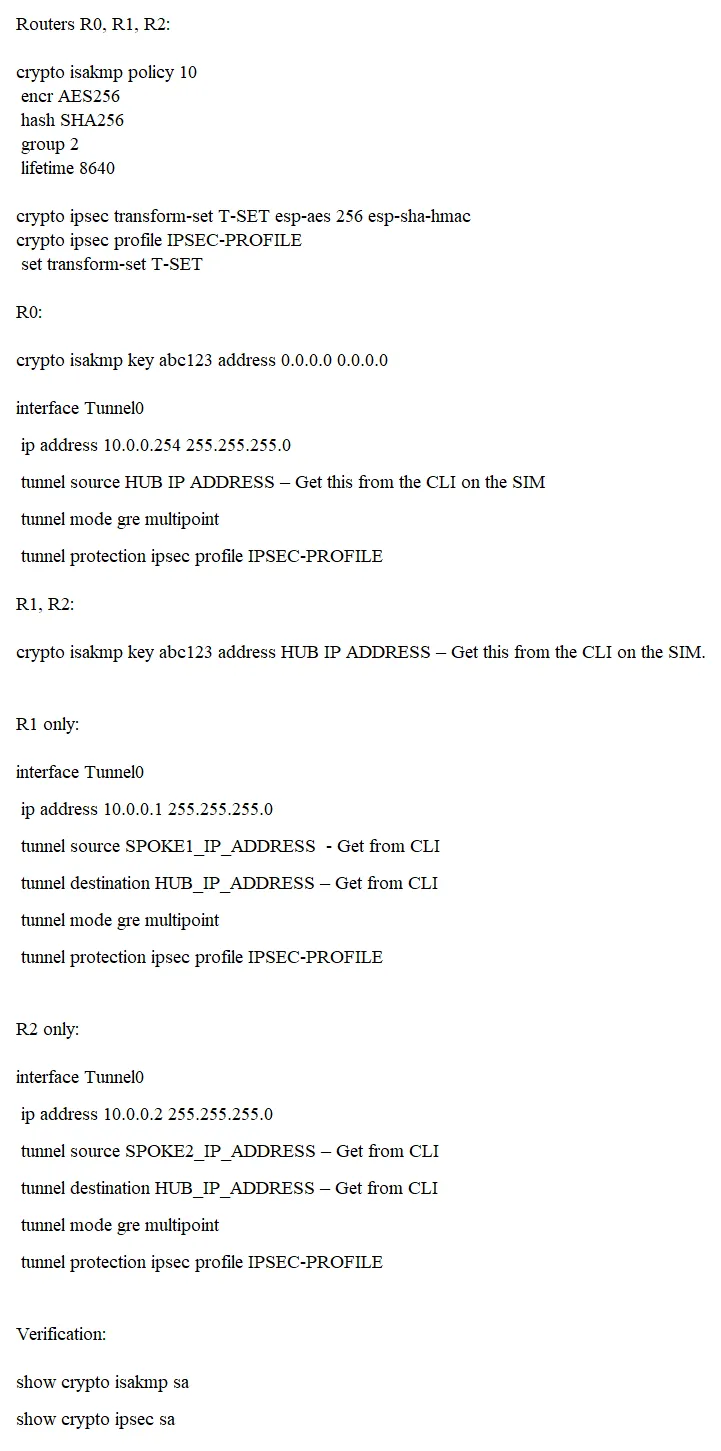
Tasks - Configure IPSec security policy on tunnel interfaces to ensure data confidentiality and integrity where mGRE tunnels are up and running between HUB and SPOKE routers. 1. Configure the ISAKMP policy parameters with the following attributes: • AES256 • SHA256 • Group2 • lifetime 86400 2. Ensure that GRE IP Header should be encrypted inside the IPSec packet. Verify IPSec security association and ISAKMP encrypted key. Use ISAKMP key "abc123". 3. Configure a flexible ISAKMP Policy on the HUB to add peers that have the dynamic IP addresses where SPOKES must add HUB IP static entry using an encrypted key. Use a single command to configure it. Use IPSec phase-2 transform-set name as T-SET and IPSec Profile name as ’IPSEC-PROFILE’.

This is an interactive task on the real exam — a drag-and-drop, hotspot or ordering question. There is nothing to select here, so the answer is shown below for reference.
Show the answer figure
Answer: See figure below
Explanation
i had this lab in the exam, the only differences were: 1. configure MD5 instead of SHA256. 2. the name of ipsec profile was different in the exam (be aware of the details of names in the exam, they are not always the same). on all Routers: (config)#crypto isakmp policy 10 (config-isakmp)#encryption aes256 (config-isakmp)#hash md5 (config-isakmp)#authentication pre-share (config-isakmp)#group 2 (config-isakmp)#lifetime 86400 (config)#crypto isakmp key abc123 address 0.0.0.0 (config)#crypto ipsec transform-set T-SET esp-aes256 esp-md5-hmac (config)#crypto ipsec profile IPSEC-PROFILE (config-ipsec-profile)#set transform-set T-SET (config)#int tunnel 0 (config-if)#tunnel source (phisical interface or phisical ip) (config-if)#tunnel protection ipsec profile IPSEC-PROFILE there´s no need for this command "tunnel mode gre multipoint" cop r st
Source: Adapted from community discussion — [Removed]