Question 81 · 654 in bank
Which factor must be considered when choosing the on-premise solution over the cloud-based one?
Show answer
Answer: D
Implementing and Operating Cisco Security Core Technologies (SCOR)654 questions across 66 pages are complete and free, with no account or card.
654 questions in this bank
Free access · progress saved on this device
Which factor must be considered when choosing the on-premise solution over the cloud-based one?
Answer: D
An engineer has been tasked with implementing a solution that can be leveraged for securing the cloud users, data, and applications. There is a requirement to use the Cisco cloud-native CASB and cloud cybersecurity platform. What should be used to meet these requirements?
Answer: B
Cisco Cloudlock is a Cloud-Based Security Broker (CASB). "A CASB provides visibility and compliance checks, protects data against misuse and exfiltration, and provides threat protections against malware like ransomware." So basically Cloudlock is a DLP device.
Source: Adapted from community discussion — statikd
In an IaaS cloud services model, which security function is the provider responsible for managing?
Answer: C
The NIST's definition of cloud computing defines infrastructure as a service as: The capability provided to the consumer is to provision processing, storage, networks, and other fundamental computing resources where the consumer is able to deploy and run arbitrary software, which can include operating systems and applications. The consumer does not manage or control the underlying cloud infrastructure but has control over operating systems, storage, and deployed applications; and possibly limited control of select networking components (e.g., host firewalls). IaaS-cloud providers supply these resources on-demand from their large pools of equipment installed in data centers. For wide-area connectivity, customers can use either the Internet or carrier clouds (dedicated virtual private networks). To deploy their applications, cloud users install operating-system images and their application software on the cloud infrastructure. In this model, the cloud user patches and maintains the operating systems and the application software. Cloud providers typically bill IaaS services on a utility computing basis: cost reflects the amount of resources allocated and consumed. IT'S ANSWER A!!!!
Source: Adapted from community discussion — klu16
An organization wants to secure users, data, and applications in the cloud. The solution must be API-based on operate as a cloud-native CASB. Which solution must be used for this implementation?
Answer: B
DRAG DROP - Drag and drop the cloud security assessment components from the left onto the definitions on the right. Select and Place:
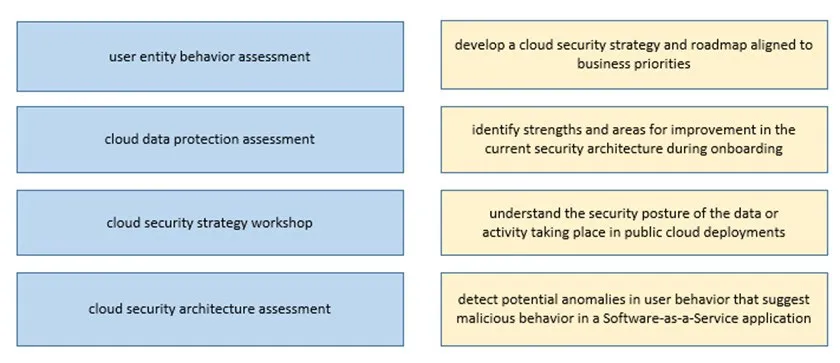
This is an interactive task on the real exam — a drag-and-drop, hotspot or ordering question. There is nothing to select here, so the answer is shown below for reference.
Answer: See figure below
Answer should be cloud security strategy workshop cloud security architecture assessment cloud data protection assessment user entity behaviour assessment https://www.cisco.com/c/dam/m/en_sg/dc-innovation/assets/pdfs/securing-your-multicloud-journey.pdf
Source: Adapted from community discussion — Max95

An organization wants to secure data in a cloud environment. Its security model requires that all users be authenticated and authorized. Security configuration and posture must be continuously validated before access is granted or maintained to applications and data. There is also a need to allow certain application traffic and deny all other traffic by default. Which technology must be used to implement these requirements?
Answer: B
Microsegmentation is NOT for posturing checking. All the requirements criteria is met by Access Control Policies where you can define in ISE, Authentication, Authorization (Assign SGT in this part, which is the microsegmentation), then use Access List to deny or allow traffic Answer is B
Source: Adapted from community discussion — jaciro11
Which cloud model is a collaborative effort where infrastructure is shared and jointly accessed by several organizations from a specific group?
Answer: A
community cloud model A community cloud model is a collaborative effort where infrastructure is shared and jointly accessed by several organizations from a specific group that share specific computing concerns such as, security, compliance or jurisdiction considerations.
Source: Adapted from community discussion — Thusi26
What are two DDoS attack categories? (Choose two.)
Answer: AE
Volume Based Attacks. Includes UDP floods, ICMP floods, and other spoofed-packet floods. ... Protocol Attacks. Includes SYN floods, fragmented packet attacks, Ping of Death, Smurf DDoS and more. ... Application Layer Attacks.
Source: Adapted from community discussion — SirFrates24
How does Cisco Workload Optimization Manager help mitigate application performance issues?
Answer: A
"Workload Optimization Manager continuously analyzes workload consumption, costs, and compliance constraints and automatically allocates resources in real time." Source: https://www.cisco.com/c/dam/en/us/products/collateral/servers-unified-computing/ucs-s-series-storage-servers/whitepaper-c11-741392.pdf
Source: Adapted from community discussion — idto
Which DevSecOps implementation process gives a weekly or daily update instead of monthly or quarterly in the applications?
Answer: A
Reference: https://devops.com/how-to-implement-an-effective-ci-cd-pipeline/
Source: Adapted from community discussion — idto
Keyboard:J Kmove between questionsA–Dselect an answerRshow or hide the answer← →change page
350-701 practice, question 81. 654 questions available.
Version 1.0.0. How we source questions