Question 101 · 654 in bank
What is the primary role of the Cisco Email Security Appliance?
Show answer
Answer: B
Implementing and Operating Cisco Security Core Technologies (SCOR)654 questions across 66 pages are complete and free, with no account or card.
654 questions in this bank
Free access · progress saved on this device
What is the primary role of the Cisco Email Security Appliance?
Answer: B
Which two services must remain as on-premises equipment when a hybrid email solution is deployed? (Choose two.)
Answer: DE
Reference: https://www.cisco.com/c/dam/en/us/td/docs/security/ces/overview_guide/Cisco_Cloud_Hybrid_Email_Security_Overview_Guide.pdf
Source: Adapted from community discussion — idto
An organization is receiving SPAM emails from a known malicious domain. What must be configured in order to prevent the session during the initial TCP communication?
Answer: A
"You can configure your Email Security Appliance (ESA) to restrict connections by adding any of these items to Sender Groups which use Mail Flow Policies: IP range Specific host or domain name SenderBase Reputation Service (SBRS) "organization" classification SBRS score range DNS List query response Each Mail Flow Policy has an access rule, such as ACCEPT, REJECT, RELAY, CONTINUE, and TCPREFUSE. A host that attempts to establish a connection to your ESA and matches a Sender Group using a TCPREFUSE access rule is not allowed to connect to your ESA." Source (2014): https://www.cisco.com/c/en/us/support/docs/security/email-security-appliance/118007-configure-esa-00.html Newer (2021) - the same but TCPREFUSE is replaced by "TCP refuse": https://www.cisco.com/c/en/us/support/docs/security/email-security-appliance/216842-understand-parameters-related-to-mail-fl.html
Source: Adapted from community discussion — NikoNiko
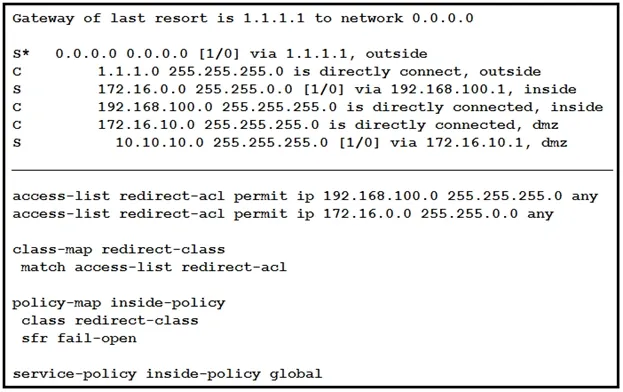
Refer to the exhibit. What is a result of the configuration?
Answer: D
The answer is definitly D. The ACL's match 192.168.100.0 to 192.168.100.255 and 172.16.0.0 to 172.16.255.255. The DMZ and inside network fall in those ranges.
Source: Adapted from community discussion — LynenDutzow
An organization received a large amount of SPAM messages over a short time period. In order to take action on the messages, it must be determined how harmful the messages are and this needs to happen dynamically. What must be configured to accomplish this?
Answer: D
What are two differences between a Cisco WSA that is running in transparent mode and one running in explicit mode? (Choose two.)
Answer: AD
A and D are correct. - In explicit proxy mode, users are configured to use a web proxy and the web traffic is sent directly to the Cisco WSA. In contrast, in transparent proxy mode the Cisco WSA intercepts user's web traffic redirected from other network devices, such as switches, routers, or firewalls.
Source: Adapted from community discussion — wfexco
Which technology is used to improve web traffic performance by proxy caching?
Answer: A
Which proxy mode must be used on Cisco WSA to redirect TCP traffic with WCCP?
Answer: A
How the WSA HTTP proxy obtains the client's request can be defined as one of two ways: Transparently or Explicitly. Deployment: Transparent Method: WCCP Description: A WCCP v2 enabled device (typically a router, switch, PIX, or ASA) redirects port 80 https://www.cisco.com/c/en/us/support/docs/security/web-security-appliance/117940-qa-wsa-00.html
Source: Adapted from community discussion — cyberwhizzy0
Which two request methods of REST API are valid on the Cisco ASA Platform? (Choose two.)
Answer: AC
ans is correct. Available request methods are: GET – Retrieves data from the specified object. PUT – Adds the supplied information to the specified object; returns a 404 Resource Not Found error if the object does not exist. POST – Creates the object with the supplied information. DELETE – Deletes the specified object. PATCH – Applies partial modifications to the specified object.
Source: Adapted from community discussion — sajoz123
How does Cisco Advanced Phishing Protection protect users?
Answer: B
Cisco® Advanced Phishing Protection provides sender authentication and BEC detection capabilities. It uses advance machine learning techniques, real time behavior analytics, relationship modeling and telemetry to protect against identity deception–based threats. answer should be B
Source: Adapted from community discussion — SirFrates24
Keyboard:J Kmove between questionsA–Dselect an answerRshow or hide the answer← →change page
350-701 practice, question 101. 654 questions available.
Version 1.0.0. How we source questions