Question 311 · 385 in bank
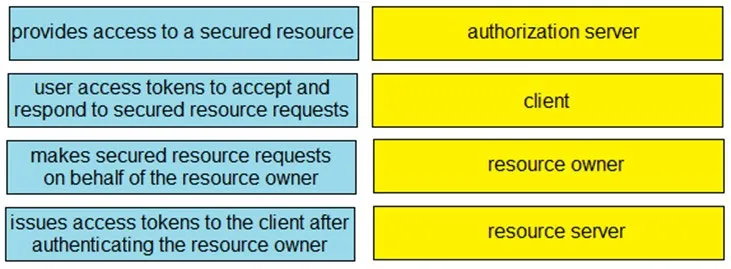
In the three-legged OAuth2 authorization workflow, which entity grants access to a protected resource?
Show answer
Answer: A
Explanation
Cisco DEVCOR Study Guide 350-901 2022 edition, page 69, section 2.5, "Describe the steps in the OAuth2 three‐legged authorization code grant flow": (B) In this step, the resource owner decides whether to grant the requested access to the client application. In the case of Google, it would display a consent window that shows the name of the application, Google services that it is requesting access to, and a summary of the scopes of access to be granted. The user can then consent to grant access or refuse the request. I'll go with A
Source: Adapted from community discussion — [Removed]