Question 301 · 385 in bank
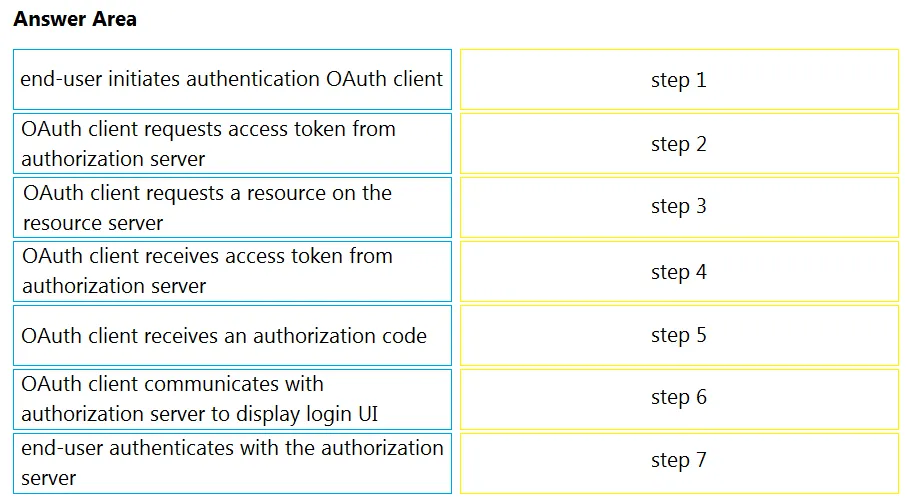
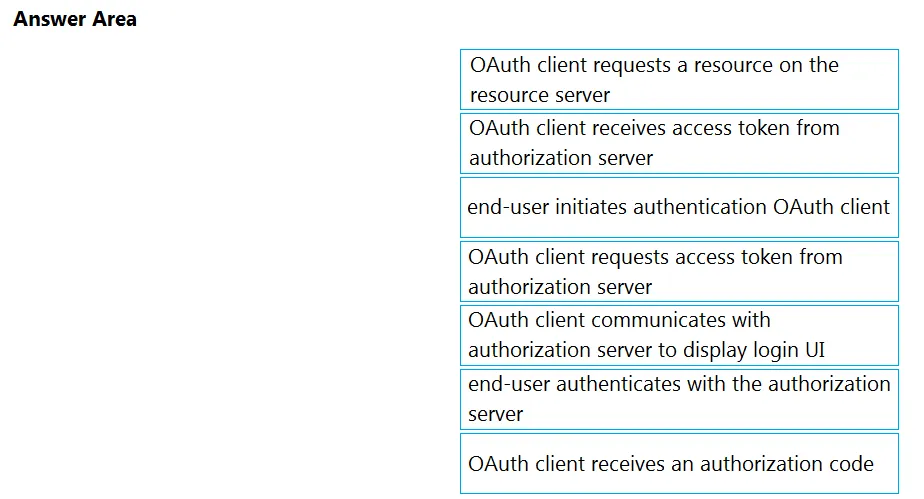
Select 2An application uses OAuth to get access to several API resources on behalf of an end user. What are two valid parameters to send to the authorization server as part of the first step of an authorization code grant flow? (Choose two.)
Show answer
Answer: AD
Explanation
"A" and "D" Explanation: The authorization code is a temporary code that the client will exchange for an access token. The code itself is obtained from the authorization server where the user gets a chance to see what the information the client is requesting, and approve or deny the request. The following parameters are used to make the authorization request. You should build a query string with the below parameters, appending that to the application’s authorization endpoint obtained from its documentation. • client_id o The client_id is the identifier for your app. You will have received a client_id when first registering your app with the service. • redirect_uri (optional) o The redirect_uri may be optional depending on the API, but is highly recommended. This is the URL to which you want the user to be redirected after the authorization is complete. This must match the redirect URL that you have previously registered with the service. • scope (optional) o Include one or more scope values (space-separated) to request additional levels of access. The values will depend on the particular service.
Source: Adapted from community discussion — blezzzo