Question 341 · 610 in bank
Which Palo Alto Networks VM-Series firewall is valid?
Palo Alto Networks Certified Network Security Engineer610 questions across 61 pages are complete and free, with no account or card.
610 questions in this bank
Free access · progress saved on this device
Which Palo Alto Networks VM-Series firewall is valid?
Which three options does Panorama offer for deploying dynamic updates to its managed devices? (Choose three.)
Answer: BDE
A network security engineer configured IP multicast in the virtual router to support a new application. Users in different network segments are reporting that they are unable to access the application. What must be enabled to allow an interface to forward multicast traffic?
Answer: D
You must enable IP multicast for the virtual router, configure Protocol Independent Multicast (PIM) on the ingress and egress interfaces, and configure Internet Group Management Protocol (IGMP) on receiver-facing interfaces. https://docs.paloaltonetworks.com/pan-os/10-1/pan-os-networking-admin/ip-multicast/configure-ip-multicast
Source: Adapted from community discussion — chrisy042

Review the screenshots and consider the following information: • FW-1 is assigned to the FW-1_DG device group and FW-2 is assigned to OFFICE_FW_DG • There are no objects configured in REGIONAL_DG and OFFICE_FW_DG device groups Which IP address will be pushed to the firewalls inside Address Object Server-1?
Answer: D
The answer is only one - D. FW-1 will get the value from FW-DG1 while FW-2 will get the value from the Shared DG since no values are present in its parent DGs. https://docs.paloaltonetworks.com/panorama/9-1/panorama-admin/manage-firewalls/manage-device-groups/manage-precedence-of-inherited-objects
Source: Adapted from community discussion — chrisy042
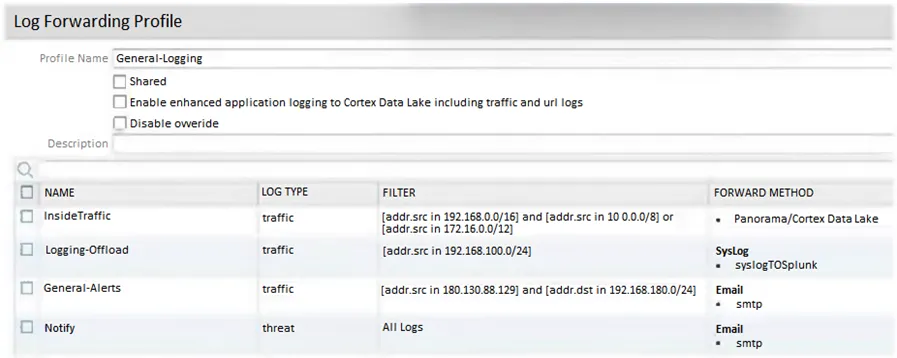
Given the Sample Log Forwarding Profile shown, which two statements are true? (Choose two.)
Answer: AC
Sadly, none of these choices are technically correct. @obatel pointed out that the RFC 1918 filter uses AND condition instead of OR @BTSeeYa pointed out that A stated 'all traffic' instead of 'all traffic logs' A would be correct if they say 'all traffic logs' instead of simply 'all traffic' B would be correct if they said email instead of Panorama C would be correct if the RFC 1918 filter used OR instead of AND D would be correct if they change the subnet to one that fell within the RFC 1918 filter AND if they referred to 'traffic logs' Since A and C are the closest to correct choices, I guess that's what I'd choose on the test? [i just hope I don't see too many questions like this one on my test]
Source: Adapted from community discussion — examtopicstroilevw
Which benefit do policy rule UUIDs provide?
Answer: C
C https://docs.paloaltonetworks.com/pan-os/10-2/pan-os-admin/policy/enumeration-of-rules-within-a-rulebase To keep track of rules within a rulebase, you can refer to the rule number, which changes depending on the order of a rule in the rulebase. The rule number determines the order in which the firewall applies the rule. The universally unique identifier (UUID) for a rule never changes even if you modify the rule, such as when you change the rule name. The UUID allows you to track the rule across rule bases even after you deleted the rule.
Source: Adapted from community discussion — confusion
A system administrator runs a port scan using the company tool as part of vulnerability check. The administrator finds that the scan is identified as a threat and is dropped by the firewall. After further investigating the logs the administrator finds that the scan is dropped in the Threat Logs. What should the administrator do to allow the tool to scan through the firewall?
Answer: B
To further clarify it is B: There is no such section in DoS Protection Profiles The other options can open the gates to non-approved reconnaissance.
Source: Adapted from community discussion — myname_1
A customer wants to combine multiple Ethernet interfaces into a single virtual interface using link aggregation. What is the valid naming convention for aggregate interfaces?
Answer: C
In the field adjacent to the read-only Interface Name , enter a number to identify the aggregate group. The range is 1 to the maximum number of aggregate interface groups supported by the firewall. https://docs.paloaltonetworks.com/pan-os/10-1/pan-os-networking-admin/configure-interfaces/configure-an-aggregate-interface-group
Source: Adapted from community discussion — chrisy042
A company with already deployed Palo Alto firewalls has purchased their first Panorama server. The security team has already configured all firewalls with the Panorama IP address and added all the firewall serial numbers in Panorama. What are the next steps to migrate configuration from the firewalls to Panorama?
Answer: C
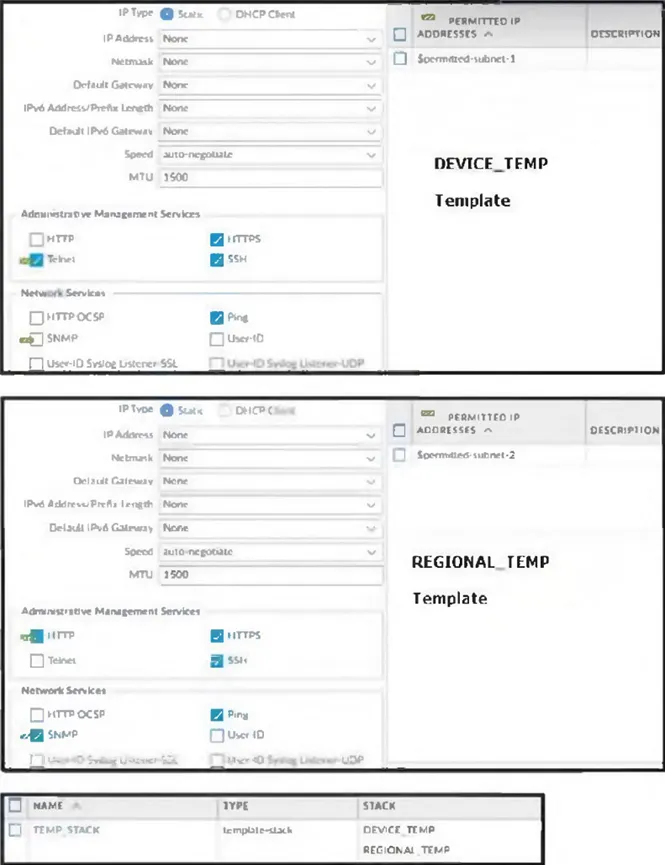
Based on the screenshots above, and with no configuration inside the Template Stack itself, what access will the device permit on its Management port?
Answer: A
I just tested in my panorama by making the same thing and when you have a permitted IP in both templates it only pushes config from the top one. Making A the only possible answer.
Source: Adapted from community discussion — procheeseburger
Keyboard:J Kmove between questionsA–Dselect an answerRshow or hide the answer← →change page
PCNSE practice, question 341. 610 questions available.
Version 1.0.0. How we source questions