Question 1 · 610 in bank
Which CLI command is used to simulate traffic going through the firewall and determine which Security policy rule, NAT translation, static route, or PBF rule will be triggered by the traffic?
Show answer
Answer: C
Palo Alto Networks Certified Network Security Engineer610 questions across 61 pages are complete and free, with no account or card.
610 questions in this bank
Free access · progress saved on this device
Which CLI command is used to simulate traffic going through the firewall and determine which Security policy rule, NAT translation, static route, or PBF rule will be triggered by the traffic?
Answer: C
If a template stack is assigned to a device and the stack includes three templates with overlapping settings, which settings are published to the device when the template stack is pushed?
Answer: A
Correct A If templates have duplicate settings, Panorama will push only the settings of the higher template in the list to the assigned firewalls https://www.paloaltonetworks.com/documentation/80/pan-os/web-interface-help/panorama-web-interface/panorama-templates/template-stacks
Source: Adapted from community discussion — Edu147
View the GlobalProtect configuration screen capture. What is the purpose of this configuration?
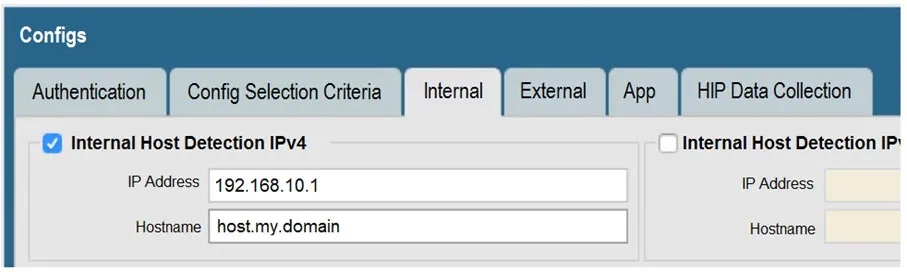
Which three user authentication services can be modified to provide the Palo Alto Networks NGFW with both usernames and role names? (Choose three.)
Answer: AEF
Correct: A,E,F The administrative accounts are DEFINED on an external SAML, TACACS+, or RADIUS server. The server performs both authentication and authorization. For authorization, you define Vendor-Specific Attributes (VSAs) on the TACACS+ or RADIUS server, or SAML attributes on the SAML server. PAN-OS maps the attributes to administrator roles, access domains, user groups, and virtual systems that you define on the firewall. Kerberos, LDAP, and PAP required the admin account to be locally defined on the firewall. https://docs.paloaltonetworks.com/pan-os/9-1/pan-os-admin/firewall-administration/manage-firewall-administrators/administrative-authentication.html
Source: Adapted from community discussion — ChiaPet75
What is exchanged through the HA2 link?
Answer: C
Correct: C "Data Link—The HA2 link is used to synchronize sessions, forwarding tables, IPSec security associations and ARP tables between devices in an HA pair. Data flow on the HA2 link is always unidirectional (except for the HA2 keep-alive); it flows from the active device to the passive device." https://docs.paloaltonetworks.com/vm-series/9-0/vm-series-deployment/set-up-the-vm-series-firewall-on-aws/high-availability-for-vm-series-firewall-on-aws/ha-links#:~:text=%E2%80%94The%20HA1%20link%20is%20used,port%20is%20used%20for%20HA1.
Source: Adapted from community discussion — ChiaPet75
Which prerequisite must be satisfied before creating an SSH proxy Decryption policy?
Answer: B
Per the Palo Alto URL provided: Configuring SSH Proxy does not require certificates and the key used to decrypt SSH sessions is generated automatically on the firewall during boot up. With SSH decryption enabled, all SSH traffic identified by the policy is decrypted and identified as either regular SSH traffic or as SSH tunneled traffic. SSH tunneled traffic is blocked and restricted according to the profiles configured on the firewall. Traffic is re-encrypted as it exits the firewall. Answer B is correct.
Source: Adapted from community discussion — MyWil
A customer wants to combine multiple Ethernet interfaces into a single virtual interface using link aggregation. Which two formats are correct for naming aggregate interfaces? (Choose two.)
Answer: AC
I guess AC but none are correct because the dot would be for subinterfaces on the aggregate... still the aggregate would be numbered... e.g. ae1 and ae8 would be valid
Source: Adapted from community discussion — Questionario
Which three authentication factors does PAN-OSֲ® software support for MFA? (Choose three.)
Answer: ADE
VPN traffic intended for an administrator's firewall is being maliciously intercepted and retransmitted by the interceptor. When creating a VPN tunnel, which protection profile can be enabled to prevent this malicious behavior?
Answer: B
Terrible question as usual with PANW tests. There is no "Replay protection profile" this is a checkbox in the IPSec tunnel creation part (-_-)...
Source: Adapted from community discussion — Pretorian
An administrator has configured a QoS policy rule and a QoS Profile that limits the maximum allowable bandwidth for the YouTube application. However, YouTube is consuming more than the maximum bandwidth allotment configured. Which configuration step needs to be configured to enable QoS?
Answer: A
QoS implementation on a Palo Alto Networks firewall begins with three primary configuration components that support a full QoS solution: a QoS policy, a QoS Profile, and configuration of the QoS egress interface. study guide page 225
Source: Adapted from community discussion — Ab121213
Keyboard:J Kmove between questionsA–Dselect an answerRshow or hide the answer← →change page
PCNSE practice, question 1. 610 questions available.
Version 1.0.0. How we source questions