Question 111 · 496 in bank
HOTSPOT - You have an Azure Active Directory (Azure AD) tenant that contains the users shown in the following table.

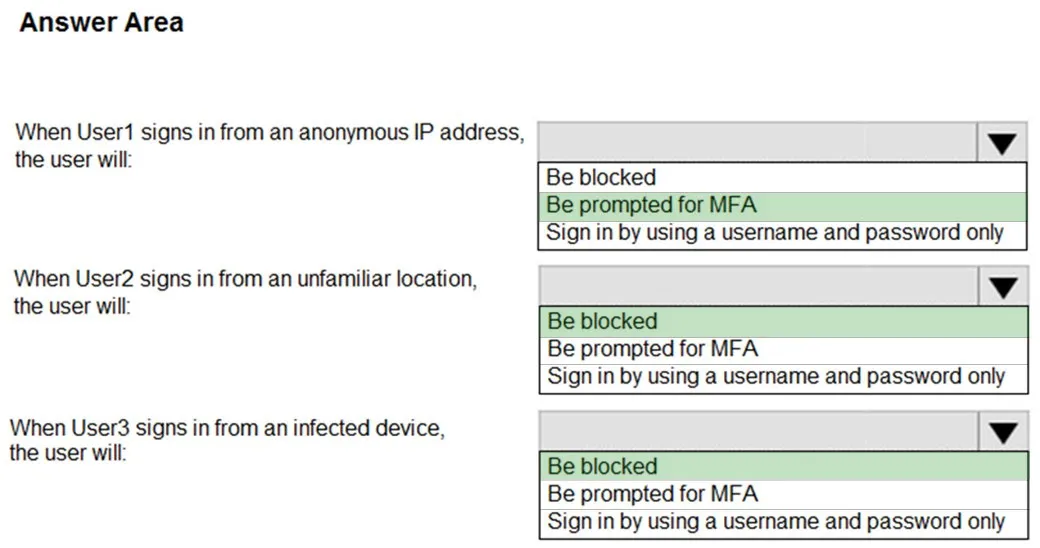
You create and enforce an Azure AD Identity Protection sign-in risk policy that has the following settings: ✑ Assignments: Include Group1, exclude Group2 ✑ Conditions: Sign-in risk level: Medium and above ✑ Access: Allow access, Require multi-factor authentication You need to identify what occurs when the users sign in to Azure AD. What should you identify for each user? To answer, select the appropriate options in the answer area. NOTE: Each correct selection is worth one point. Hot Area:
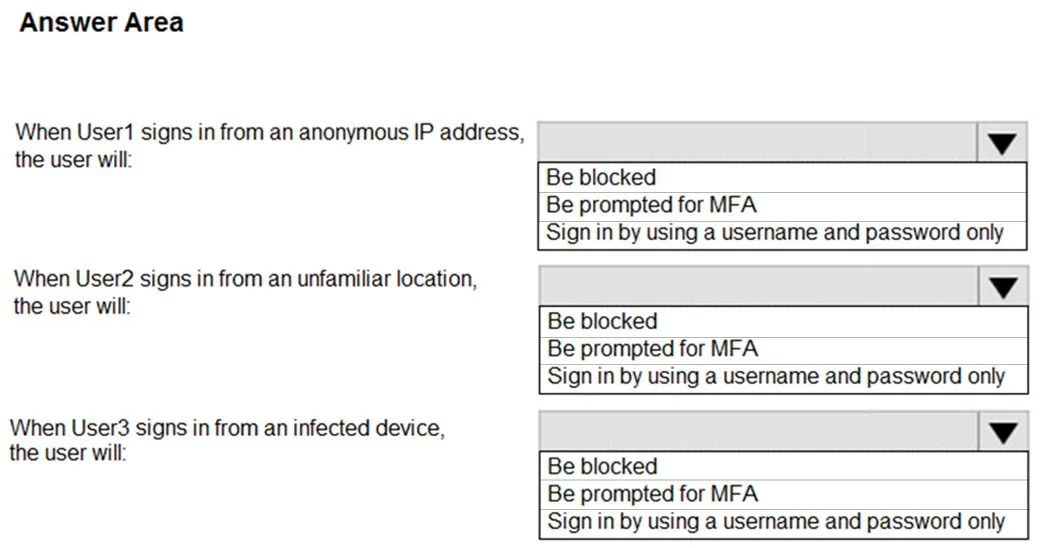
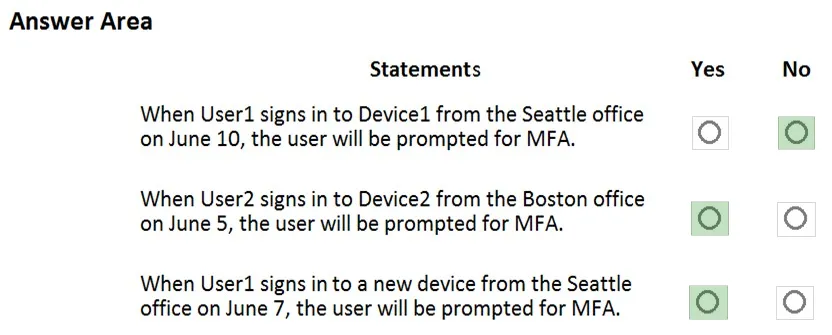
This is an interactive task on the real exam — a drag-and-drop, hotspot or ordering question. There is nothing to select here, so the answer is shown below for reference.
Show the answer figure
Answer: See figure below
Explanation
References: http://www.rebeladmin.com/2018/09/step-step-guide-configure-risk-based-azure-conditional-access-policies/ https://docs.microsoft.com/en-us/azure/active-directory/identity-protection/concept-identity-protection-policies https://docs.microsoft.com/en-us/azure/active-directory/identity-protection/concept-identity-protection-risks
Source: Adapted from community discussion — Bjarki2330