Question 141 · 232 in bank
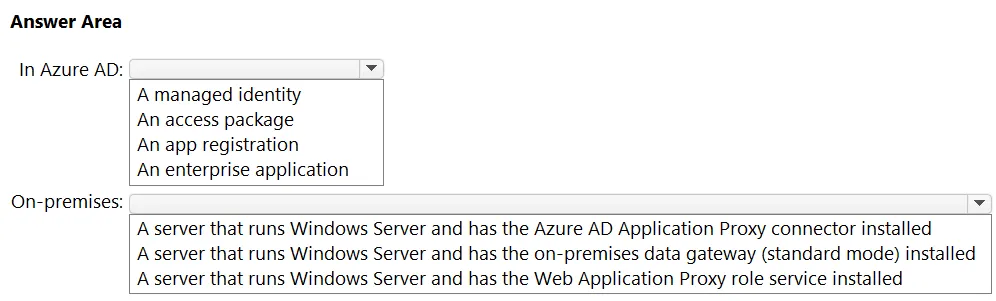
HOTSPOT - Your on-premises network contains an Active Directory Domain Services (AD DS) domain. The domain contains a server named Server1. Server1 contains an app named App1 that uses AD DS authentication. Remote users access App1 by using a VPN connection to the on-premises network. You have an Azure AD tenant that syncs with the AD DS domain by using Azure AD Connect. You need to ensure that the remote users can access App1 without using a VPN. The solution must meet the following requirements: • Ensure that the users authenticate by using Azure Multi-Factor Authentication (MFA). • Minimize administrative effort. What should you include in the solution? To answer, select the appropriate options in the answer area. NOTE: Each correct selection is worth one point.
This is an interactive task on the real exam — a drag-and-drop, hotspot or ordering question. There is nothing to select here, so the answer is shown below for reference.
Show the answer figure
Answer: See figure below
Explanation
The application doesn't do the authentication, this is handled by the App Proxy service, see https://learn.microsoft.com/en-us/entra/identity/app-proxy/application-proxy-security The service requires an Enterprise Application to be created, see https://learn.microsoft.com/en-us/entra/identity/app-proxy/application-proxy-add-on-premises-application - see section "Add an on-premises app to Microsoft Entra ID", "2. Browse to Identity > Applications > Enterprise applications".
Source: Adapted from community discussion — kodathedog