Question 11 · 24 in bank
Refer to the exhibit.
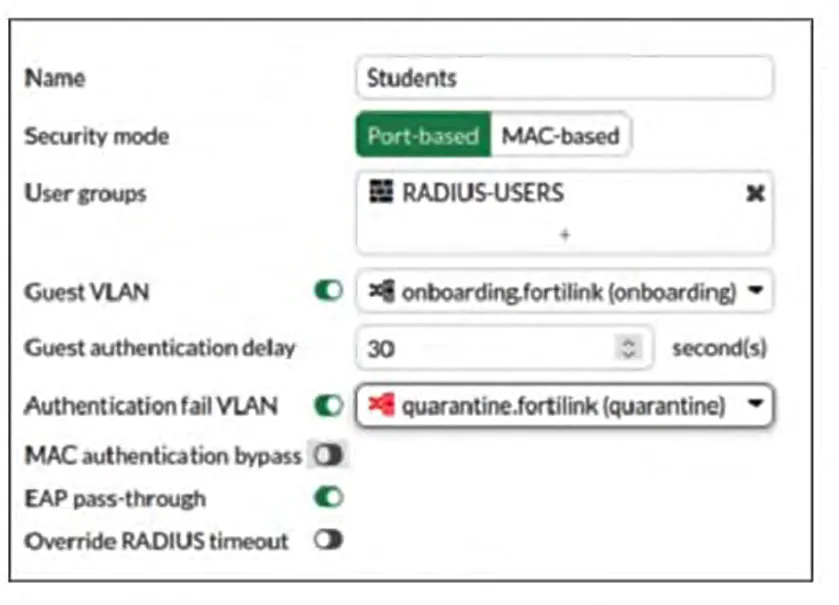
The security port policy is configured as shown in the exhibit. Which behavior occurs if a device connected to the port that does not support 802.1X?
Show answer
Answer: B
Fortinet NSE 5 - FortiSwitch 7.6 Administrator24 questions across 3 pages are complete and free, with no account or card.
24 questions in this bank
Free access · progress saved on this device
Refer to the exhibit.
The security port policy is configured as shown in the exhibit. Which behavior occurs if a device connected to the port that does not support 802.1X?
Answer: B
When Dynamic Host Configuration Protocol (DHCP) snooping is enabled on a FortiSwitch VLAN, which two statements are true? (Choose two.)
Answer: AC
Refer to the exhibit. Routing Monitor -
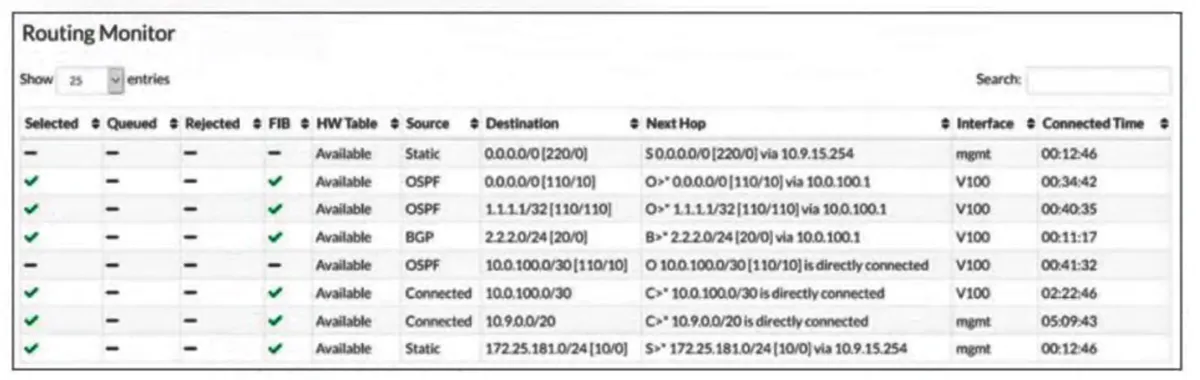
The routing monitor displays multiple route entries, but only some are installed in the forwarding information base (FIB). After analyzing the two route entries with the destination 0.0.0.0/0, which statement correctly describe why one of these routes is not installed in the FIB?
Answer: C
You are configuring VLANs on a FortiSwitch device managed by FortiGate. Which two statements accurately describe VLAN assignment requirements and behavior on FortiSwitch ports? (Choose two.)
Answer: BC
Refer to the exhibit. Network Topology -
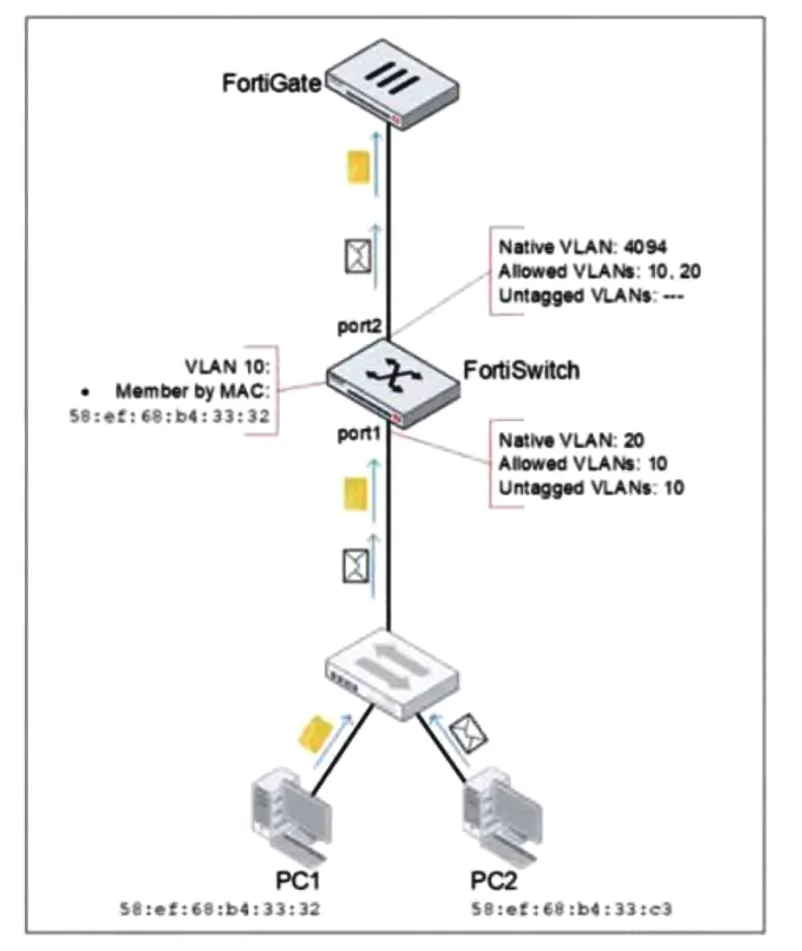
PC1 and PC2 are connected to port1 on FortiSwitch. Which VLAN tags will FortiSwitch apply when forwarding PC1 and PC2 traffic out of port2?
Answer: C
Refer to the exhibit. Topology view -
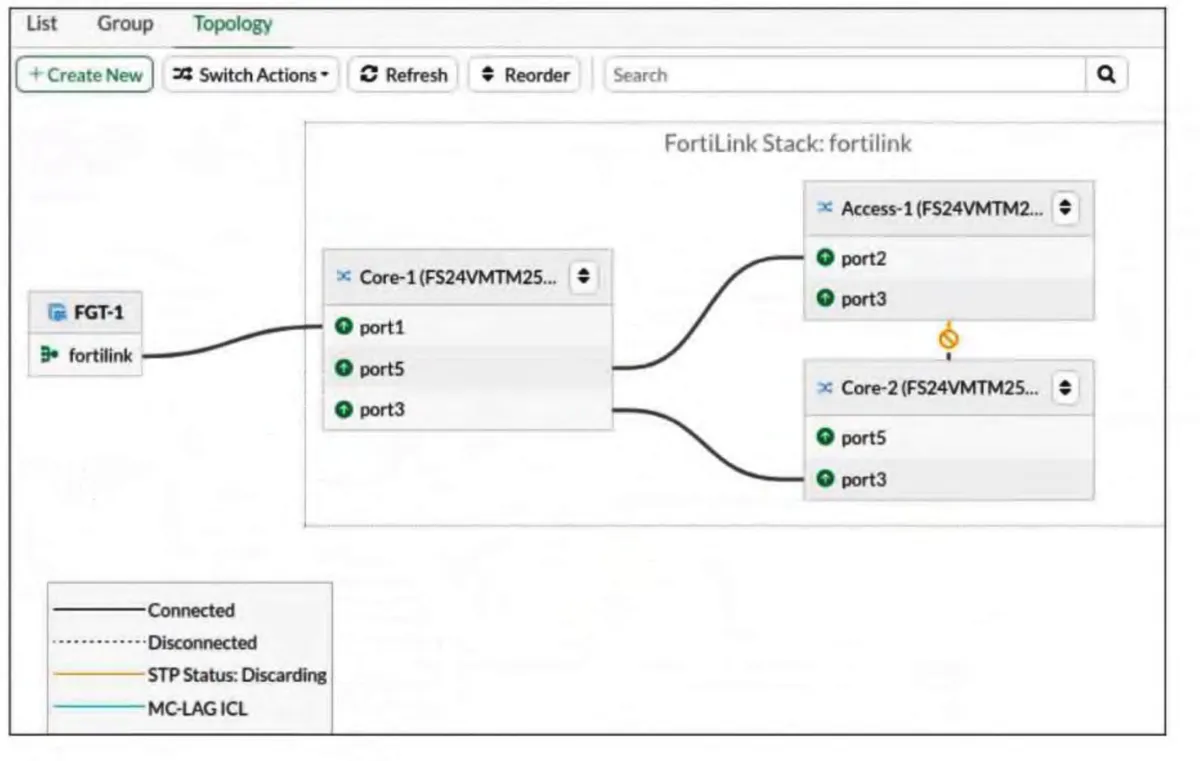
You just connected three FortiSwitch devices: Core-1, Core-2, and Access-1. Core-1 and Core-2 both connect to Access-1 for redundancy. All switches are managed by FortiGate, which uses port4 as the FortiLink interface. After you enable the uplink ports on Core-2, you notice that port3 on Access-1 enters the Discarding STP state. What is the most likely cause of this behavior?
Answer: D
When you change FortiSwitch management mode from standalone to managed, what happens to the existing standalone configuration?
Answer: C
In which two ways can you assign a FortiSwitch port to a VDOM using a multi-tenancy setup? (Choose two.)
Answer: BC
You enable Dynamic Host Configuration Protocol (DHCP) snooping on a VLAN and configure a FortiSwitch port as trusted for DHCP snooping. What additional step is required to configure the port as trusted for Dynamic ARP Inspection (DAI)?
Answer: C
Which three are valid actions that a FortiSwitch access control list (ACL) can apply to matching traffic? (Choose three.)
Answer: BCE
Keyboard:J Kmove between questionsA–Dselect an answerRshow or hide the answer← →change page
NSE5_FSW_AD-7.6 practice, question 11. 24 questions available.
Version 1.0.0. How we source questions