Question 431 · 527 in bank
After several tabletop exercises, the cybersecurity team is underperforming against MTTR and MTTD. Which of the following would help the team achieve improved performance?
Show answer
Answer: C
CompTIA Cybersecurity Analyst (CySA+)527 questions across 53 pages are complete and free, with no account or card.
527 questions in this bank
Free access · progress saved on this device
After several tabletop exercises, the cybersecurity team is underperforming against MTTR and MTTD. Which of the following would help the team achieve improved performance?
Answer: C
An IDS is triggered during after-hours operations. The indicator records an abnormal amount of SYN requests being sent to port 21 from numerous external systems. A security analyst reports this information to the IR team for further investigation. Which of the following best describes this incident?
Answer: D
A security analyst reviews a packet capture and identifies the following output as anomalous:
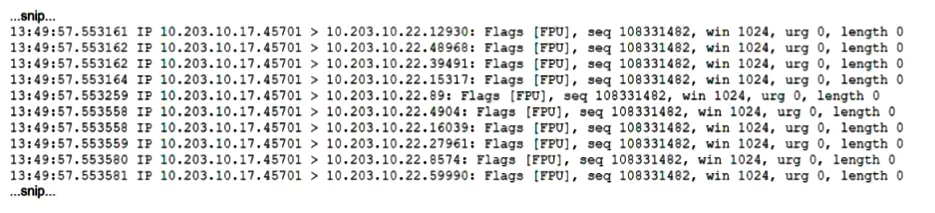
Which of the following activities explains the output?
Answer: A
While performing a dynamic analysis of a malicious file, a security analyst notices the memory address changes every time the process runs. Which of the following controls is most likely preventing the analyst from finding the proper memory address of the piece of malicious code?
Answer: A
An analyst finds that duplicate entries may exist in the asset inventory, which is skewing vulnerability scan data. Which of the following is the best way for the analyst to improve the effectiveness of the vulnerability scan?
Answer: A
A security analyst identifies a device on which different malware was detected multiple times even after the systems were scanned and cleaned several times. Which of the following actions would be most effective to ensure the device does not have residual malware?
Answer: B
A user is flagged for consistently consuming a high volume of network bandwidth over the past week. During the investigation, the security analyst finds traffic to the following websites:
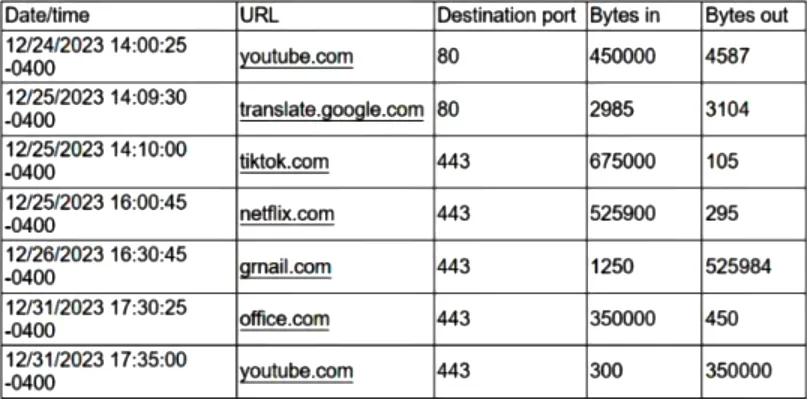
Which of the following data flows should the analyst investigate first?
Answer: D
After a series of UEBA alerts, a company’s SOC observes an extended period of suspicious outbound traffic all with the same destination. Which of the following steps of the cyber kill chain has this attack completed?
Answer: B
Security analysts can review the Windows Registry on endpoints to get insights into:
Answer: C
During an internal code review, software called “ACE” was discovered to have a vulnerability that allows the execution of arbitrary code. The vulnerability is in a legacy, third-party vendor resource that is used by the ACE software. ACE is used worldwide and is essential for many businesses in this industry. Developers informed the Chief Information Security Officer that removal of the vulnerability will take time. Which of the following is the first action to take?
Answer: D
Keyboard:J Kmove between questionsA–Dselect an answerRshow or hide the answer← →change page
CS0-003 practice, question 431. 527 questions available.
Version 1.0.0. How we source questions