Question 421 · 527 in bank
An analyst wants to detect outdated software packages on a server. Which of the following methodologies will achieve this objective?
Show answer
Answer: D
CompTIA Cybersecurity Analyst (CySA+)527 questions across 53 pages are complete and free, with no account or card.
527 questions in this bank
Free access · progress saved on this device
An analyst wants to detect outdated software packages on a server. Which of the following methodologies will achieve this objective?
Answer: D
A systems administrator receives several reports about emails containing phishing links. The hosting domain is always different, but the URL follows a specific pattern of characters. Which of the following is the best way for the administrator to find more messages that were not reported?
Answer: A
A security analyst receives an alert with the following packet capture attached:
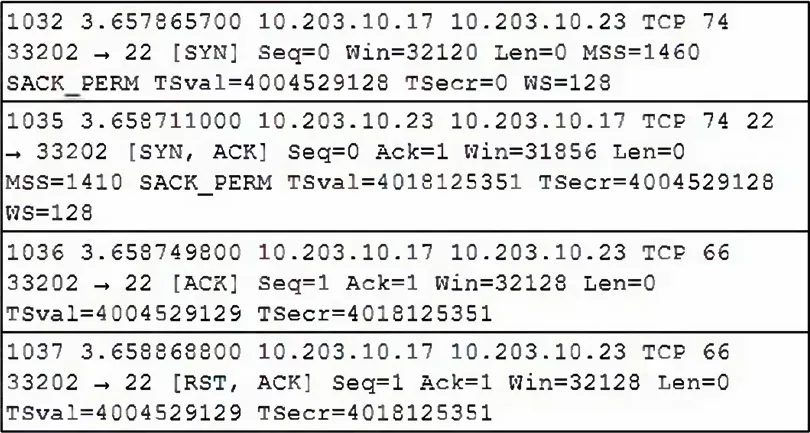
Which of the following has occurred?
Answer: C
A company runs a website that allows public posts. Recently, some users report that when visiting the website, pop-ups appear asking the users for their credentials. Which of the following is the most likely cause of this issue?
Answer: D
A security manager has decided to form a special group of analysts who participate in both penetration testing and defending the company's network infrastructure during exercises. Which of the following teams should the group form in order to achieve this goal?
Answer: B
Which of the following documents should link to the recovery point objectives and recovery time objectives on critical services?
Answer: B
A security analyst reviews the following output:
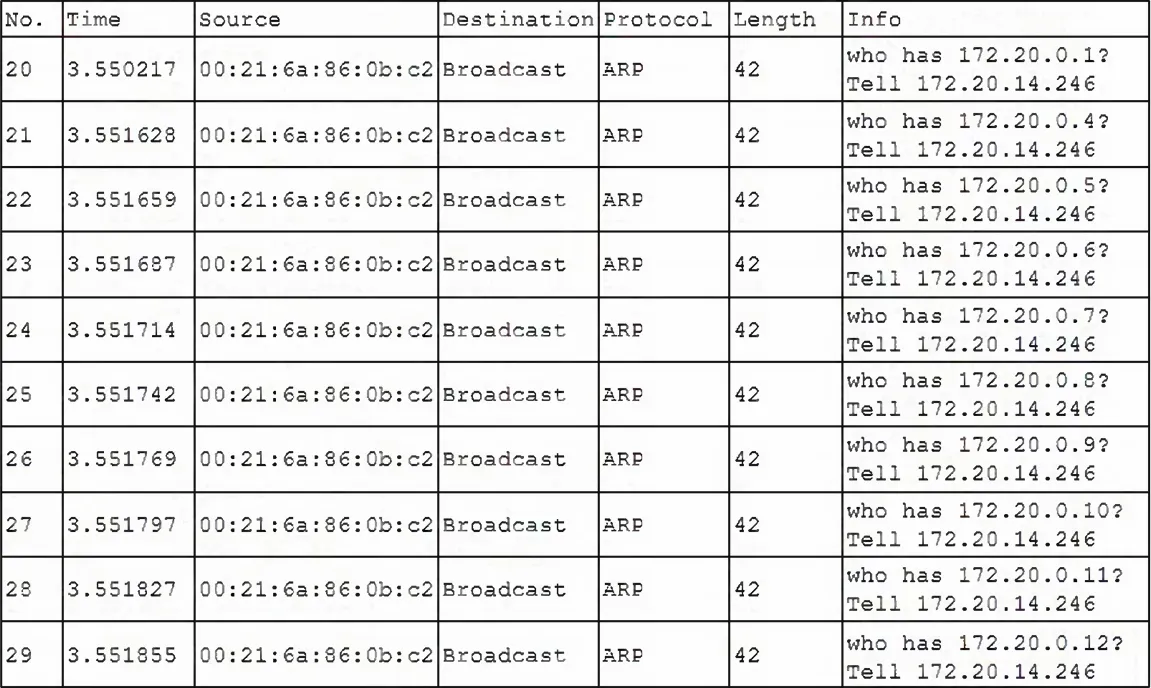
Which of the following malicious activities is occurring?
Answer: D
An e-commerce organization recently experienced a cyberattack. During a lessons learned meeting, a cybersecurity analyst requests that the RTO is prioritized. Which of the following is the greatest concern?
Answer: B
A security analyst reviews a SIEM alert related to a suspicious email and wants to verify the authenticity of the message: SPF = PASS - DKIM = FAIL - DMARC = FAIL - Which of the following did the analyst most likely discover?
Answer: B
An analyst is reviewing an SSLscan from a web server in an environment:
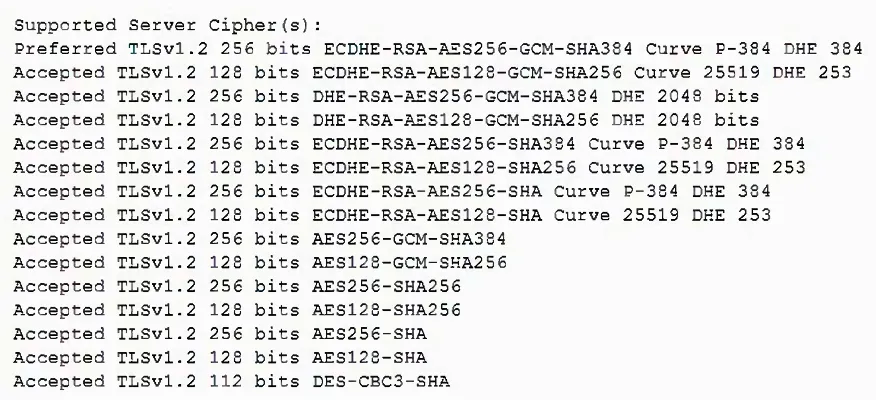
The analyst needs to immediately disable ciphers that do not comply with company security standards. Which of the following ciphers is the least secure and should be disabled?
Answer: E
Keyboard:J Kmove between questionsA–Dselect an answerRshow or hide the answer← →change page
CS0-003 practice, question 421. 527 questions available.
Version 1.0.0. How we source questions