Question 281 · 377 in bank
SIMULATION -

Guidelines - This is a lab item in which tasks will be performed on virtual devices. • Refer to the Tasks tab to view the tasks for this lab item. • Refer to the Topology tab to access the device console(s) and perform the tasks. • Console access is available for all required devices by clicking the device icon or using the tab(s) above the console window. • All necessary preconfigurations have been applied. • Do not change the enable password or hostname for any device. • Save your configurations to NVRAM before moving to the next item. • Click Next at the bottom of the screen to submit this lab and move to the next question. • When Next is clicked, the lab closes and cannot be reopened. Topology -
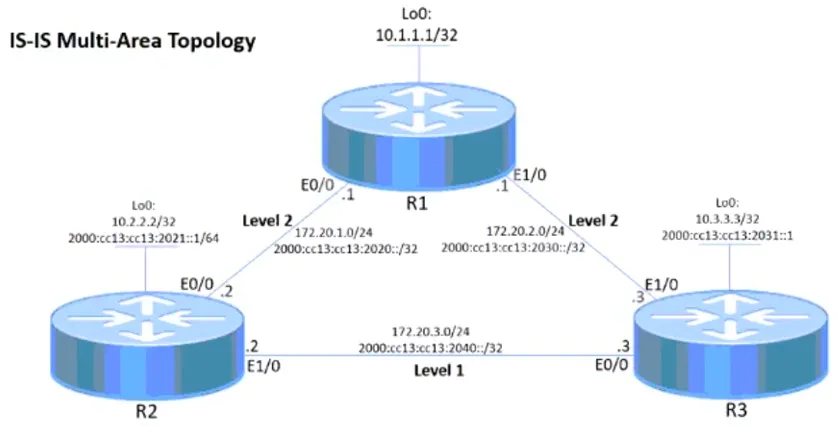
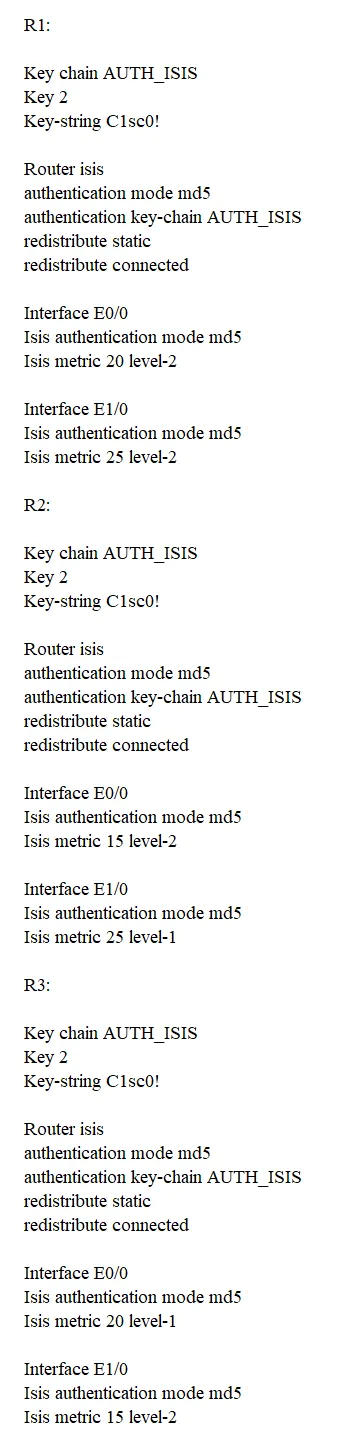
Tasks - Configure the IS-IS routing protocol for R1, R2, and R3 according to the topology to achieve these goals: 1. Configure HMAC-MD5 authentication for R1, R2, and R3 links that form the IS-IS adjacency using the ISIS commands on the interfaces using these parameters: • key-chain name: AUTH_ISIS • key ID: 2 • password: C1sc0! 2. Configure ISIS metric on R1, R2, and R3 to: • 15 for each level on all interfaces that form adjacency on router R1 • 20 for each level on all interfaces that form adjacency on router R2 • 25 for each level on all interface that form adjacency on R3 3. Configure IS-IS route redistribution for all static routes and connected interfaces on R1, R2, and R3.
This is an interactive task on the real exam — a drag-and-drop, hotspot or ordering question. There is nothing to select here, so the answer is shown below for reference.
Show the answer figure
Answer: See figure below
Explanation
The routers have IPv6 on their interfaces. We may want to add metric wide for IPv6 af. It will be something like this: router isis 1 net 49.0000.0000.0000.0001.00 metric-style wide log-adjacency-changes all ! address-family ipv6 multi-topology exit-address-family interface range E0/0 ip router isis 1 ipv6 router isis 1 Regarding the Authentication, it really depend on what type of authentication they are asking in the exam, it could be Hello Authentication or Domain authentication or Area/LSP authentication. https://www.cisco.com/c/en/us/support/docs/ip/integrated-intermediate-system-to-intermediate-system-is-is/13792-isis-authent.html
Source: Adapted from community discussion — EAS22