Question 1 · 88 in bank
Phishing belongs which of the following MITRE ATT&CK tactics?
Show answer
Answer: D
Palo Alto Networks Certified Detection and Remediation Analyst88 questions across 9 pages are complete and free, with no account or card.
88 questions in this bank
Free access · progress saved on this device
Phishing belongs which of the following MITRE ATT&CK tactics?
Answer: D
When viewing the incident directly, what is the “assigned to” field value of a new Incident that was just reported to Cortex?
Answer: C
from Admin Guide: Assigned To: The user to which the incident is assigned. The assignee tracks which analyst is responsible for investigating the threat. Incidents that have not been assigned have a status of Unassigned. https://docs-cortex.paloaltonetworks.com/r/Cortex-XDR/Cortex-XDR-Pro-Administrator-Guide/Incidents
Source: Adapted from community discussion — cneru1
In incident-related widgets, how would you filter the display to only show incidents that were “starred”?
Answer: D
Where would you view the WildFire report in an incident?
Answer: A
What does the following output tell us?
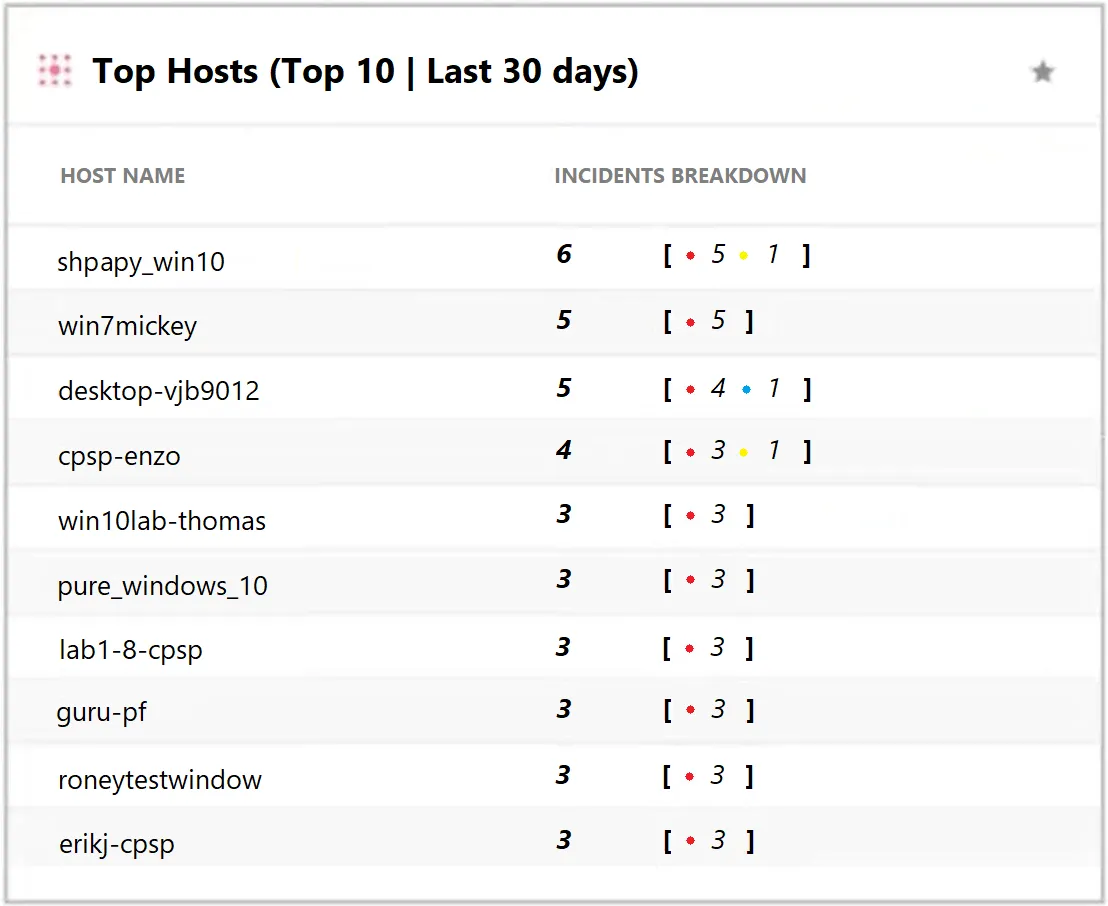
Answer: A
Which engine, of the following, in Cortex XDR determines the most relevant artifacts in each alert and aggregates all alerts related to an event into an incident?
Answer: B
From CXPAD: The Causality Analysis Engine determines the most relevant artifacts in each alert and aggregates all alerts related to an event into an incident.
Source: Adapted from community discussion — 9smiles
Which type of BIOC rule is currently available in Cortex XDR?
Answer: D
D is the only correct answer. Type of BIOC rule: Collection Credential Access Dropper Evasion Execution Evasive Exfiltration File Privilege Manipulation File Type Obfuscation Infiltration Lateral Movement Other Persistence Privilege Escalation Reconnaissance Tampering
Source: Adapted from community discussion — im2ca
In Windows and macOS you need to prevent the Cortex XDR Agent from blocking execution of a file based on the digital signer. What is one way to add an exception for the singer?
Answer: C
the correct option to prevent the Cortex XDR Agent from blocking the execution of a file based on the digital signer may vary depending on the specific version and configuration of the Cortex XDR Agent. However, based on the given options, the most appropriate choice would be: C. Add the signer to the allow list in the malware profile. By adding the digital signer to the allow list in the malware profile, you are essentially telling the Cortex XDR Agent to trust files signed by that specific signer and allow their execution without being blocked. It's worth noting that cybersecurity measures and software configurations can change over time, so it's essential to refer to the official documentation or the latest guidelines provided by the product's vendor for the most up-to-date information. Additionally, configuring security software requires careful consideration and should be performed by knowledgeable and authorized personnel to ensure the system's security.
Source: Adapted from community discussion — im2ca
As a Malware Analyst working with Cortex XDR you notice an alert suggesting that there was a prevented attempt to download Cobalt Strike on one of your servers. Days later, you learn about a massive ongoing supply chain attack. Using Cortex XDR you recognize that your server was compromised by the attack and that Cortex XDR prevented it. What steps can you take to ensure that the same protection is extended to all your servers?
Answer: A
Please provide a reference for your claim im2ca. I have not been able to find any supporting documentation for this. Probably you are talking about custom prevention rules, which are basically BIOC rules that you add to restriction profiles see [1], but BTP Rules are something else and their database is not available to the public [2]. [1]: https://docs-cortex.paloaltonetworks.com/r/Cortex-XDR/Cortex-XDR-Pro-Administrator-Guide/Create-a-BIOC-Rule [2]: https://live.paloaltonetworks.com/t5/cortex-xdr-discussions/about-behavioral-threat-protection-btp-rules/td-p/395977
Source: Adapted from community discussion — 9smiles
Which statement is true based on the following Agent Auto Upgrade widget?

Answer: B
Keyboard:J Kmove between questionsA–Dselect an answerRshow or hide the answer← →change page
PCDRA practice, question 1. 88 questions available.
Version 1.0.0. How we source questions