Question 151 · 394 in bank
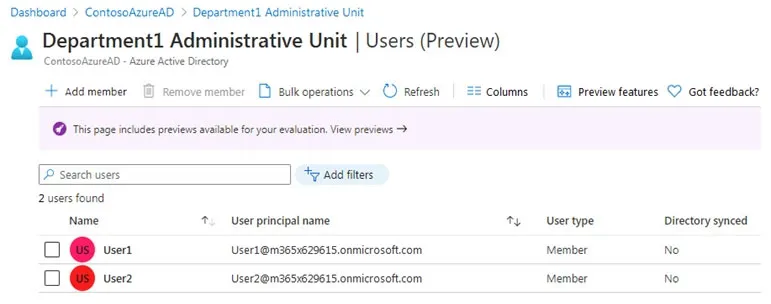
HOTSPOT - You have an Azure Active Directory (Azure AD) tenant that contains a group named Group3 and an administrative unit named Department1. Department1 has the users shown in the Users exhibit. (Click the Users tab.)
Department1 has the groups shown in the Groups exhibit. (Click the Groups tab.)

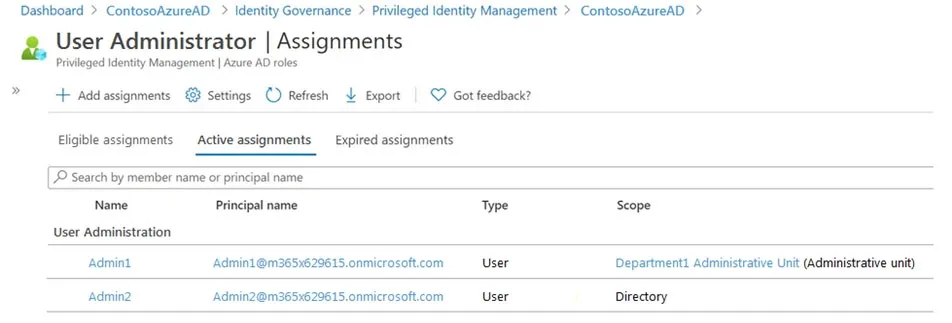
Department1 has the user administrator assignments shown in the Assignments exhibit. (Click the Assignments tab.)
The members of Group2 are shown in the Group2 exhibit. (Click the Group2 tab.)

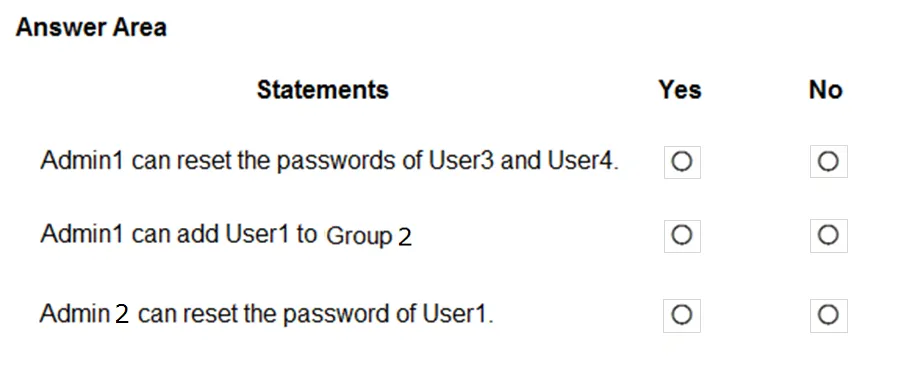
For each of the following statements, select Yes if the statement is true. Otherwise, select No. NOTE: Each correct selection is worth one point. Hot Area:
This is an interactive task on the real exam — a drag-and-drop, hotspot or ordering question. There is nothing to select here, so the answer is shown below for reference.
Show the answer figure
Answer: See figure below
Explanation
Admin1 and Admin2 are not members of Administrative group(Department1).However Admin1 has User administrator role scope for Department1 and Admin2 has User administrator role scope for the whole directory User 1 And User 2 are users of Department1 Group1(No members) and Group2(User 3 and User4 are members) are groups of Department1. FIrst Answer - NO Admin1 cannot reset the pwd for User 3 and User4 because they are part of group2.(User admin role assigned to admin unit cannot reset pwd of users present inside the group. Admin1 can reset the pwd of User1 and User2 who are not part of any groups inside the admin unit) Second Answer : YES Admin1 can add/remove users to the GROUPS present inside the admin unit(Admin1 cannot add/remove users from USERS section) Third Answer: YES Admin2 is User admin at directory scope ,hence can reset pwd of any uses except the pwd of global admin/higher power roles
Source: Adapted from community discussion — reddevil01