Question 111 · 277 in bank
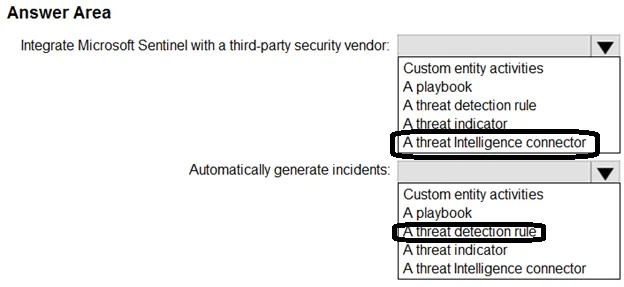
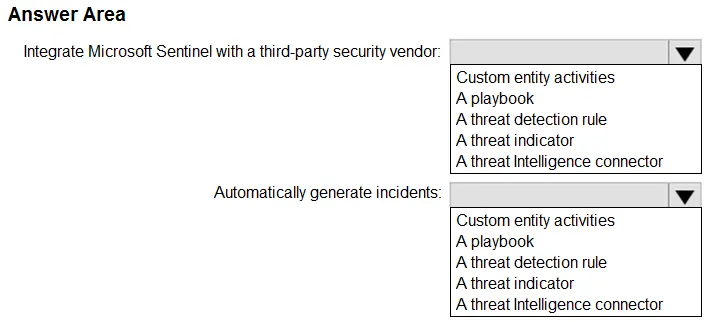
HOTSPOT - You have a Microsoft 365 subscription that is protected by using Microsoft 365 Defender. You are designing a security operations strategy that will use Microsoft Sentinel to monitor events from Microsoft 365 and Microsoft 365 Defender. You need to recommend a solution to meet the following requirements: • Integrate Microsoft Sentinel with a third-party security vendor to access information about known malware. • Automatically generate incidents when the IP address of a command-and-control server is detected in the events. What should you configure in Microsoft Sentinel to meet each requirement? To answer, select the appropriate options in the answer area. NOTE: Each correct selection is worth one point.
This is an interactive task on the real exam — a drag-and-drop, hotspot or ordering question. There is nothing to select here, so the answer is shown below for reference.
Show the answer figure
Answer: See figure below
Explanation
1. Threat Intelligence connector - Allow you to integrate Microsoft Sentinel with third-party security vendors to access information about known threats, such as malware and command-and-control servers. 2. Threat detection rule- Allow you to define conditions that, when met, will automatically generate an incident in Microsoft Sentinel. https://learn.microsoft.com/en-us/azure/sentinel/partner-integrations https://learn.microsoft.com/en-us/azure/sentinel/create-incidents-from-alerts
Source: Adapted from community discussion — Victory007