Question 171 · 383 in bank
You have a Hyper-V host. The host contains virtual machines that run Windows 10 as shown in following table.

Which virtual machines can be upgraded to Windows 11?
Show answer
Answer: B
Endpoint Administrator383 questions across 39 pages are complete and free, with no account or card.
383 questions in this bank
Free access · progress saved on this device
You have a Hyper-V host. The host contains virtual machines that run Windows 10 as shown in following table.
Which virtual machines can be upgraded to Windows 11?
Answer: B
You have a Microsoft 365 subscription that uses Microsoft Intune Suite. You use Intune to manage all devise. Users have iOS devices with Microsoft apps installed. You need to prevent users from cutting, copying, and pasting data between Microsoft Excel and other apps installed on the devices. What should you configure?
Answer: A
You have a Microsoft 365 subscription that uses Microsoft Intune Suite. You use Intune to manage devices. You need to review details about device wipes initiated through Intune. Which report should you review?
Answer: D
Looks correct When you go into Devices and choose a device, there is the Device Action Status at the bottom of the screen, which shows the status.....
Source: Adapted from community discussion — mp34
You have a Microsoft 365 subscription. The subscription contains 500 computers that run Windows 11 and are enrolled in Microsoft Intune. You need to manage the deployment of monthly security updates. The solution must meet the following requirements: • Updates must be deployed to a group of test computers for quality assurance. • Updates must be deployed automatically 15 days after the quality assurance testing. What should you create in the Microsoft Intune admin center?
Answer: D
D. an update ring Taking a ring approach will ensure that testing is performed in the company's Dev/QA environment(s), and final release will be made to the Production environment after 15 days after QA testing wraps up. .
Source: Adapted from community discussion — Merrybob
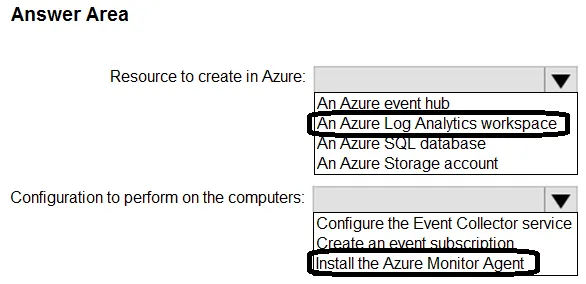
HOTSPOT - Your company has computers that run Windows 10 and are Microsoft Entra joined. The company purchases an Azure subscription. You need to collect Windows events from the Windows 10 computers in Azure. The solution must enable you to create alerts based on the collected events. What should you create in Azure and what should you configure on the computers? To answer, select the appropriate options in the answer area.
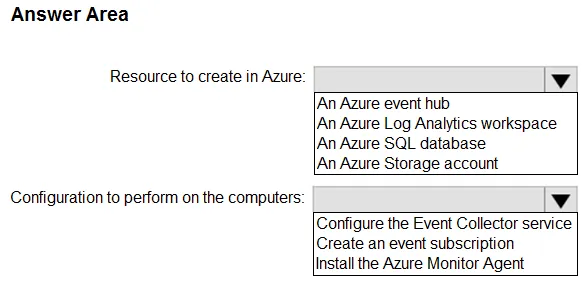
This is an interactive task on the real exam — a drag-and-drop, hotspot or ordering question. There is nothing to select here, so the answer is shown below for reference.
Answer: See figure below
Log analytics is correct for the first part, and to make that work on a computer you need to install the Agent, so the answer seems correct
Source: Adapted from community discussion — mp34
You have a Microsoft 365 subscription that contains 500 computers that run Windows 11. The computers are Azure AD joined and are enrolled in Microsoft Intune. You plan to manage Microsoft Defender Antivirus on the computers. You need to prevent users from disabling Microsoft Defender for Endpoint. What should you do?
Answer: B
To prevent users from disabling Microsoft Defender for Endpoint, you can use Group Policy to hide the Microsoft Defender Antivirus interface from users and prevent them from pausing scans 12. This will ensure that users cannot disable Microsoft Defender Antivirus on their endpoints. Therefore, the correct answer is B. From the Microsoft 365 Defender portal, enable tamper protection 3. Tamper protection is a feature that prevents malicious actors from disabling Microsoft Defender Antivirus and other security features on endpoints. It is available in Microsoft Defender for Endpoint Plan 1 and Plan 2 3. Option A is incorrect because attack surface reduction (ASR) policies are used to reduce the attack surface of an organization’s devices by blocking or restricting certain types of activities 1. Option C is incorrect because account protection policies are used to protect user accounts from unauthorized access 1. Option D is incorrect because Conditional Access policies are used to control access to cloud apps and services based on specific conditions 1. Bing AI said ...
Source: Adapted from community discussion — Krayzr
You have a Microsoft 365 subscription that has Windows 365 Enterprise licenses. You plan to use a custom Windows 11 image as a template for Cloud PCs. You have a Hyper-V virtual machine that runs Windows 11 and has the following configurations: • Name: VM1 • Disk size: 64 GB • Disk format: VHDX • Disk type: Fixed size • Generation: Generation 2 You need to ensure that you can use VM1 as a source for the custom image. What should you do on VM1 first?
Answer: B
To use VM1 as a source for the custom Windows 11 image on Windows 365, you should choose option B. Change the disk format to VHD. Microsoft 365 Windows 365 Cloud PCs typically use VHD (Virtual Hard Disk) format for virtual machine images. Therefore, converting the disk format from VHDX to VHD is necessary for compatibility.
Source: Adapted from community discussion — CaTa_LySt
HOTSPOT - Your on-premises network contains an Active Directory domain named contoso.com. The domain contains a user account named Admin1 and the resources shown in the following table.

You have a Microsoft 365 E5 subscription. You have a Microsoft Entra tenant that syncs with contoso.com. Admin1 plans to use Windows Autopilot to deploy 100 Windows 11 devices. The deployment must meet the following requirements: • The devices must be Microsoft Entra hybrid joined during the deployment. • Computer objects must be created in OU1. You need to configure Server1 and Active Directory delegation to support the deployment. NOTE: Each correct selection is worth one point.

This is an interactive task on the real exam — a drag-and-drop, hotspot or ordering question. There is nothing to select here, so the answer is shown below for reference.
Answer: See figure below
broh.. have you ever done it before? you should try by yourself. Install the Intune connector on server 1, delegate server 1 upon ou1
Source: Adapted from community discussion — RazielLycas

You have a Microsoft 365 E5 subscription. The subscription contains 25 computers that run Windows 11 and are enrolled in Microsoft Intune. You need to onboard the devices to Microsoft Defender for Endpoint. What should you create in the Microsoft Intune admin center?
Answer: C
To onboard devices to Microsoft Defender for Endpoint using Microsoft Intune, you should create an endpoint detection and response (EDR) policy. This policy is specifically designed to configure and manage endpoint detection and response capabilities, including onboarding devices to Microsoft Defender for Endpoint. Therefore, the correct answer is: C. an endpoint detection and response (EDR) policy
Source: Adapted from community discussion — veliyath
You have a Microsoft 365 subscription. Each user is assigned a Windows 365 Enterprise license. You need to deploy Cloud PCs that will be Microsoft Entra hybrid joined. What should you do first?
Answer: A
"Microsoft Entra hybrid joined devices require network line of sight to your domain controllers periodically. Without this connection, devices become unusable." This is a prereq, so that must be the first thing to do https://learn.microsoft.com/en-us/entra/identity/devices/hybrid-join-plan
Source: Adapted from community discussion — Soest009
Keyboard:J Kmove between questionsA–Dselect an answerRshow or hide the answer← →change page
MD-102 practice, question 171. 383 questions available.
Version 1.0.0. How we source questions