Question 301 · 462 in bank
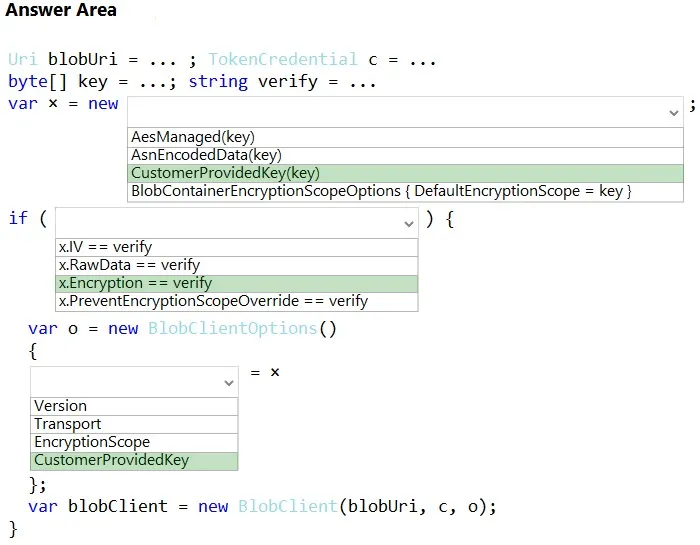
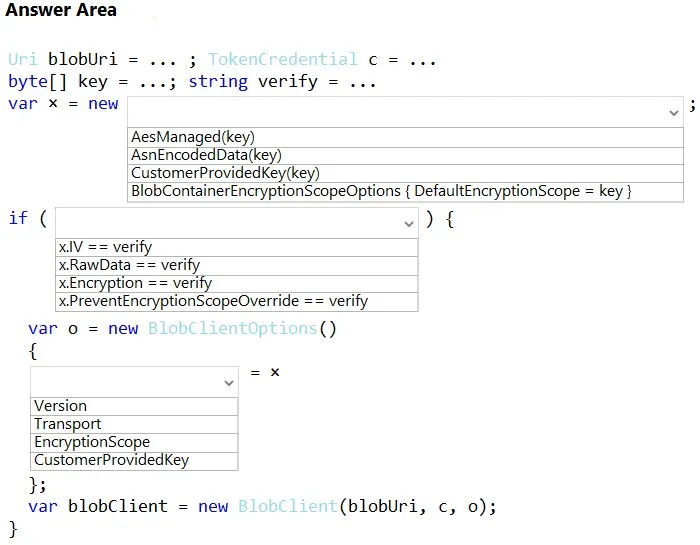
HOTSPOT - You are building an application that stores sensitive customer data in Azure Blob storage. The data must be encrypted with a key that is unique for each customer. If the encryption key has been corrupted it must not be used for encryption. You need to ensure that the blob is encrypted. How should you complete the code segment? To answer, select the appropriate options in the answer area. NOTE: Each correct selection is worth one point. Hot Area:
This is an interactive task on the real exam — a drag-and-drop, hotspot or ordering question. There is nothing to select here, so the answer is shown below for reference.
Show the answer figure
Answer: See figure below
Explanation
Box 1: CustomerProvidedKey(key) The data must be encrypted with a key that is unique for each customer. Sample code: async static Task UploadBlobWithClientKey(Uri blobUri, Stream data, byte[] key, string keySha256) { // Create a new customer-provided key. // Key must be AES-256. var cpk = new CustomerProvidedKey(key); Box 2: Encryption - CustomerProvidedKey.EncryptionKey Property Sample code continued: // Check the key's encryption hash. if (cpk.EncryptionKeyHash != keySha256) { throw new InvalidOperationException("The encryption key is corrupted."); } Box 3: CustomerProvidedKey - Sample code continued; // Specify the customer-provided key on the options for the client. BlobClientOptions options = new BlobClientOptions() { CustomerProvidedKey = cpk - }; // Create the client object with options specified. BlobClient blobClient = new BlobClient( blobUri, new DefaultAzureCredential(), options); Incorrect: * Version - Gets the BlobClientOptions.ServiceVersion of the service API used when making requests. Transport - The HttpPipelineTransport to be used for this client. Reference: https://docs.microsoft.com/en-us/azure/storage/blobs/storage-blob-customer-provided-key
Source: Adapted from community discussion — Ciupaz
References