Question 291 · 339 in bank
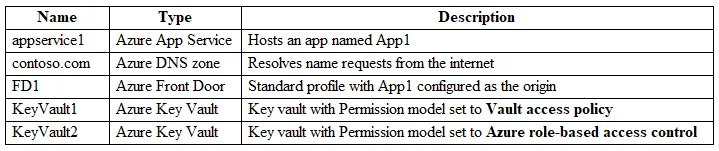
You have an Azure subscription that contains the resources shown in the following table.

You need to ensure that VM1 and VM2 can connect only to storage1. The solution must meet the following requirements: • Prevent VM1 and VM2 from accessing any other storage accounts • Ensure that storage1 is accessible from the internet. What should you use?
Show answer
Answer: B
Explanation
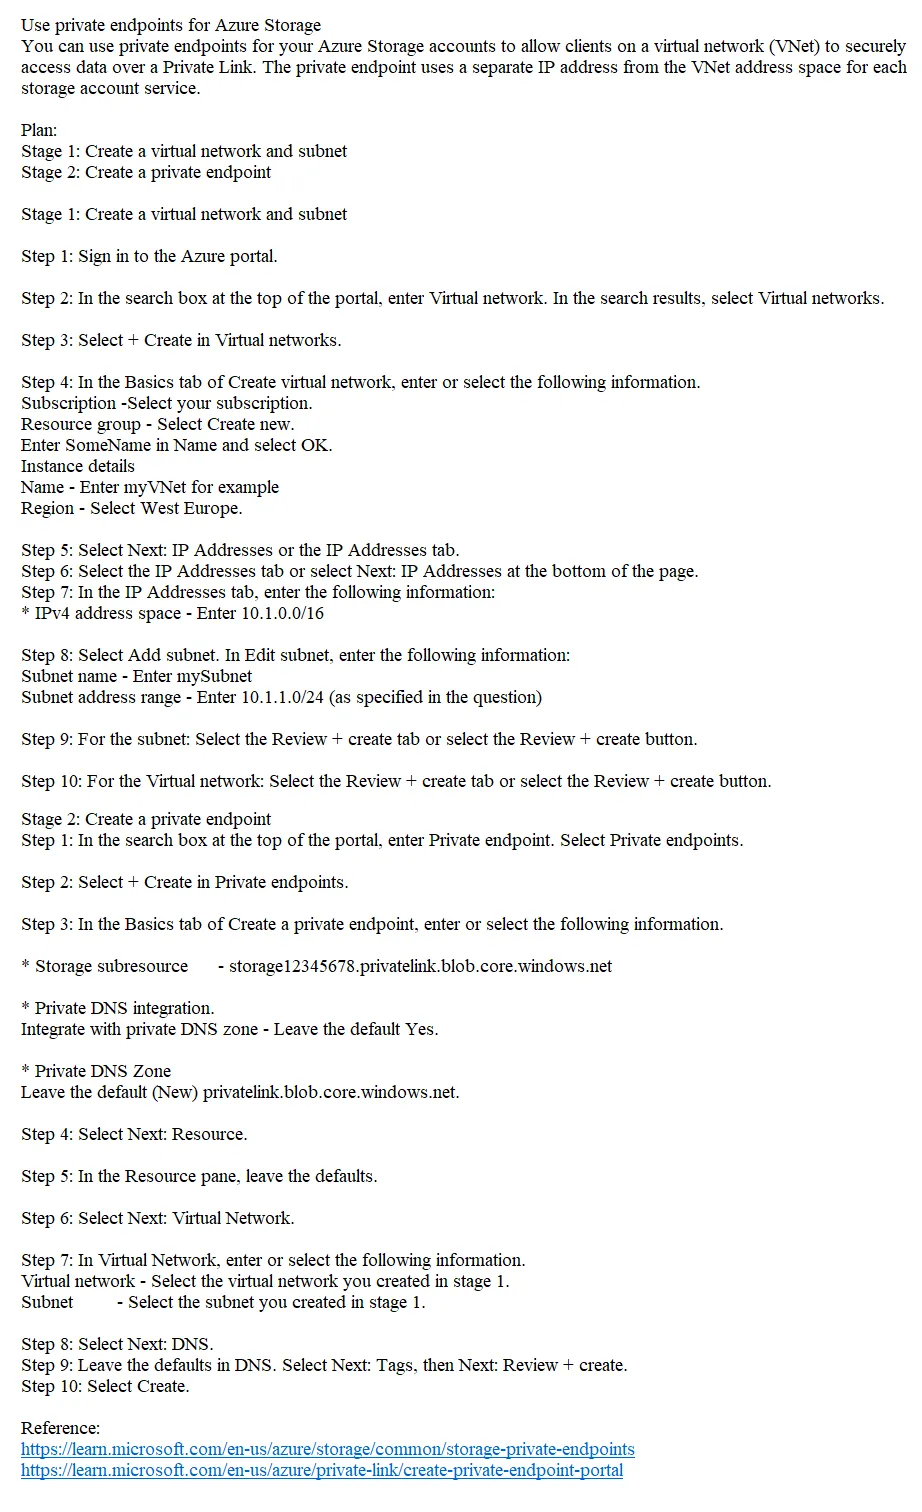
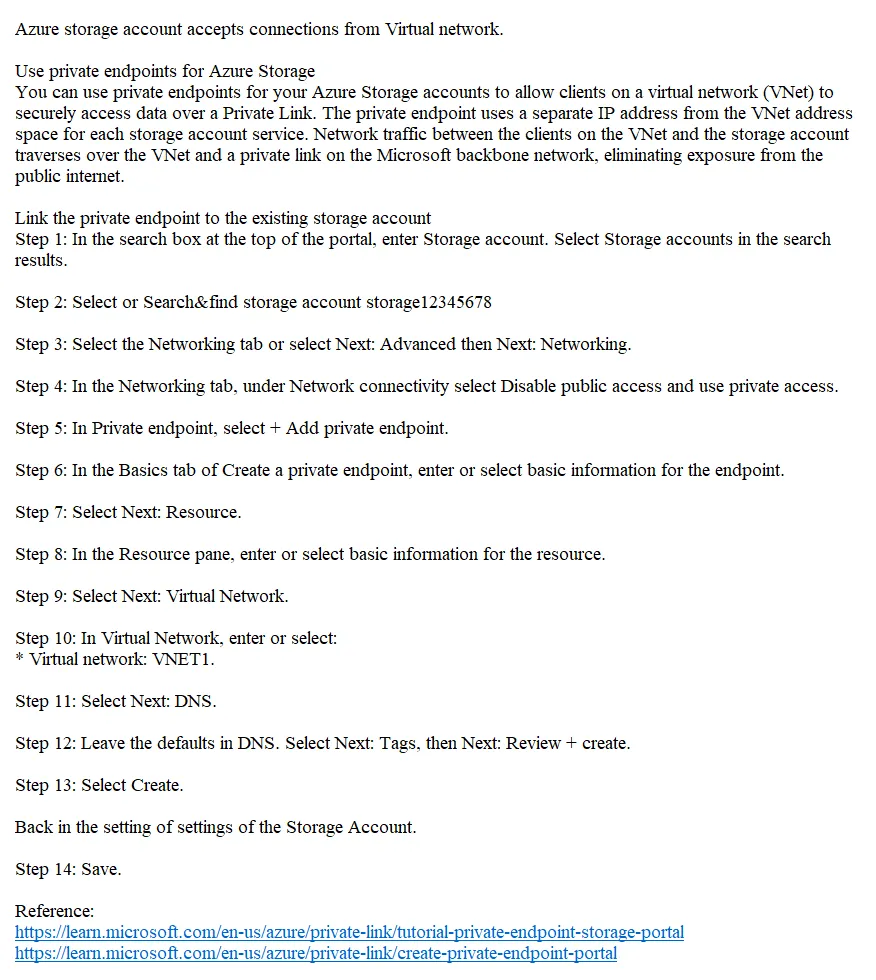
B. a service endpoint policy A service endpoint policy can be used to control the access to Azure Storage accounts from virtual networks. By creating a service endpoint policy, you can specify which storage accounts are allowed to be accessed from the virtual network, while blocking access to other storage accounts. In this case, you can create a service endpoint policy that allows access to storage1 and associate it with the virtual network containing VM1 and VM2. This will ensure that VM1 and VM2 can only connect to storage1 and will be prevented from accessing any other storage accounts. Additionally, to ensure that storage1 is accessible from the internet, you can configure the storage account's networking settings to allow public access. This can be done by enabling the appropriate settings such as allowing public access to blobs or enabling a public endpoint. Using a network security group (NSG) would not provide the required granular control over specific storage accounts. A private link or private endpoint would enable private access to the storage account but would not allow access from the internet, which is a requirement in this scenario. Therefore, the best option is to use a service endpoint policy.
Source: Adapted from community discussion — roshingrg