Question 31 · 88 in bank
Examine the command below. Output has been trimmed.
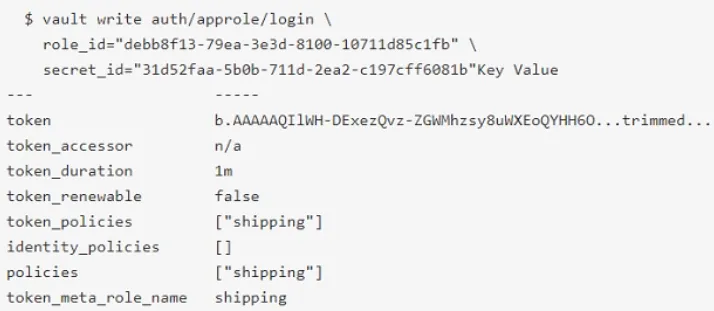
Which of the following statements describe the command and its output?
Show answer
Answer: D
HashiCorp Certified: Vault Associate (002)88 questions across 9 pages are complete and free, with no account or card.
88 questions in this bank
Free access · progress saved on this device
Examine the command below. Output has been trimmed.
Which of the following statements describe the command and its output?
Answer: D
You have a 2GB Base64 binary large object (blob) that needs to be encrypted. Which of the following best describes the transit secrets engine?
Answer: A
The key/value v2 secrets engine is enabled at secret/. See the following policy:

Which of the following operations are permitted by this policy? (Choose two.)
Answer: AB
The KV Put and KV Get operations require the read, create, and update capabilities granted in the first part of the policy so A & B are correct. Metadata is not one of the listed capabilities in the first section of the policy so C is wrong. The deny in the second part of the policy prevents D & E.
Source: Adapted from community discussion — daz_rekka
You are performing a high number of authentications in a short amount of time. You're experiencing slow throughput for token generation. How would you solve this problem?
Answer: B
When looking at Vault token details, which key helps you find the paths the token is able to access?
Answer: C
A developer mistakenly committed code that contained AWS S3 credentials into a public repository. You have been tasked with revoking the AWS S3 credential that was in the code. This credential was created using Vault’s AWS secrets engine and the developer received the following output when requesting a credential from Vault.

Which Vault command will revoke the lease and remove the credential from AWS?
Answer: A
When an auth method is disabled, all users authenticated via that method lose access.
Answer: A
An authentication method should be selected for a use case based on:
Answer: A
A web application uses Vault’s transit secrets engine to encrypt data in-transit. If an attacker intercepts the data in transit, which of the following statements are true? (Choose two.)
Answer: BC
The Vault encryption key is stored in Vault’s backend storage.
Answer: A
Vault stores it's own encryption key in it's own storage backend. The root key created during the Unseal step is the key to decrypt that key and not known to Vault or kept in the Storage Backend by design. https://developer.hashicorp.com/vault/docs/concepts/seal#why
Source: Adapted from community discussion — daz_rekka
Keyboard:J Kmove between questionsA–Dselect an answerRshow or hide the answer← →change page
VA-002 practice, question 31. 88 questions available.
Version 1.0.0. How we source questions