Question 11 · 61 in bank
How does the Syslog-based single sign-on (SSO) feature in FortiAuthenticator function to correlate user activity with authentication events across multiple network devices?
Show answer
Answer: A
Fortinet NSE 6 - LAN Edge 7.6 Architect61 questions across 7 pages are complete and free, with no account or card.
61 questions in this bank
Free access · progress saved on this device
How does the Syslog-based single sign-on (SSO) feature in FortiAuthenticator function to correlate user activity with authentication events across multiple network devices?
Answer: A
In a Windows environment using AD machine authentication, how does FortiAuthenticator ensure that a previously authenticated device is maintaining its network access once the device resumes operating after sleep or hibernation?
Answer: B
You are troubleshooting an issue where users are being intermittently redirected to an error page after submitting their login credentials on a captive portal. As part of your troubleshooting steps, you review the POST parameters sent from the client to the authentication server. What should you check in the magic ID within the POST parameters to help resolve the issue?
Answer: C
You need to deploy FortiAPs at remote locations and want to avoid high latency by minimizing interference from FortiGate. Which SSID traffic mode is best suited for this deployment?
Answer: C
In which two ways is layer 2 isolation applied to a quarantined device? (Choose two.)
Answer: BE
When troubleshooting a FortLink connectivity issue between FortiGate and FortiSwitch, why is it important to verify their time and date settings?
Answer: A
A network administrator is configuring a RADIUS server on FortiGate to authenticate remote users. The administrator configures FortiGate to forward authentication requests to FortiAuthenticator, which then proxies these requests to a Windows Active Directory (AD) server using LDAP. Which is the primary benefit of using FortiAuthenticator in this configuration?
Answer: B
A network administrator is deploying a new FortiGate firewall and wants to enable zero-touch provisioning with FortiManager. The administrator has not manually configured the FortiManager IP address or FQDN on FortiGate. However, FortiGate can still discover FortiManager automatically. In this situation, where can FortiGate learn the FortiManager IP address or FQDN for zero-touch provisioning?
Answer: A
What is the primary purpose of configuring an untagged VLAN on a FortiSwitch port in a network deployment?
Answer: A
Refer to the exhibits.

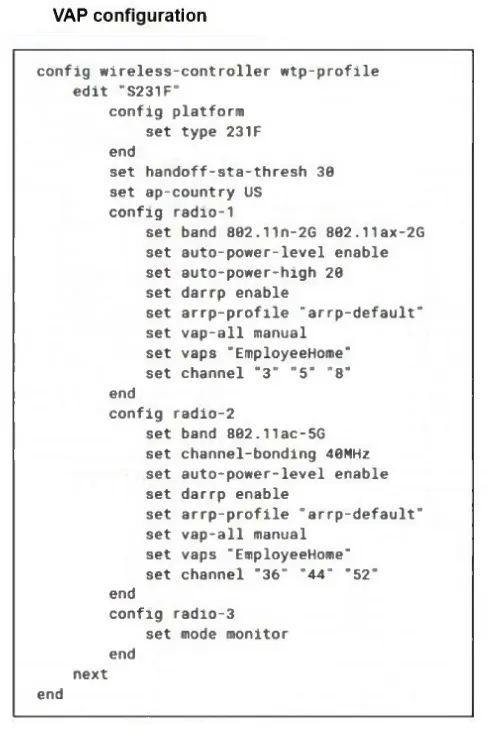
The exhibits show the WTP profile and VAP CLI configurations on FortiGate managing a remote AP. The AP is designed to grant a remote employee access to company network resources, including the database and AD servers. The employee can reach company resources but is unable to access a local printer at home. What two solutions are required to fix this issue? (Choose two.)
Answer: AD
Keyboard:J Kmove between questionsA–Dselect an answerRshow or hide the answer← →change page
FCSS_LED_AR-7.6 practice, question 11. 61 questions available.
Version 1.0.0. How we source questions