Question 1 · 10 in bank
When selecting multiple rules at once on FortiSIEM, which actions can you perform?
Show answer
Answer: A
Fortinet NSE 6 - FortiSIEM 7.4 Analyst10 questions across 1 page are complete and free, with no account or card.
10 questions in this bank
Free access · progress saved on this device
When selecting multiple rules at once on FortiSIEM, which actions can you perform?
Answer: A
Refer to the exhibit. The configuration for a machine learning (ML) dataset using anomaly detection is shown.

If data for this model is generated every hour, how long must the FortiSIEM device be up before it can produce a valid training set?
Answer: B
Rules on FortiSIEM are usually processed as events are collected (streaming). How can you create a rule to evaluate events over an 8-hour period?
Answer: D
Which two categories can you map to the MITRE ATT&CK coverage tables on FortiSIEM? (Choose two.)
Answer: AC
What are two required components in a rule? (Choose two.)
Answer: AB
You need a model that predicts a target field based on other fields in a dataset and then triggers an anomaly if the value does not match the prediction. Which machine learning (ML) algorithm will you use to build this type of model?
Answer: A
You want to create a rule with multiple subpatterns but trigger an incident only if three different subpatterns are matched over a 24-hour period. Where must you define the time period that the rule uses to evaluate all the subpatterns?
Answer: B
Refer to the exhibit.
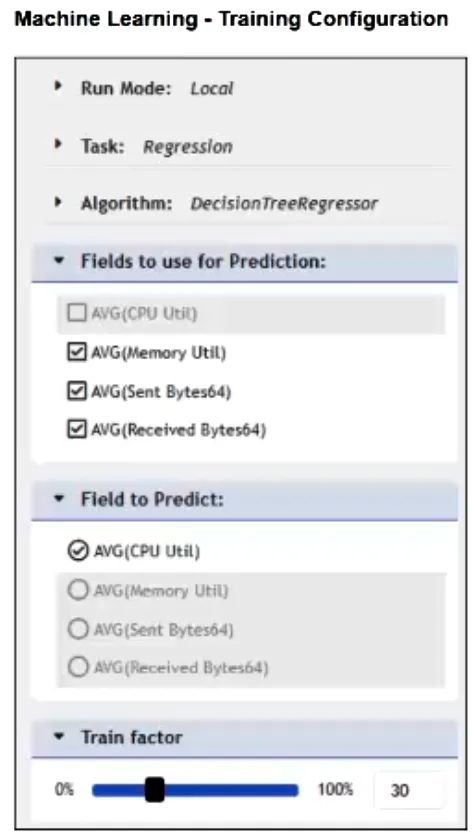
An incorrect configuration is shown. Which setting must you change to successfully apply this configuration to FortiSIEM?
Answer: C
Which two ways are rule tags used on FortiSIEM? (Choose two.)
Answer: AB
What are four incident status options on FortiSIEM?
Answer: D
Keyboard:J Kmove between questionsA–Dselect an answerRshow or hide the answer← →change page
NSE6_FSM_AN-7.4 practice, question 1. 10 questions available.
Version 1.0.0. How we source questions