Question 1 · 62 in bank
Refer to the exhibit.
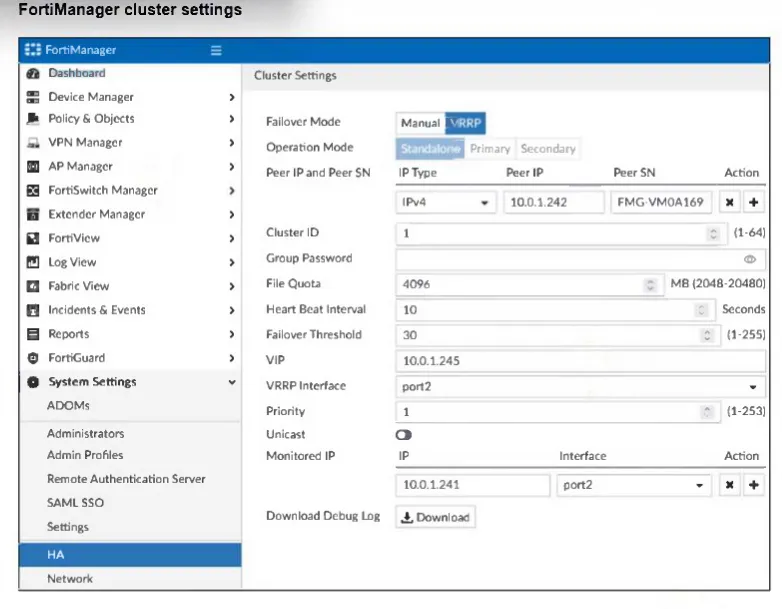
If the monitored interface for the primary FortiManager device fails, what must you do to maintain high availability (HA)?
Show answer
Answer: A
Fortinet NSE 5 - FortiManager 7.6 Administrator62 questions across 7 pages are complete and free, with no account or card.
62 questions in this bank
Free access · progress saved on this device
Refer to the exhibit.
If the monitored interface for the primary FortiManager device fails, what must you do to maintain high availability (HA)?
Answer: A
Refer to the exhibit.
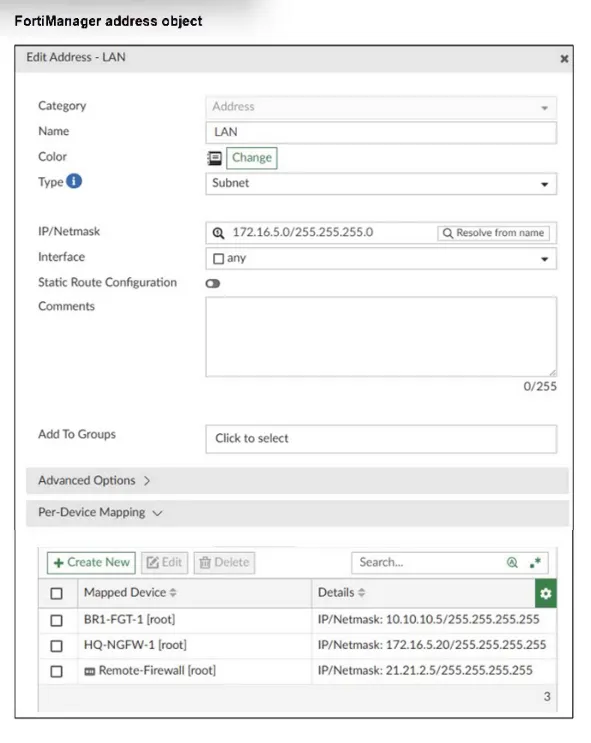
An administrator has created a firewall address object that is used in multiple policy packages for multiple FortiGate devices in an ADOM. After the installation operation is performed, which IP/netmask will be installed on Remote-Firewall [VDOM1] for the LAN firewall address object?
Answer: C
You want to let multiple administrators work in the same ADOM without creating configuration conflicts. What is the best and the most effective solution to apply?
Answer: D
Refer to the exhibits.
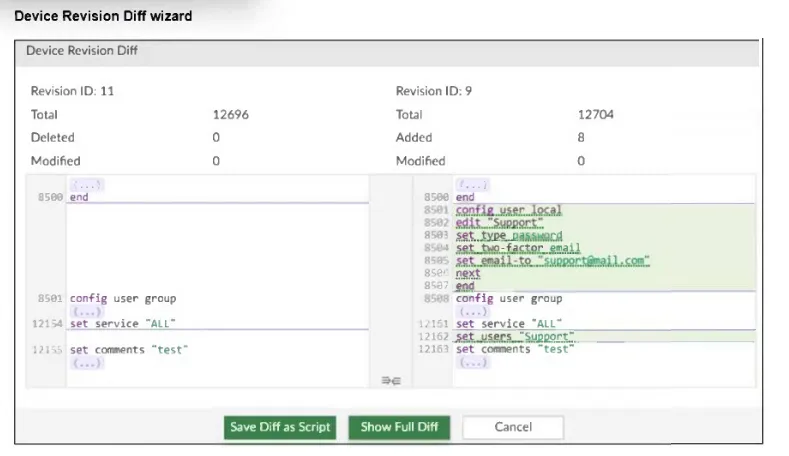

An administrator needed to recover all the configurations related to the user, Support. The configurations were saved in configuration revision ID 9. The administrator reverted the configuration using the Configuration Revision History window and received the CLI output shown in the exhibit. What can you conclude from the CLI output?
Answer: D
An administrator wants to configure and manage multiple objects in the FortiManager database and give access to other users who work in the same database. To stay in control of the changes made to firewall policies by other team members, the administrator needs a setup where all modifications go through a central check before they can be installed. How can the administrator create this setup?
Answer: D
Which two conditions trigger FortiManager to create a new revision history? (Choose two.)
Answer: AC
Refer to the exhibits.
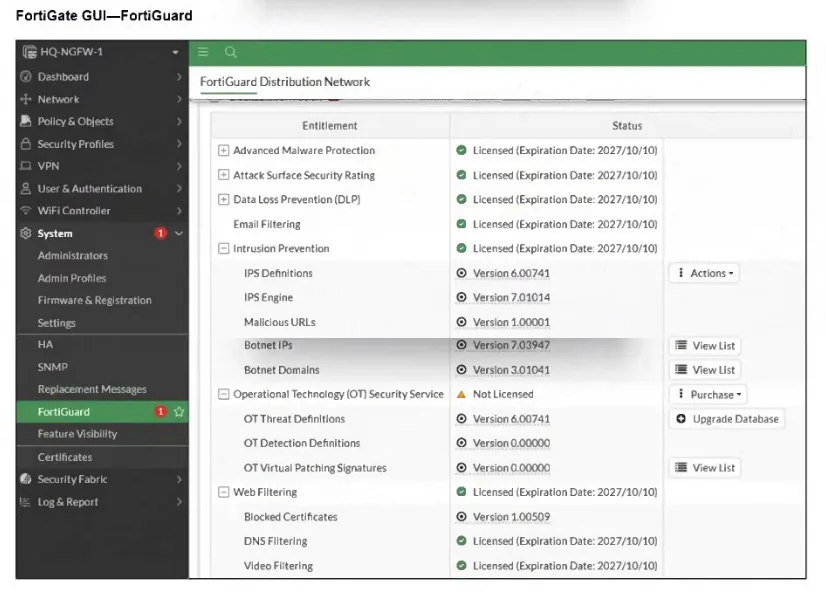
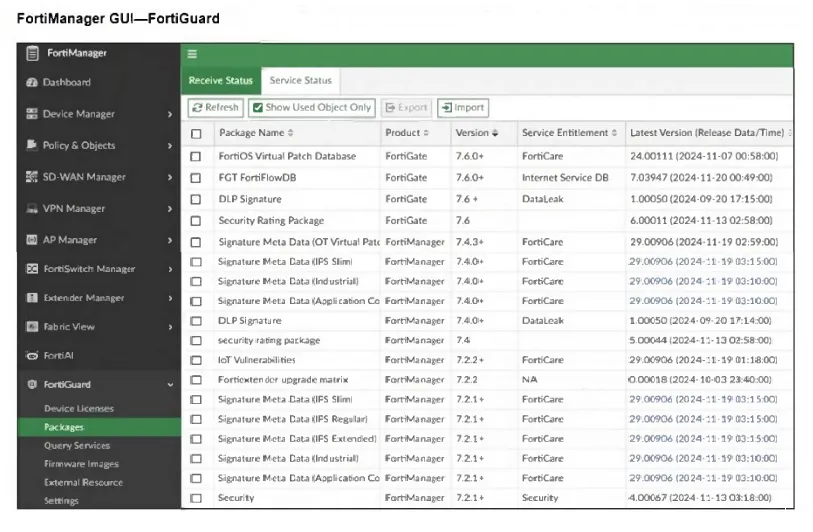

FortiGate HQ-NGFW-1 downloads and validates FortiGuard databases from FortiManager which acts as a local FortiGuard Distribution Server (FDS) in a closed network. An administrator pushes a new firewall policy with an intrusion prevention system (IPS) profile from FortiManager to FortiGate HQ- NGFW-1 However, FortiGate does not recognize the new IPS signature from FortiManager. What is the most likely reason why FortiGate HQ-NGFW-1 does not recognize the new IPS signature?
Answer: B
An administrator has assigned a global policy package to a new ADOM named ADOM1. What will happen if the administrator tries to create a new policy package in ADOM1?
Answer: B
Which is recommended when you are managing a high volume of logs in your network?
Answer: B
What is the best explanation of how FortiManager helps with mass provisioning?
Answer: C
Keyboard:J Kmove between questionsA–Dselect an answerRshow or hide the answer← →change page
FCP_FMG_AD-7.6 practice, question 1. 62 questions available.
Version 1.0.0. How we source questions