Question 51 · 78 in bank
Refer to the exhibit.

What can you conclude from the log shown in the exhibit?
Show answer
Answer: A
Fortinet NSE 4 - FortiOS 7.6 Administrator78 questions across 8 pages are complete and free, with no account or card.
78 questions in this bank
Free access · progress saved on this device
Refer to the exhibit.
What can you conclude from the log shown in the exhibit?
Answer: A
Refer to the exhibit.
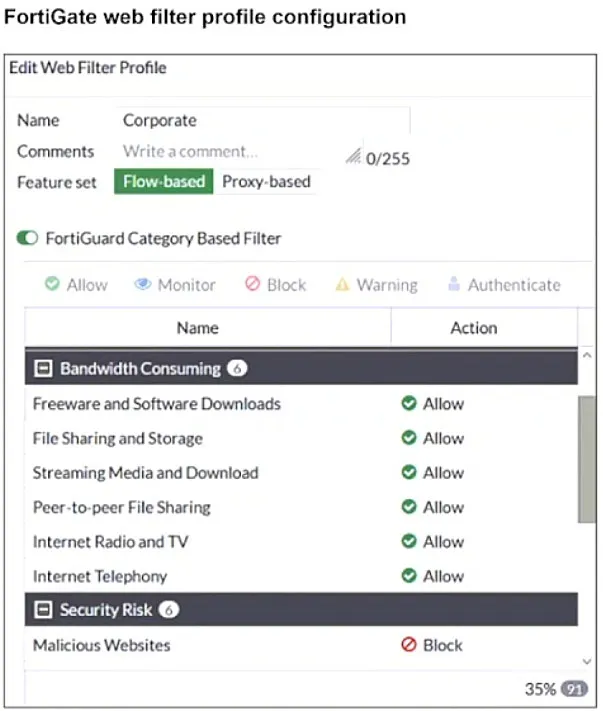
The exhibit shows the FortiGuard Category Based Filter section of a corporate web filter profile. An administrator must block access to download.com, which belongs to the Freeware and Software Downloads category. The administrator must also allow other websites in the same category. What are two solutions for satisfying the requirement? (Choose two.)
Answer: AB
Which two statements are true about an HA cluster? (Choose two.)
Answer: AD
Refer to the exhibit. An intrusion prevention system (IPS) profile signature setting is shown.

What can you conclude about the signature when adding the FTP.Login.Failed signature to the IPS Sensor profile?
Answer: C
Which three strategies are valid SD-WAN rule strategies for member selection? (Choose three.)
Answer: ACD
A network administrator enabled antivirus and selected an SSL inspection profile on a firewall policy. When downloading an EICAR test file through HTTP, FortiGate detects the virus and blocks the file. When downloading the same file through HTTPS, FortiGate does not detect the virus and does not block the file, allowing it to be downloaded. The administrator confirms that the traffic matches the configured firewall policy. What are two reasons for the failed virus detection by FortiGate? (Choose two.)
Answer: AC
Refer to the exhibits.


The exhibits show a diagram of a FortiGate device connected to the network, and the firewall policies, VIP, and IP pool configurations on the FortiGate device. The WAN (port2) interface has the IP address 100.65.0.101/24. The LAN (port4) interface has the IP address 10.0.11.254/24. The first firewall policy has NAT enabled using the IP pool. The second firewall policy is configured with a VIP as the destination address. Which IP address will be used to source NAT (SNAT) the internet traffic coming from a workstation with the IP address 10.0.11.50?
Answer: B
Refer to the exhibit, which shows a partial configuration from the remote authentication server.

Why does the FortiGate administrator need this configuration?
Answer: A
Refer to the exhibits.


An administrator configured the Web Filter Profile to block access to all social networking sites except Facebook. However, when users try to access Facebook.com, they are redirected to a FortiGuard web filtering block page. Based on the exhibits, which configuration change must the administrator make to allow Facebook while blocking all other social networking sites?
Answer: C
What is the primary FortiGate election process when the HA override setting is enabled?
Answer: C
Keyboard:J Kmove between questionsA–Dselect an answerRshow or hide the answer← →change page
NSE4_FGT_AD-7.6 practice, question 51. 78 questions available.
Version 1.0.0. How we source questions